Splunk: Exploring SPL (TryHackMe)
Link to the challenge on TryHackMe: Splunk: Exploring SPL
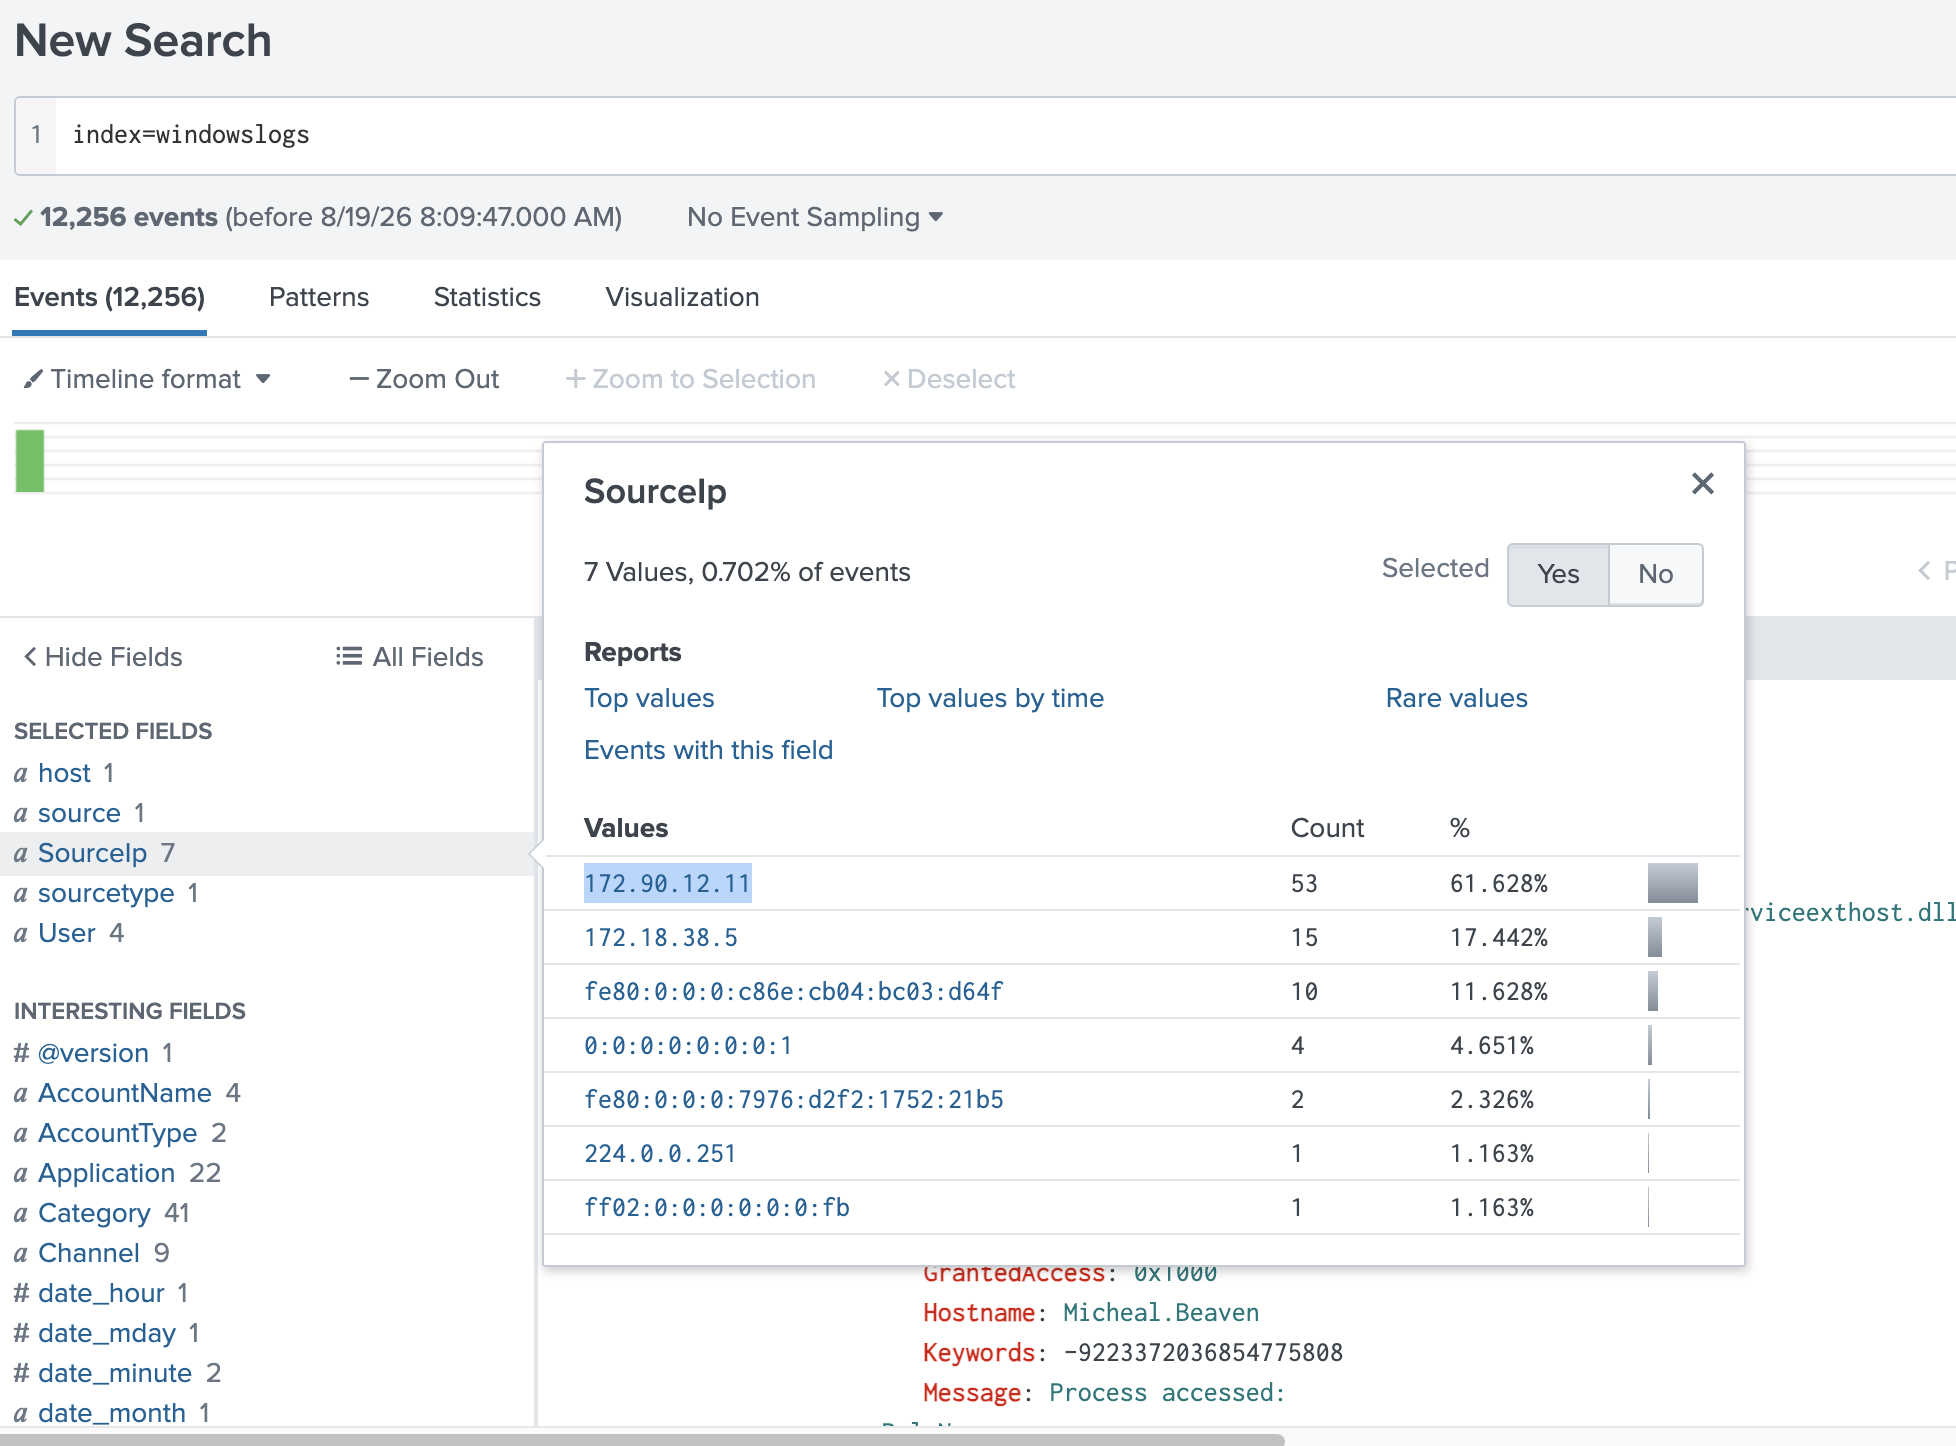
index=windowslogs
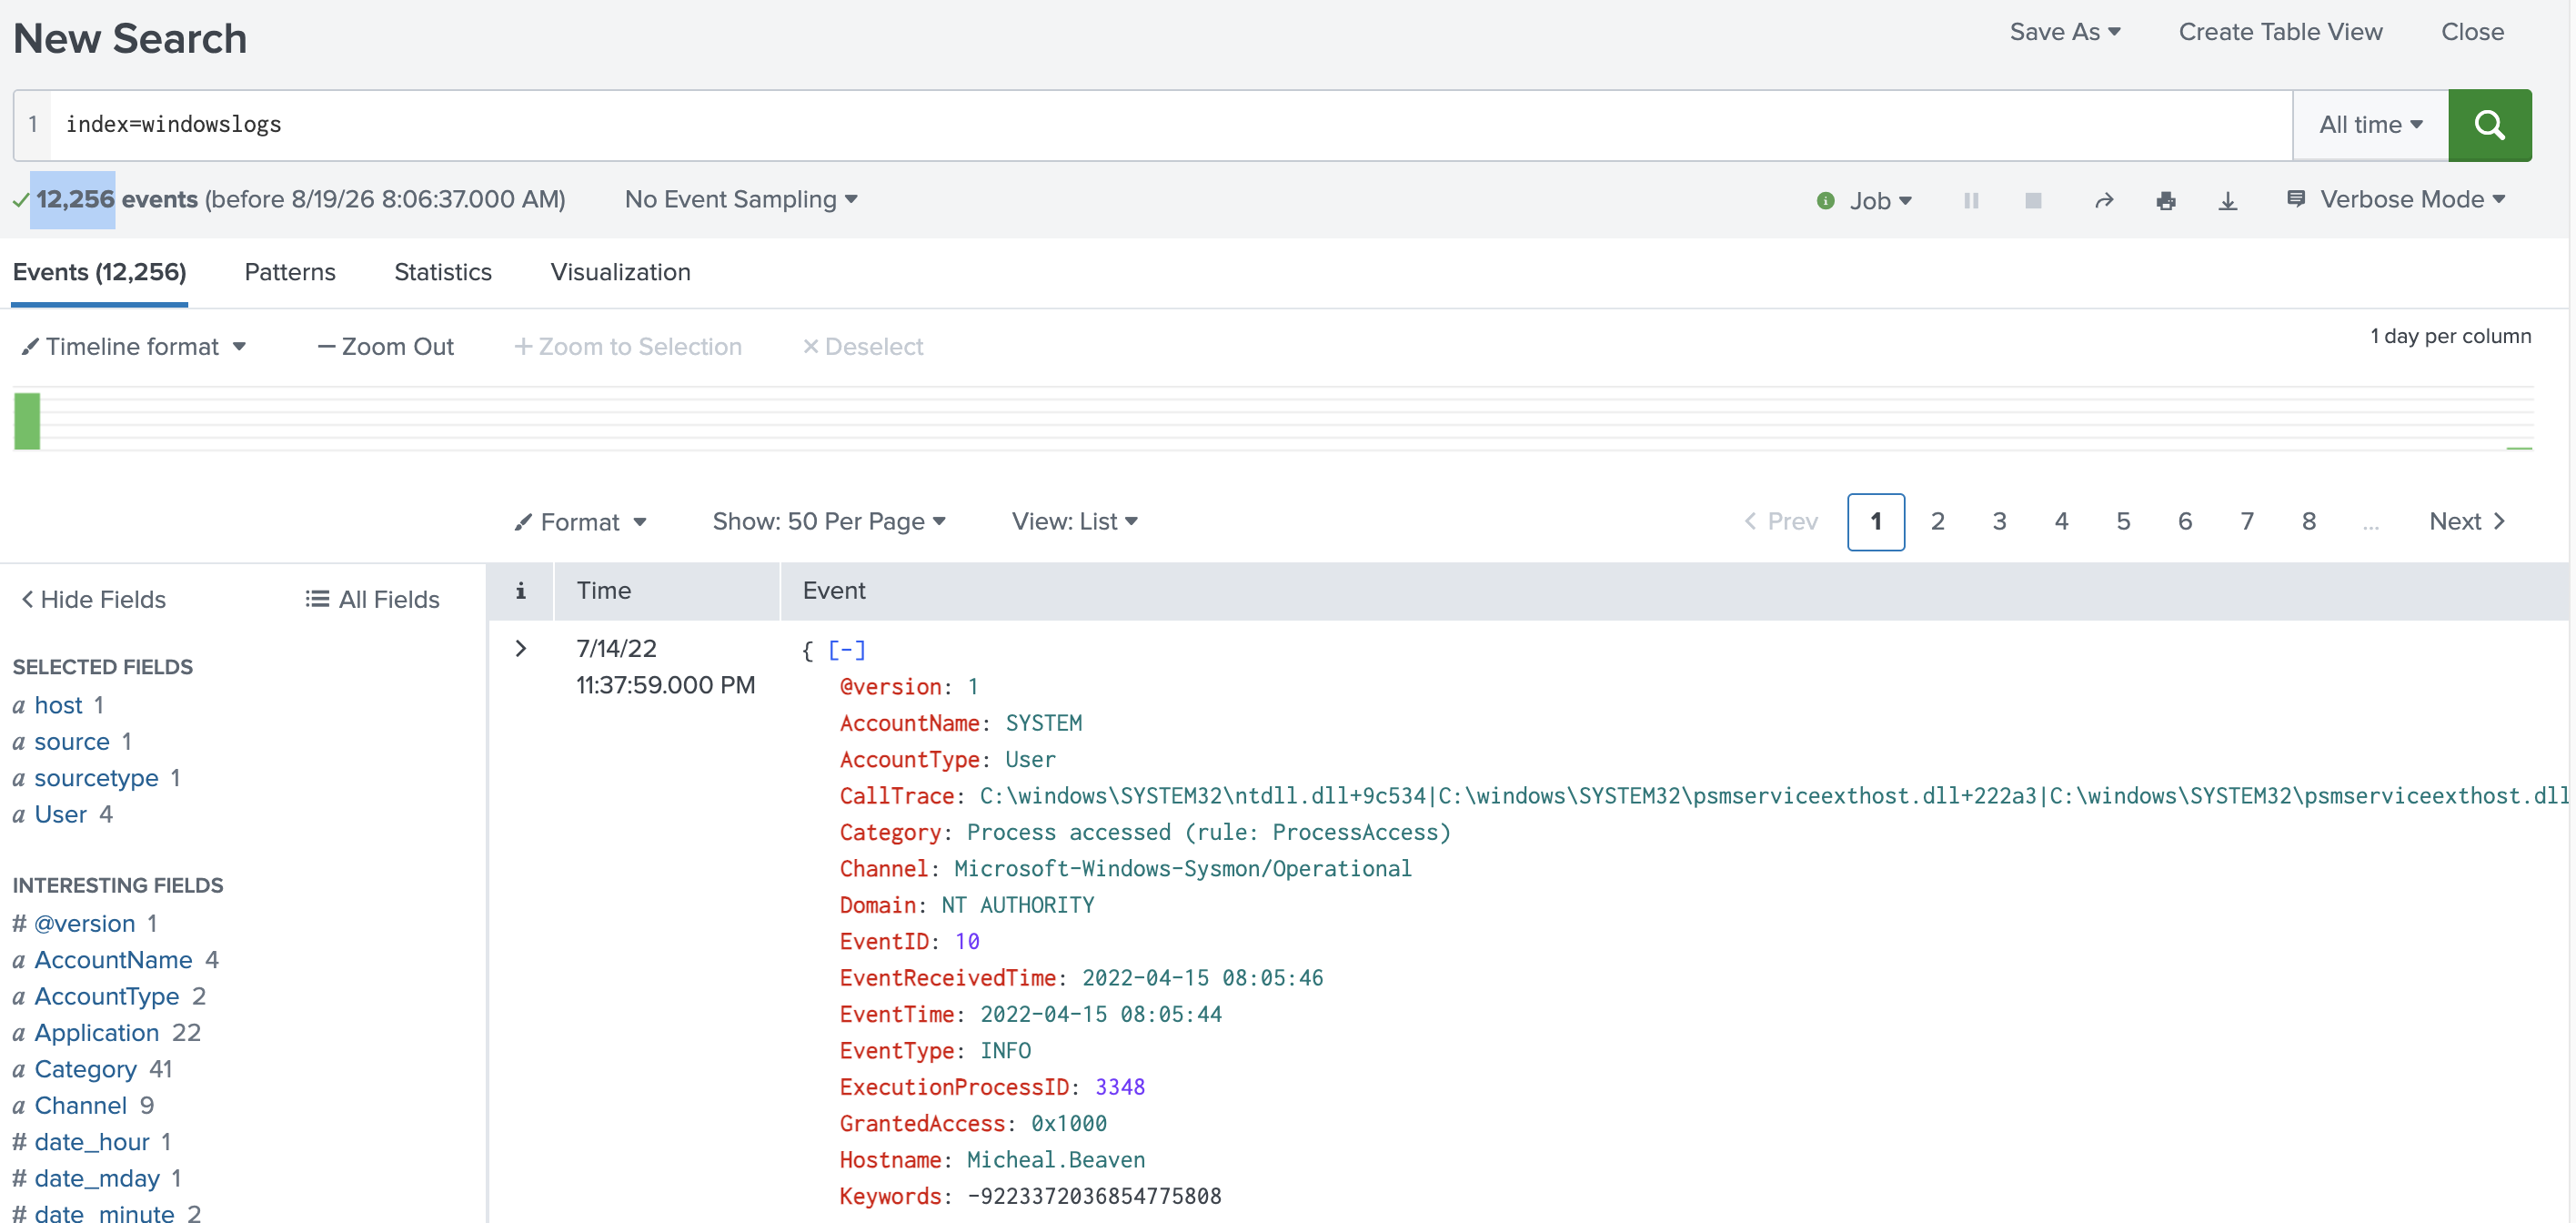
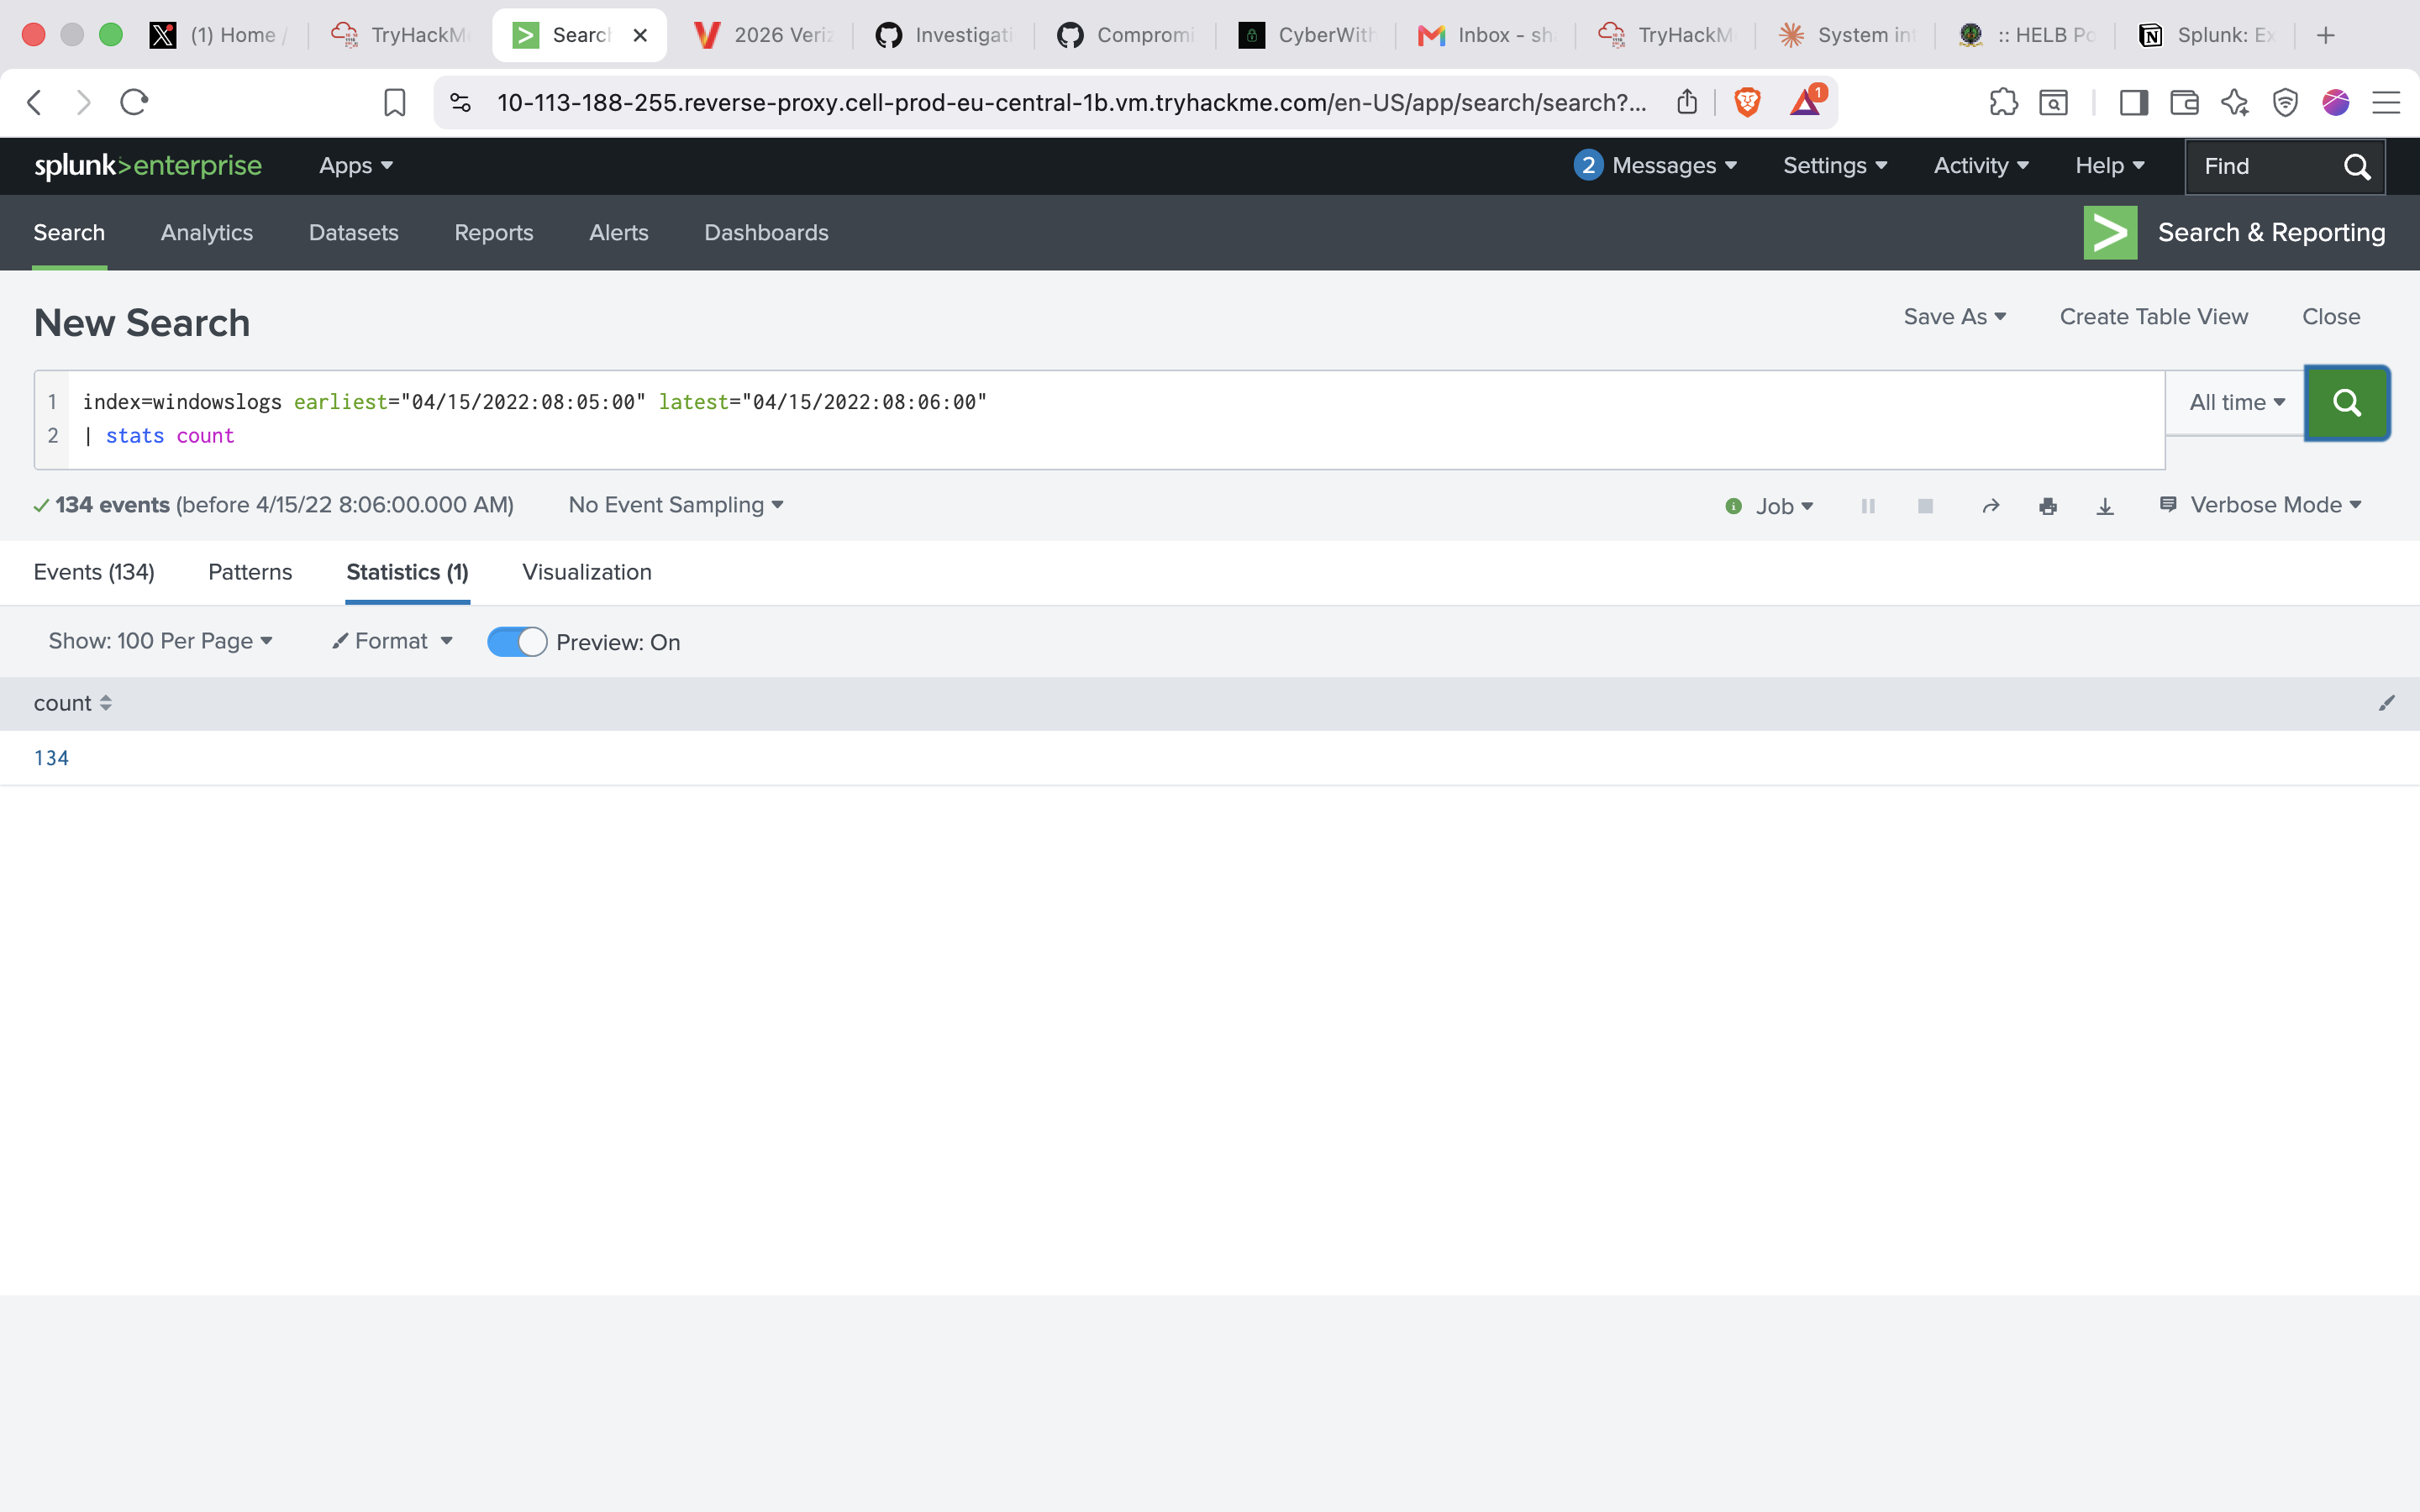
index=windowslogs earliest="04/15/2022:08:05:00" latest="04/15/2022:08:06:00"
| stats count
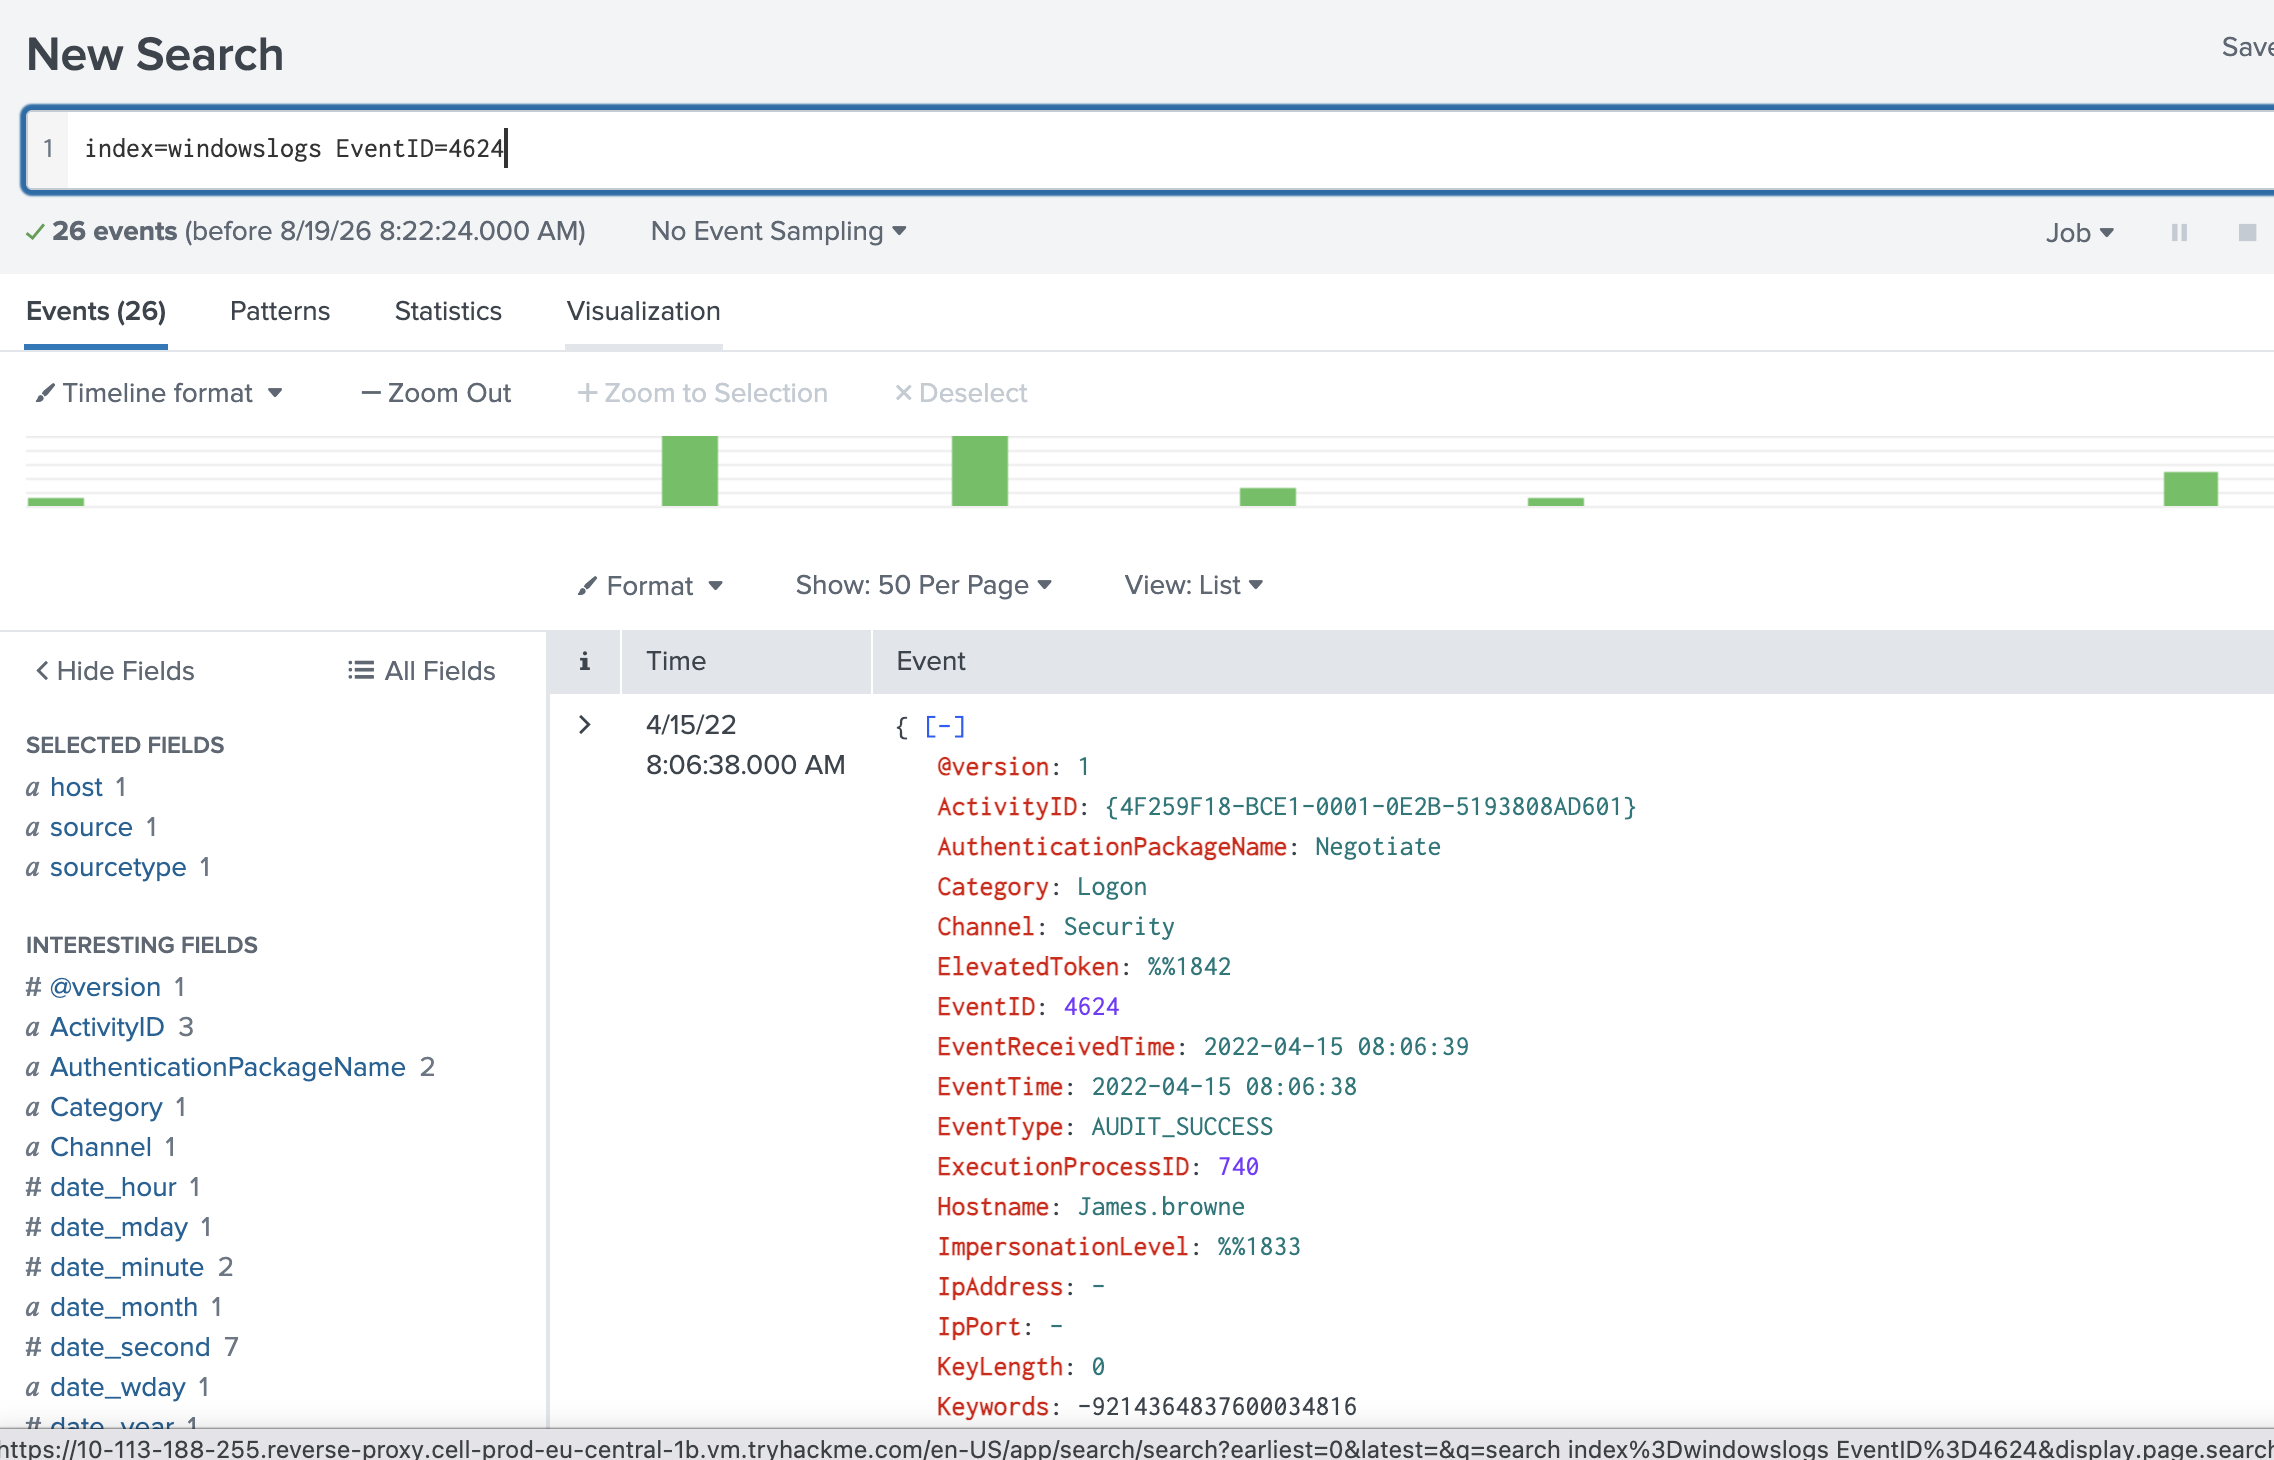
index=windowslogs EventID=4624
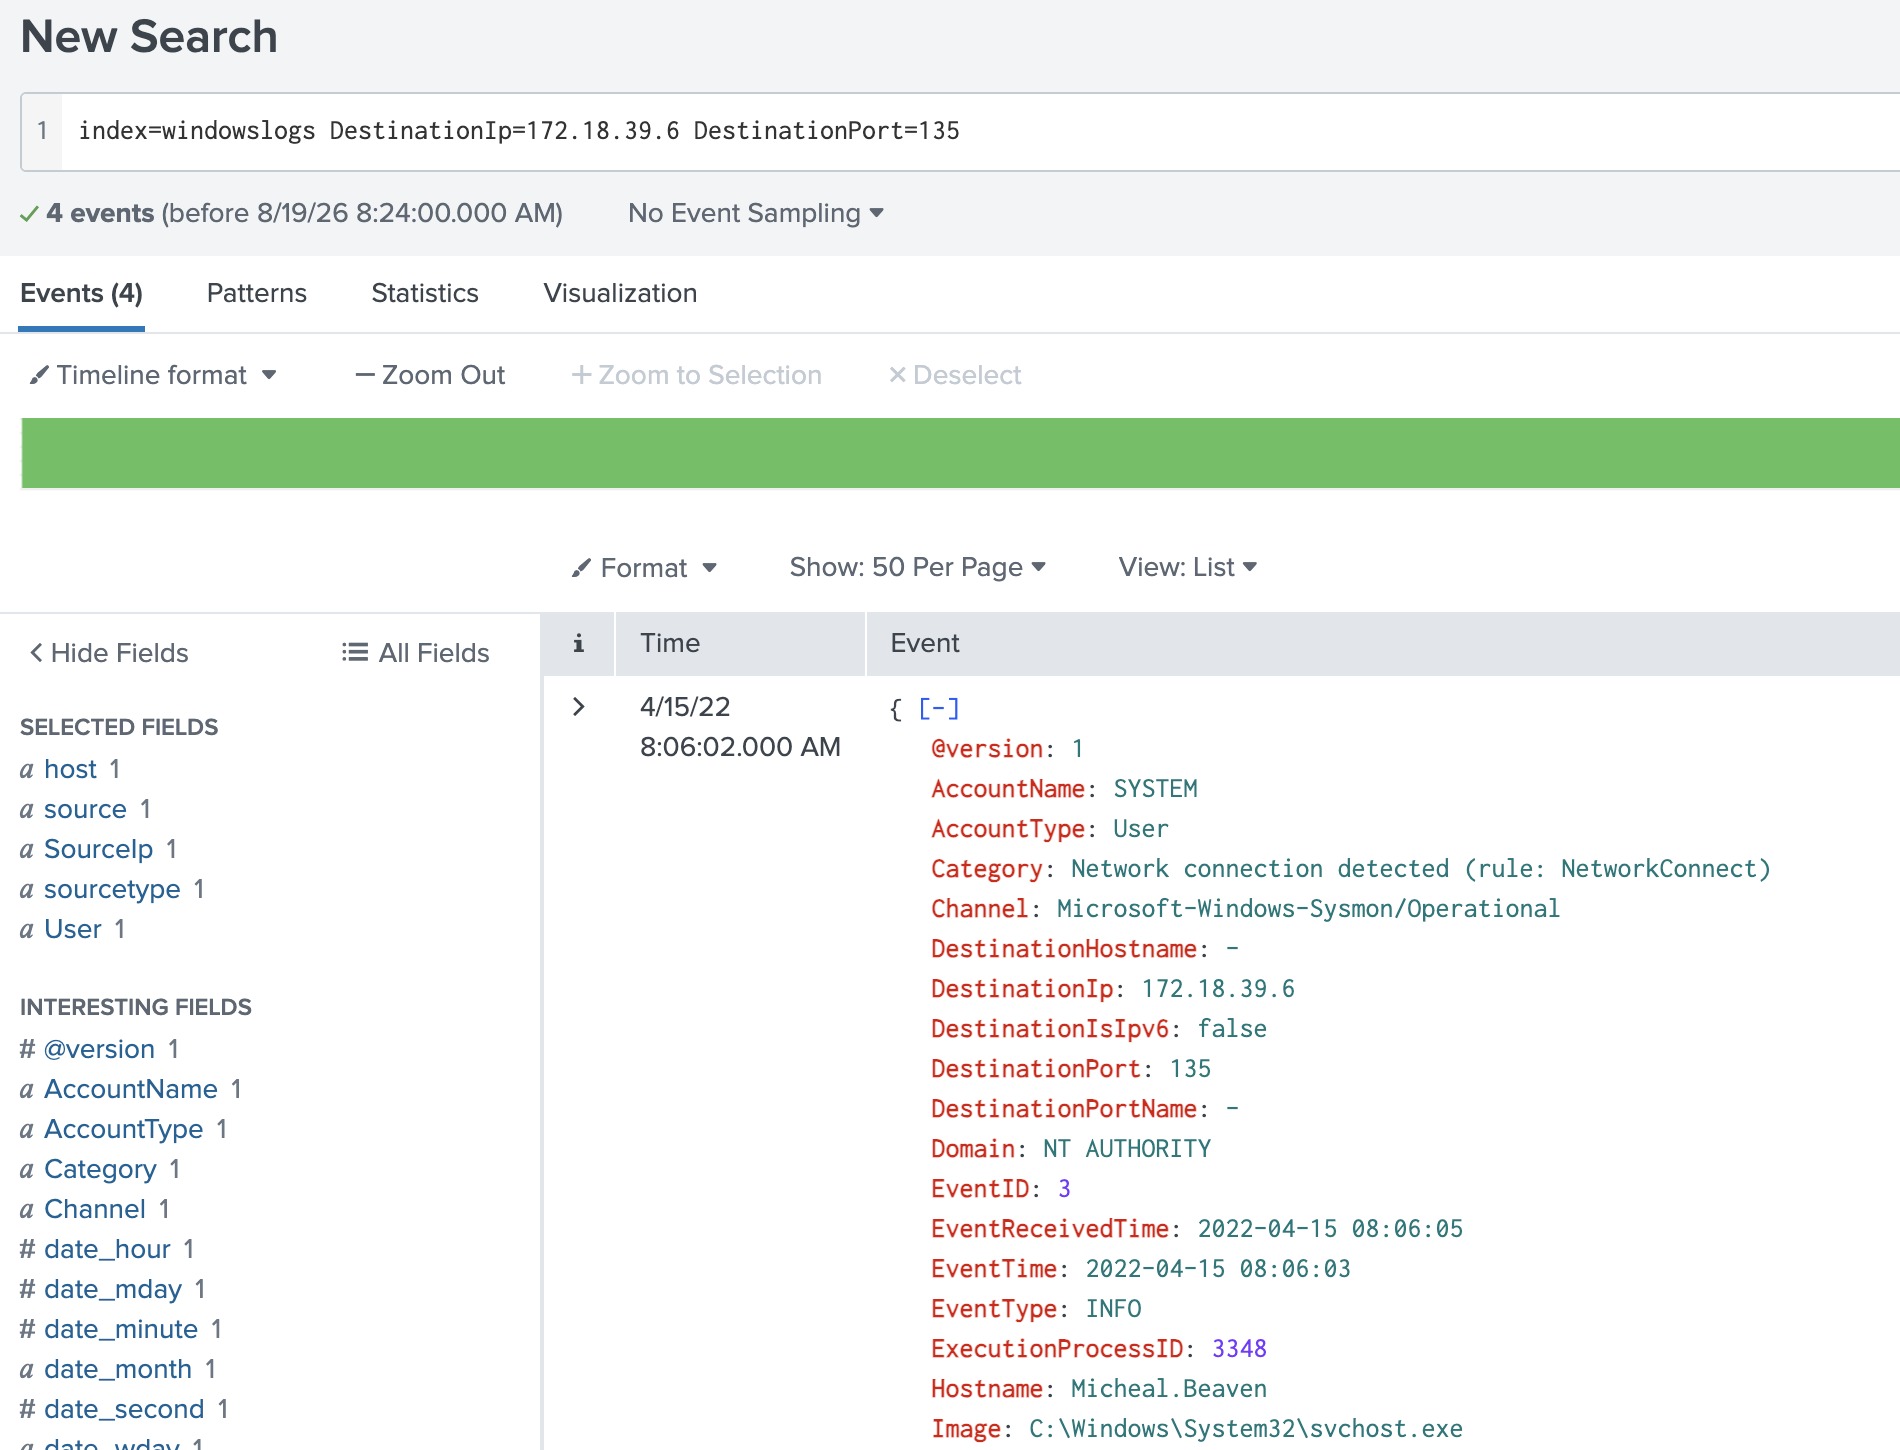
index=windowslogs DestinationIp=172.18.39.6 DestinationPort=135
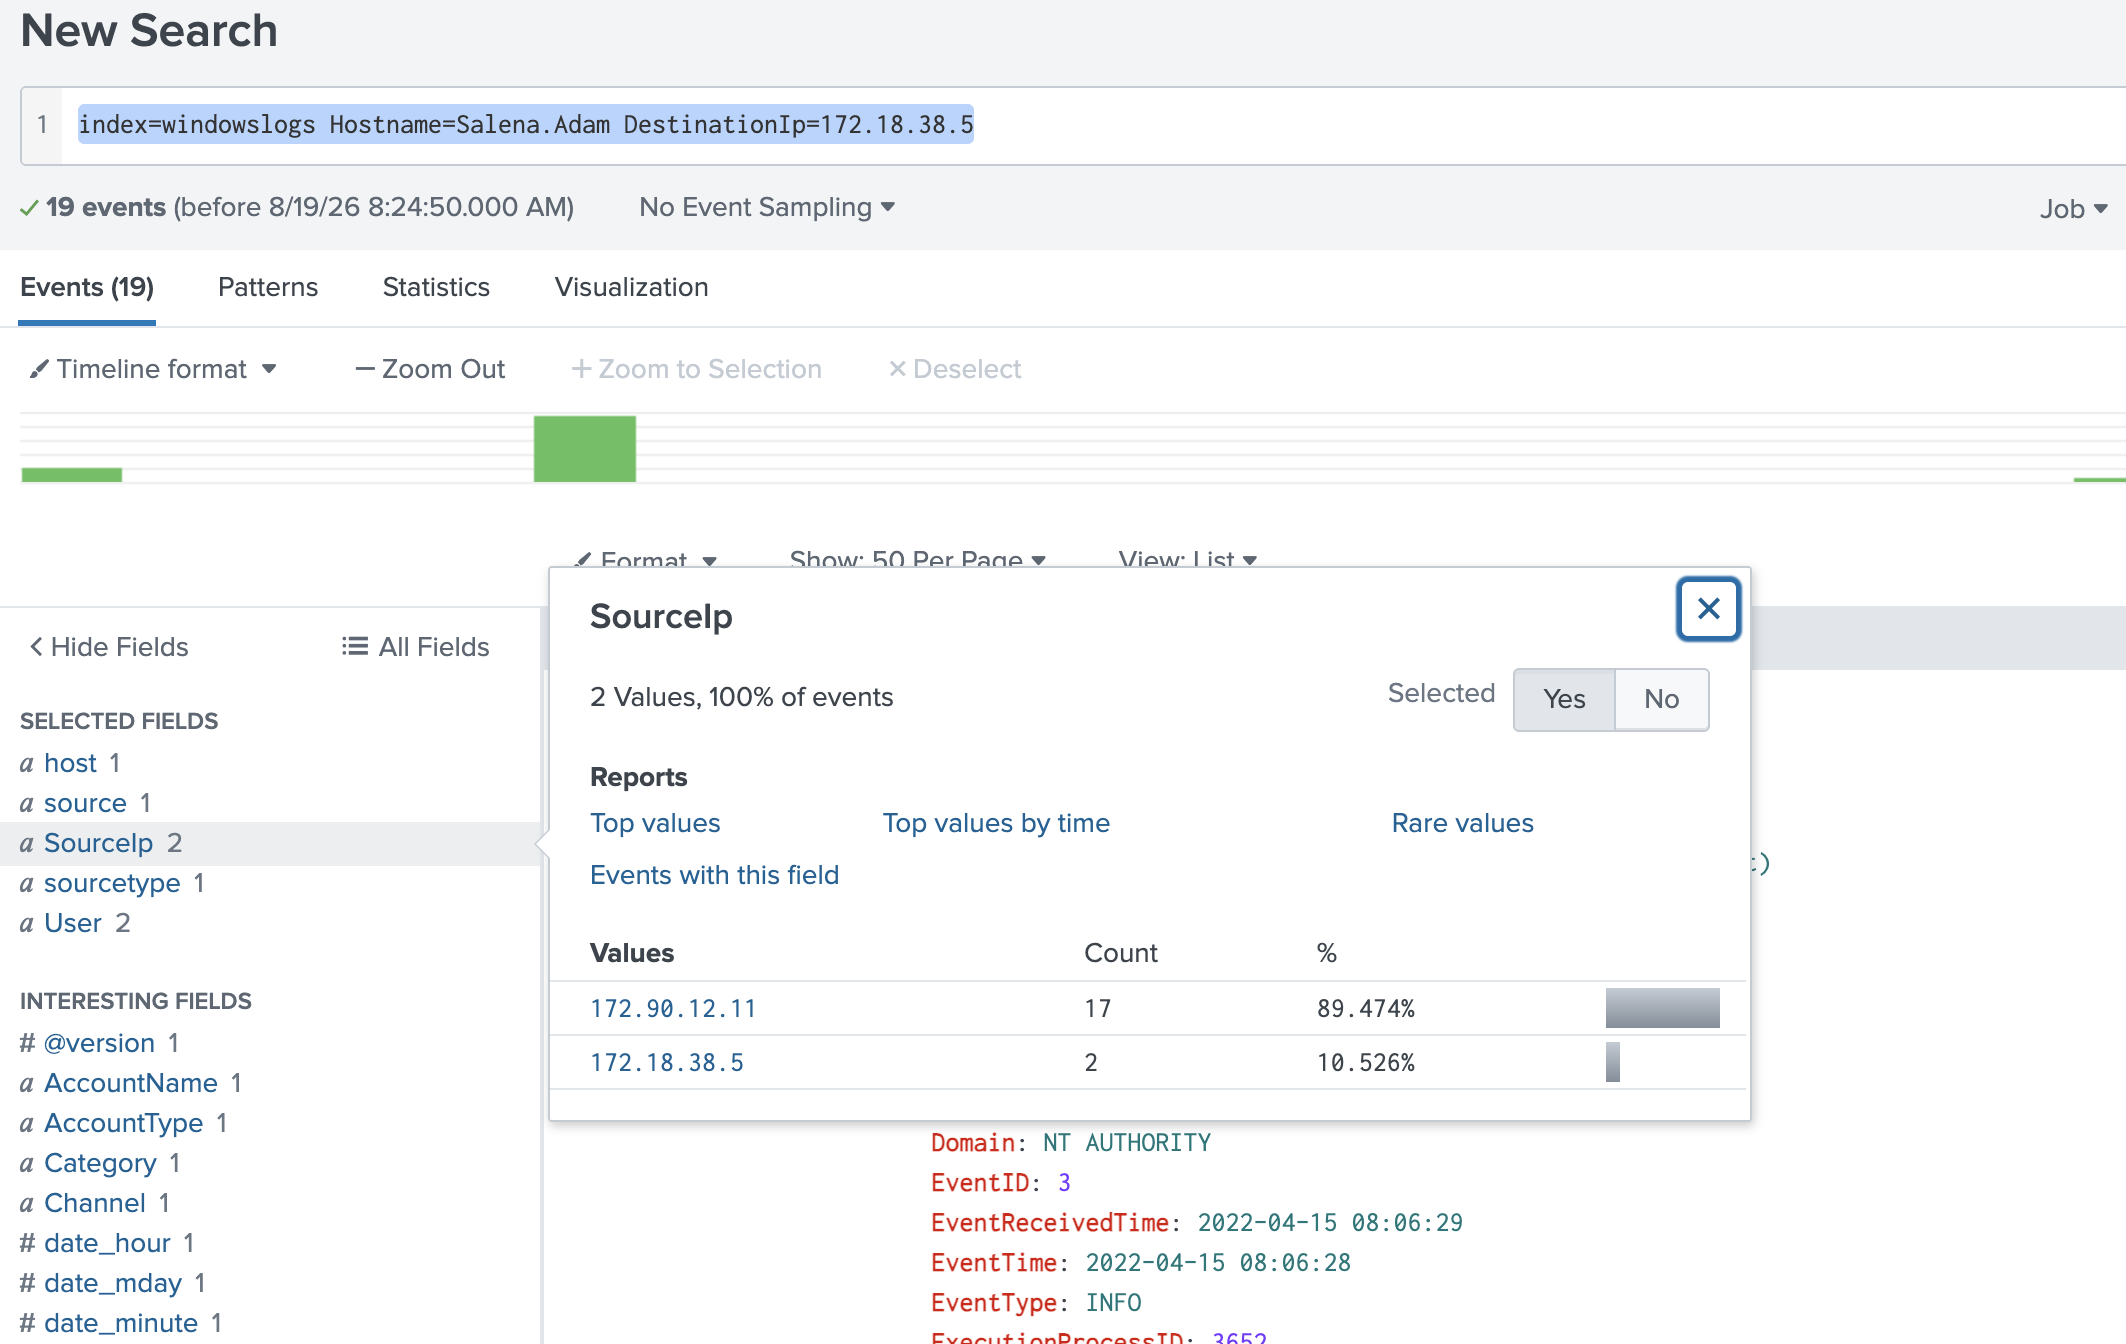
index=windowslogs Hostname=Salena.Adam DestinationIp=172.18.38.5
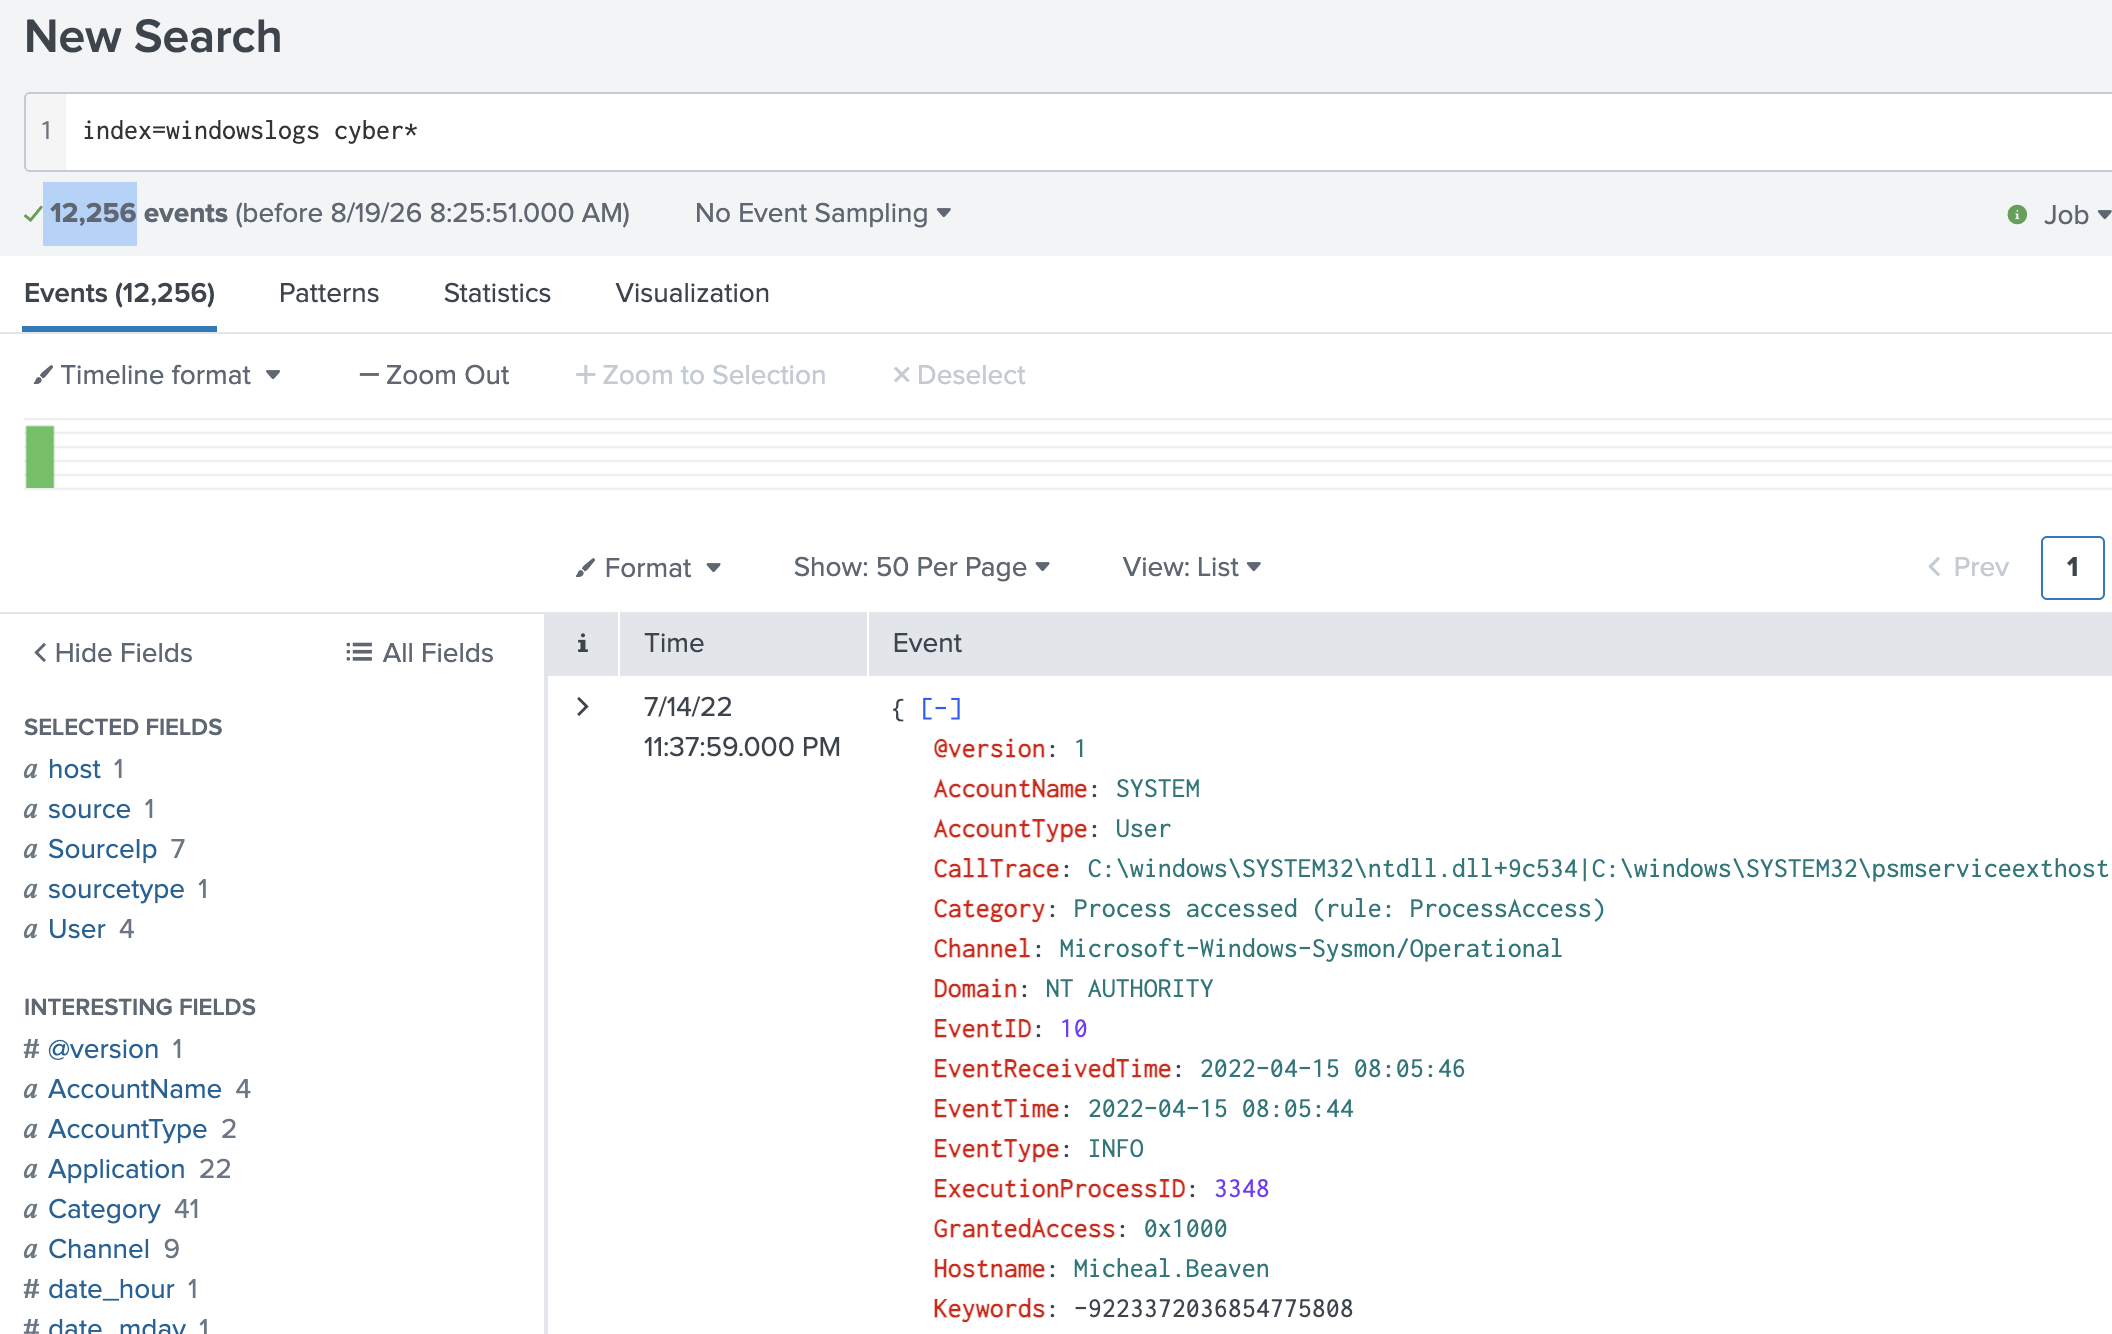
index=windowslogs cyber*
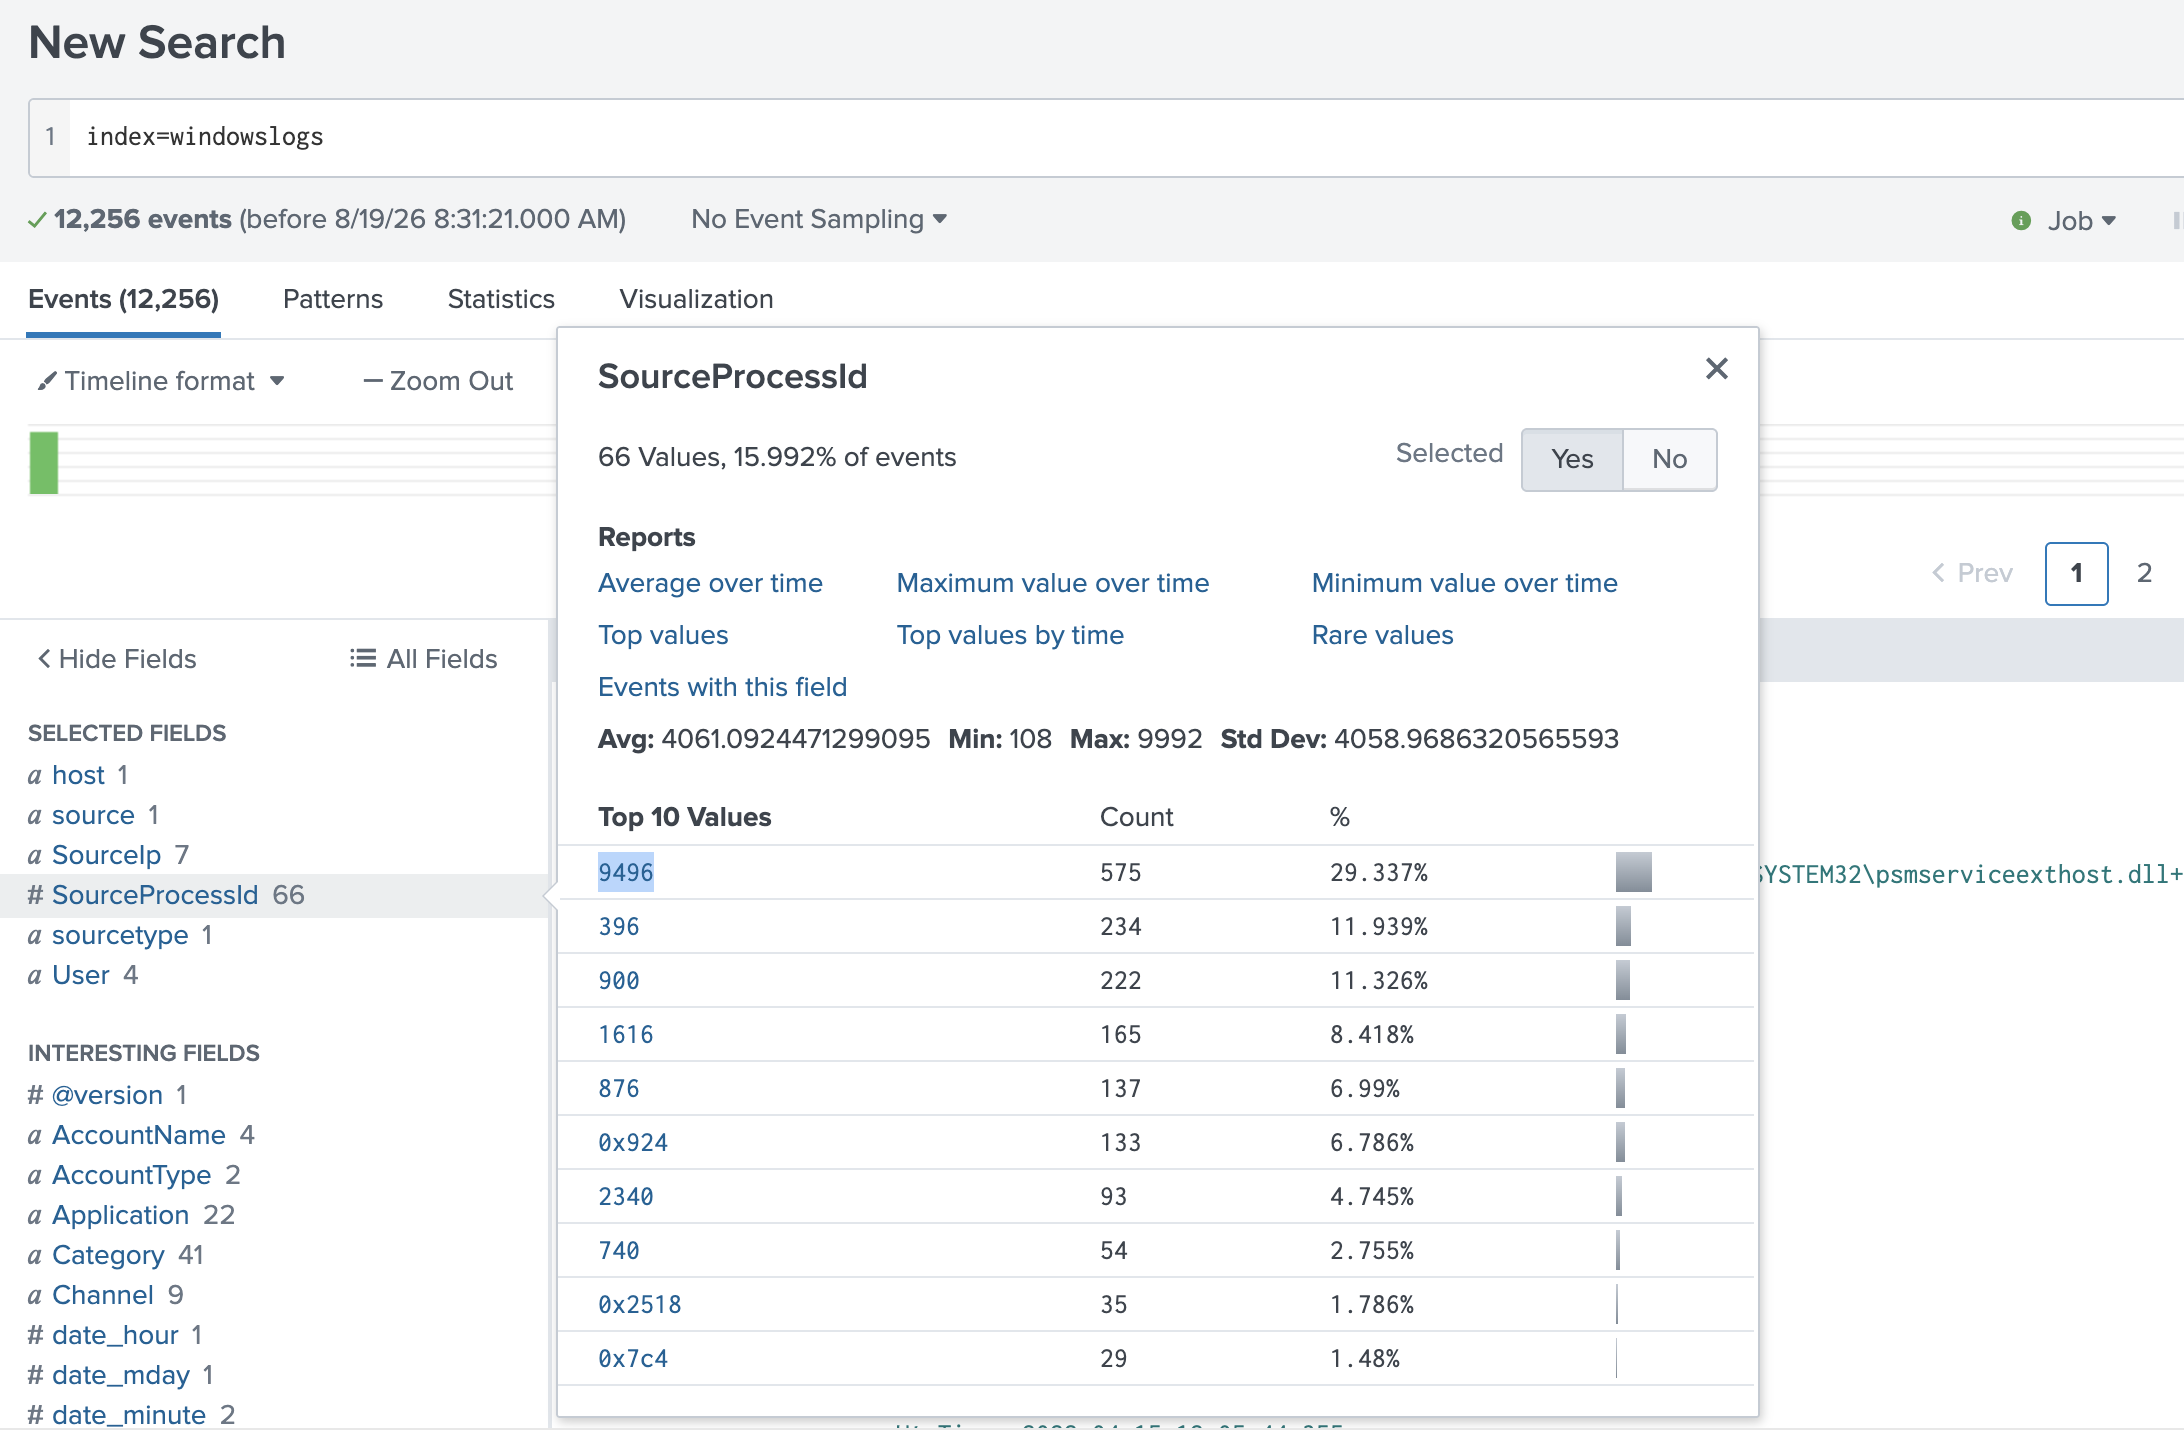
index=windowslogs
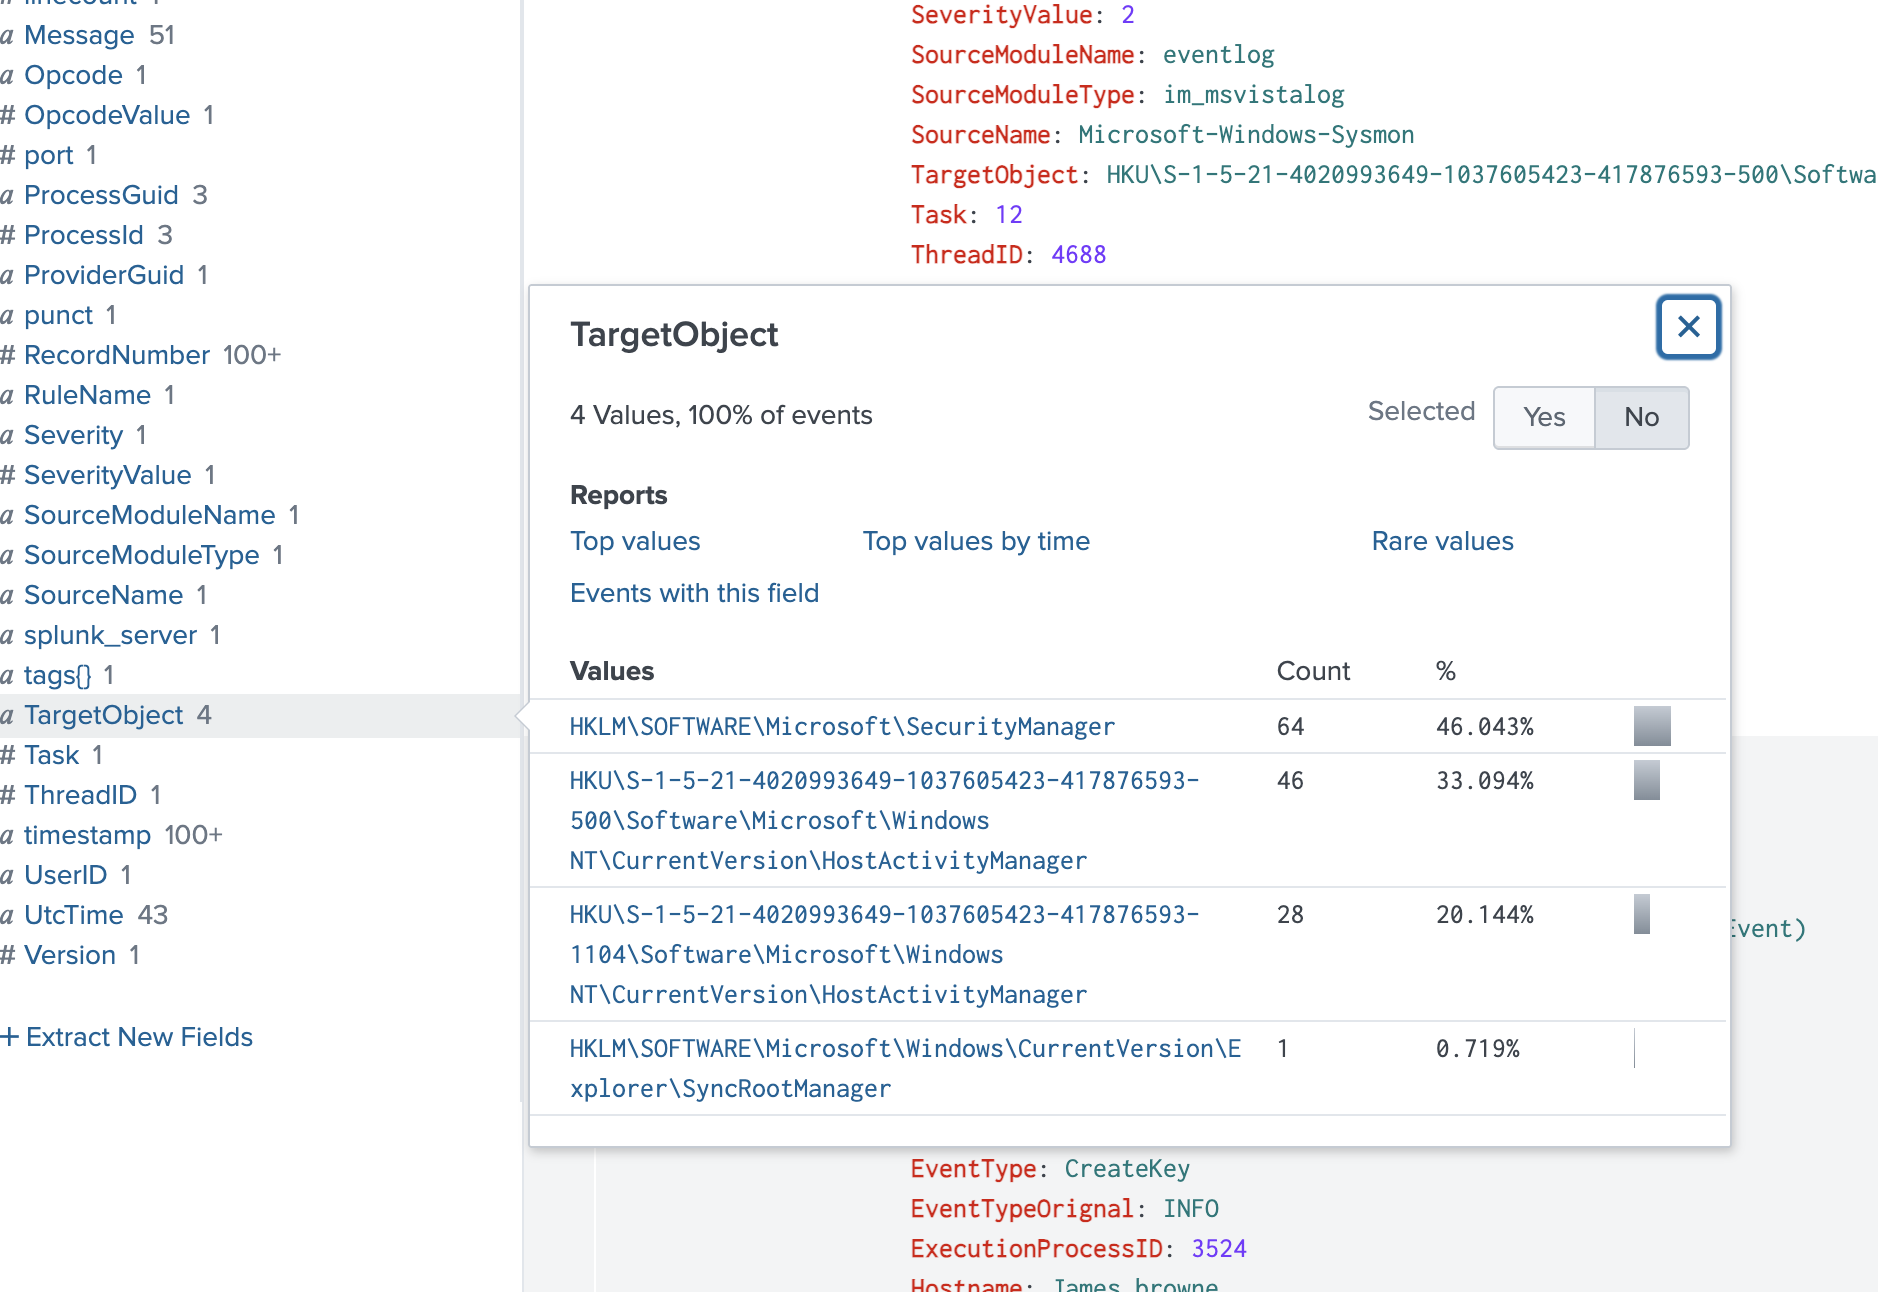
index=windowslogs | regex TargetObject="Manager$"
index=windowslogs
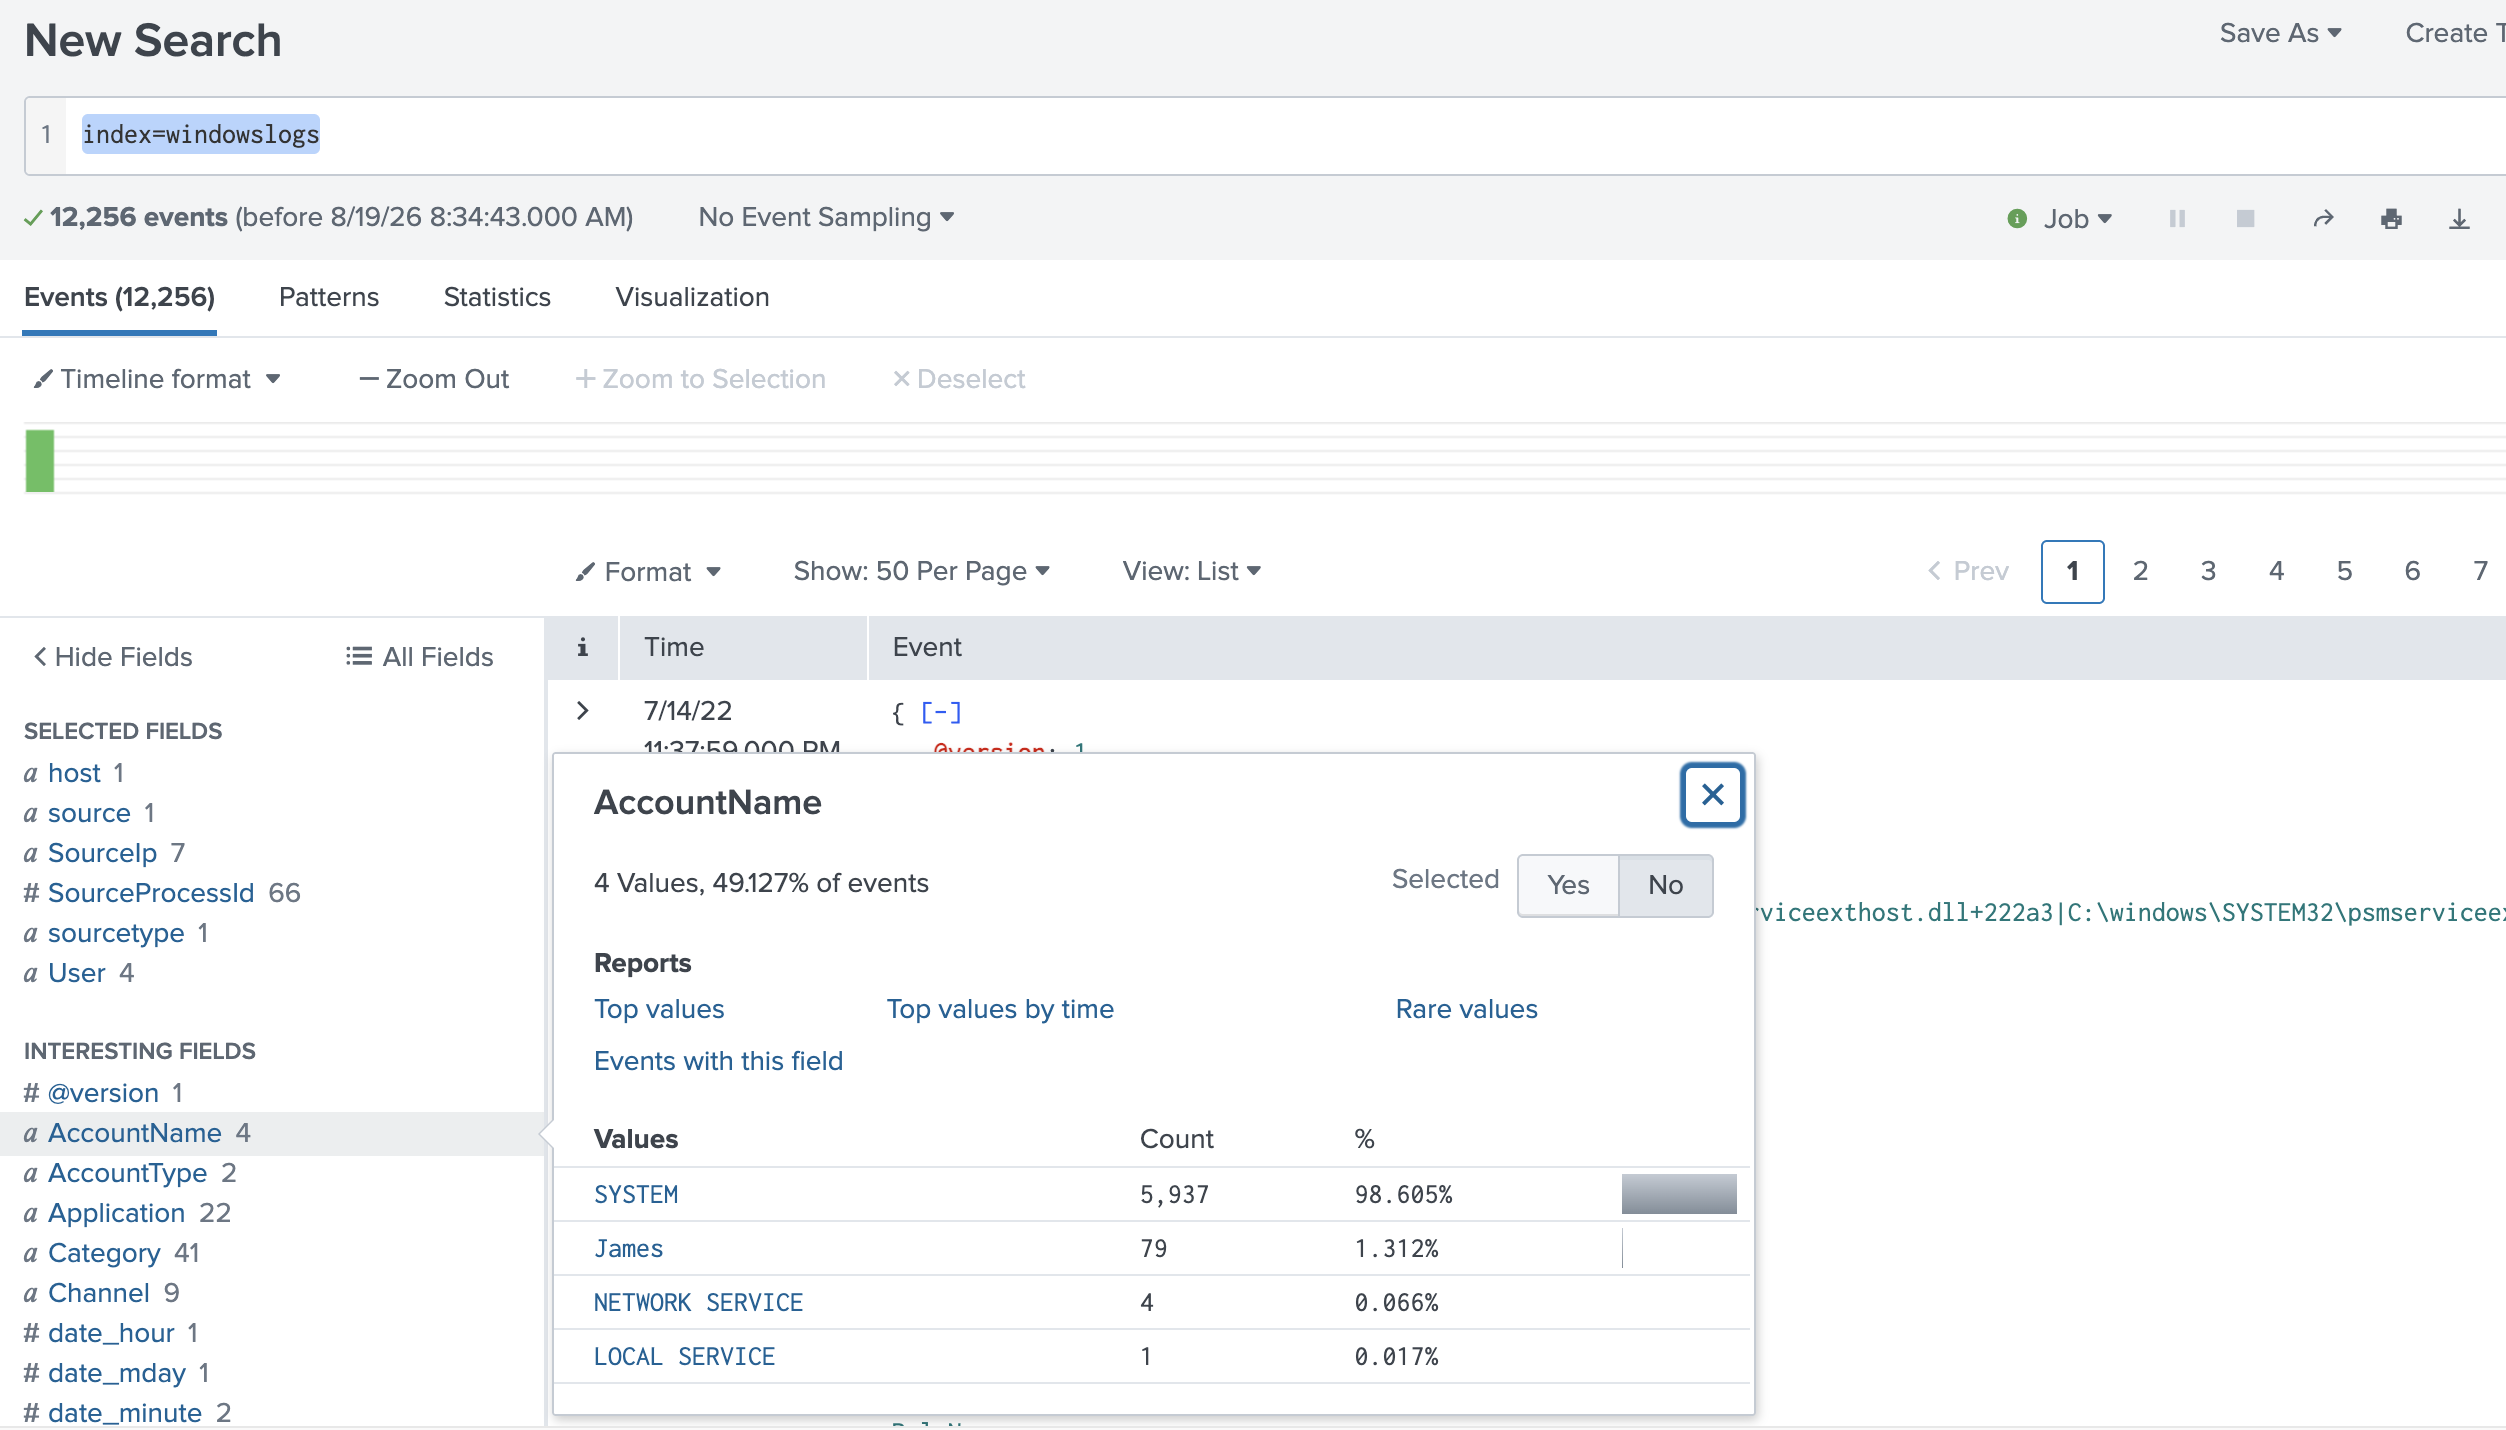
index=windowslogs | table EventID AccountName AccountType | reverse
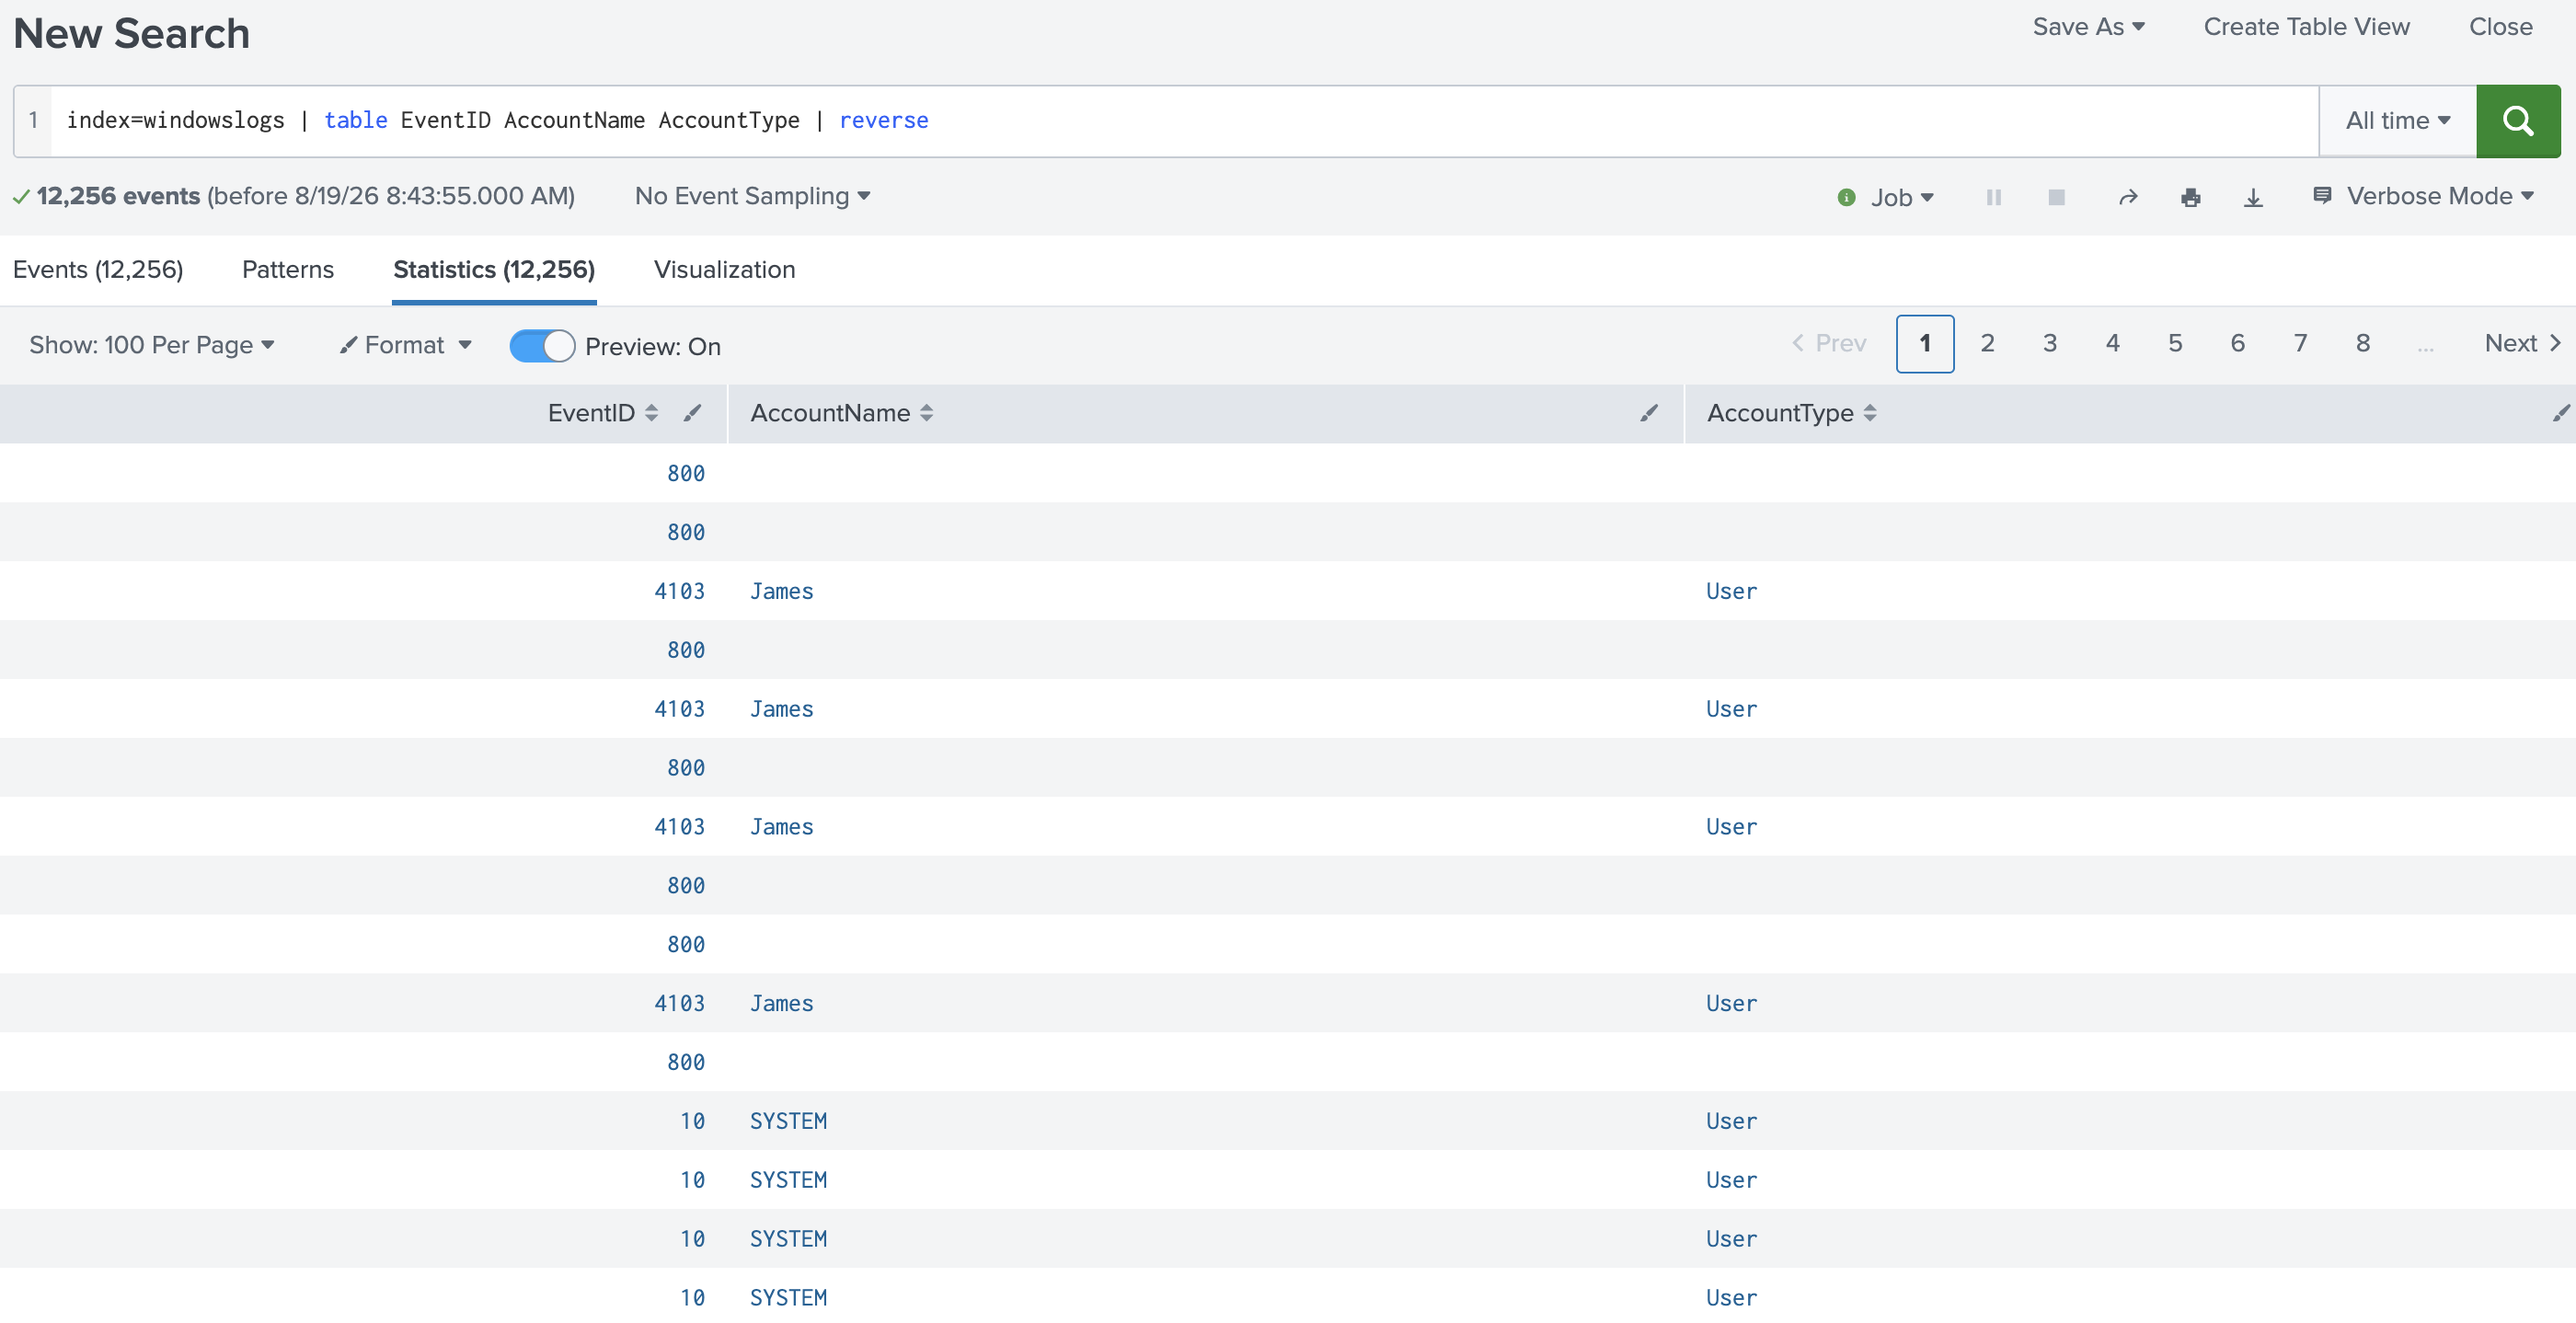
index=windowslogs EventID=1
| table _time ParentProcessId ProcessId ParentCommandLine CommandLine
| reverse
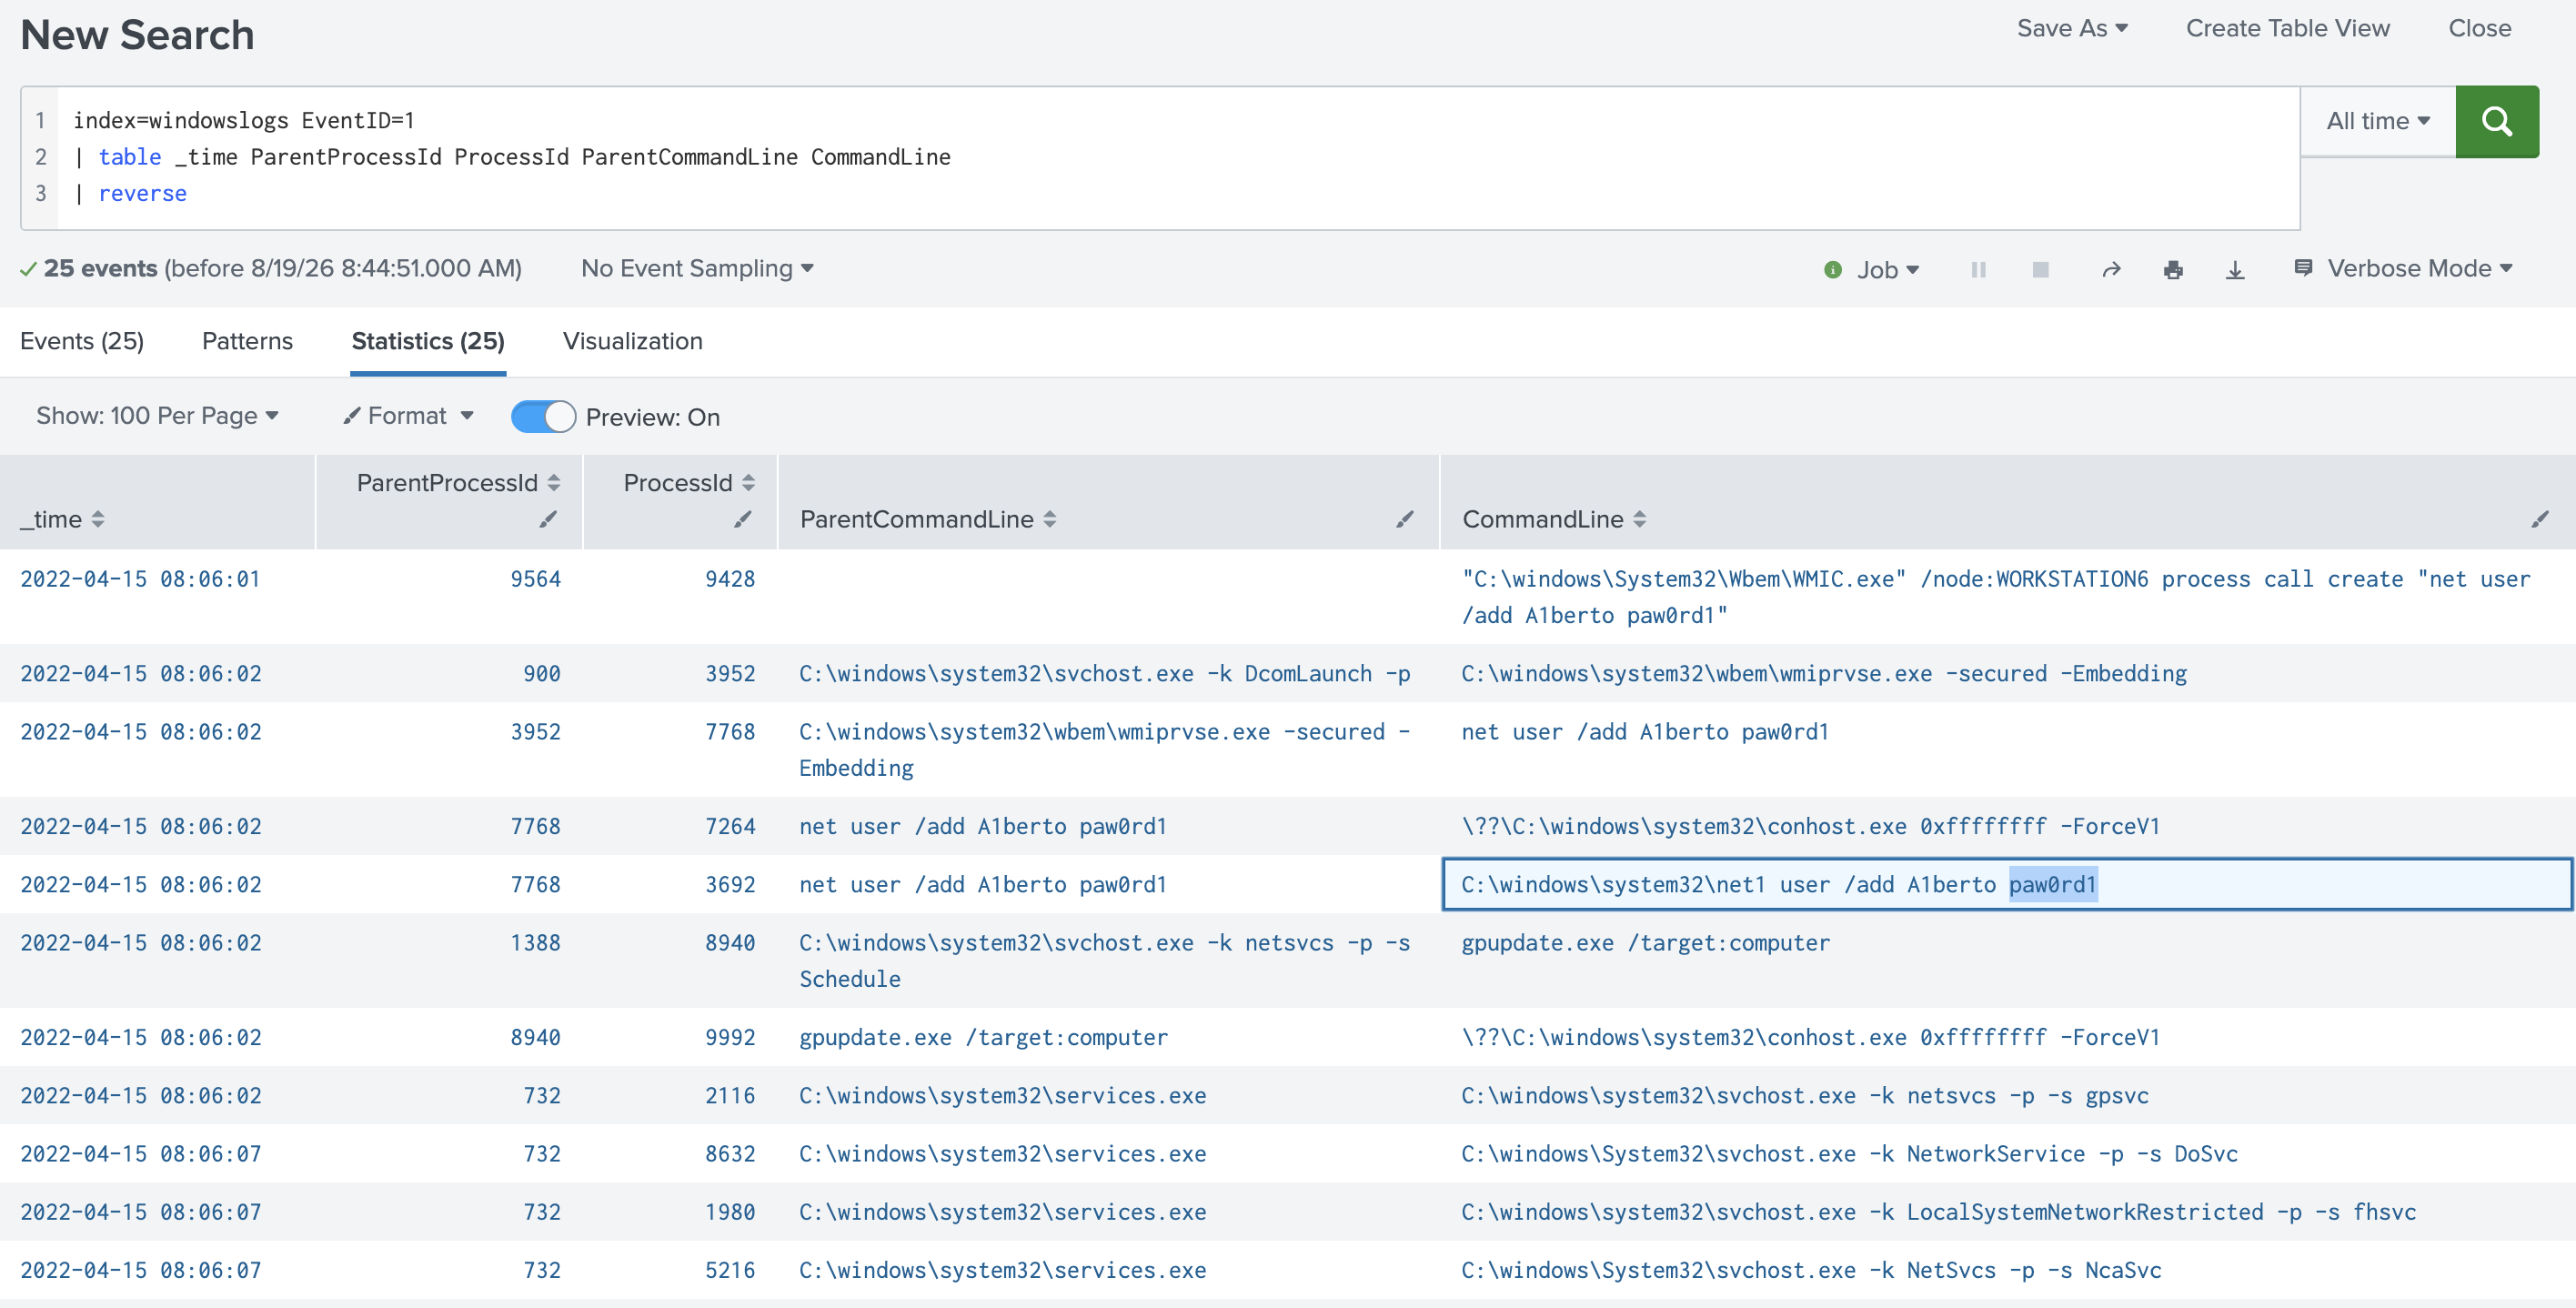
index=windowslogs
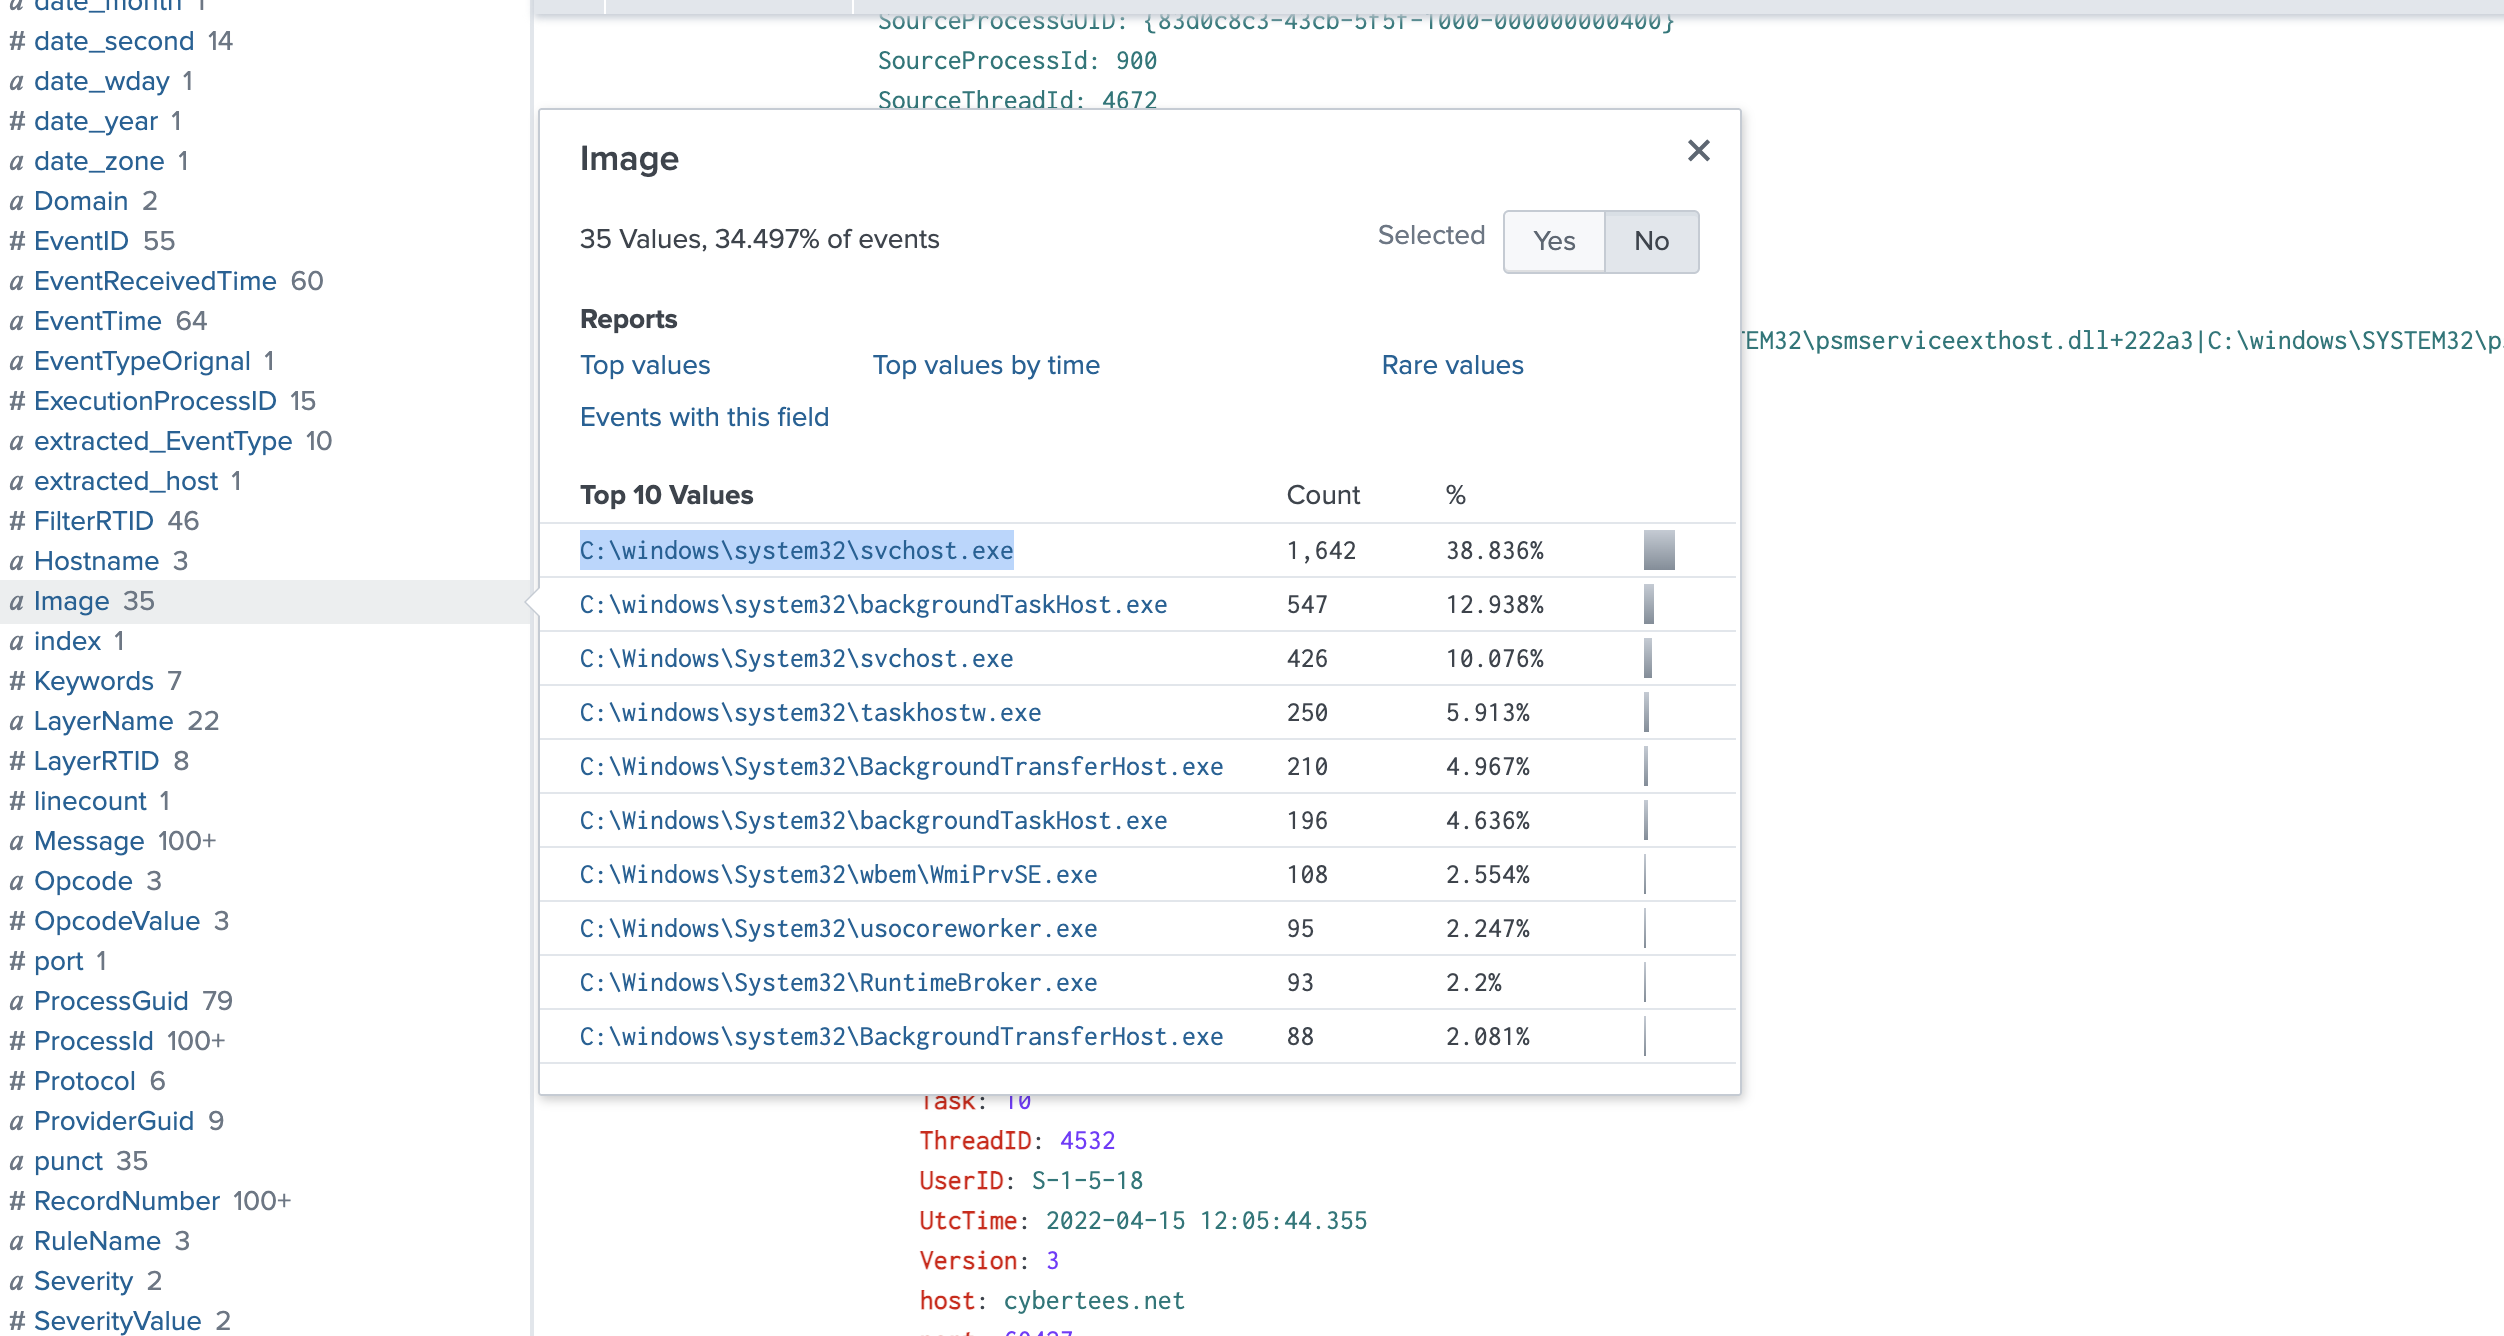
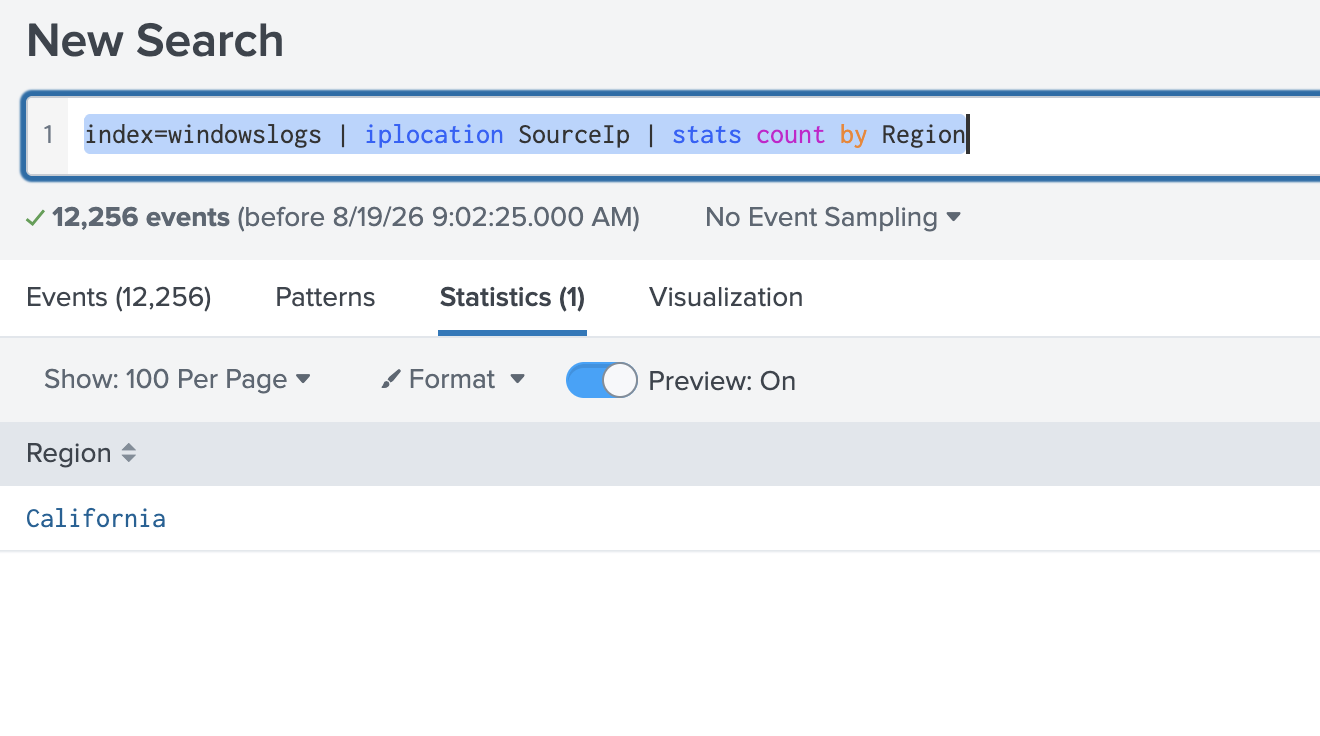
index=windowslogs | iplocation SourceIp | stats count by Region
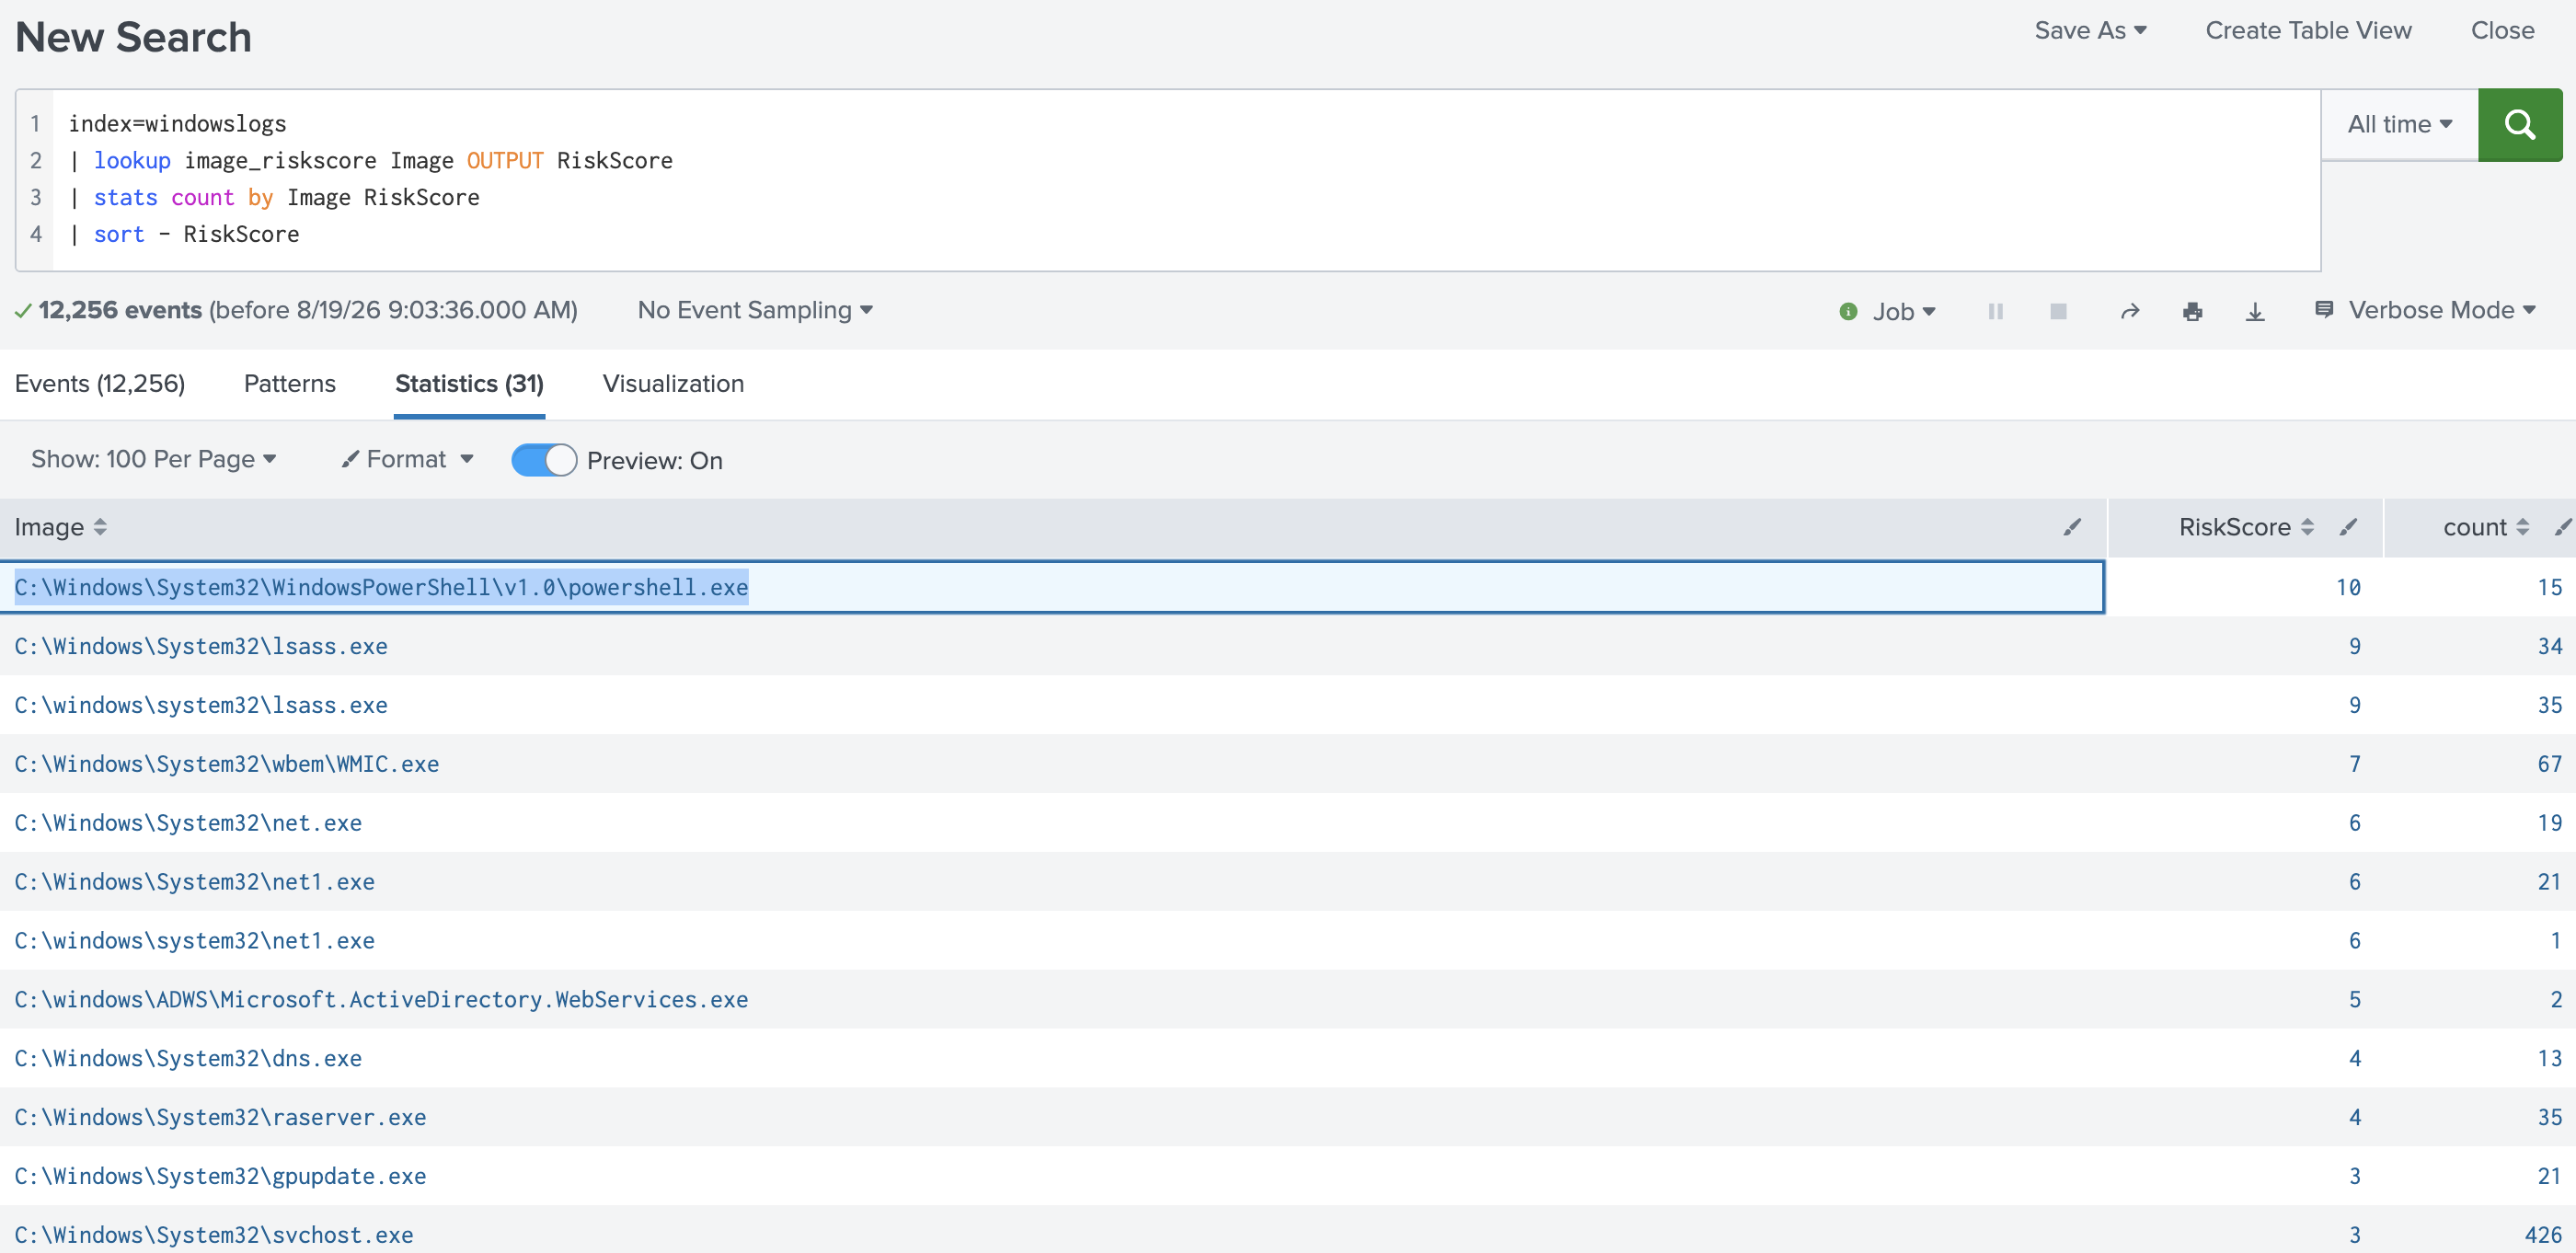
index=windowslogs
| lookup image_riskscore Image OUTPUT RiskScore
| stats count by Image RiskScore
| sort - RiskScore
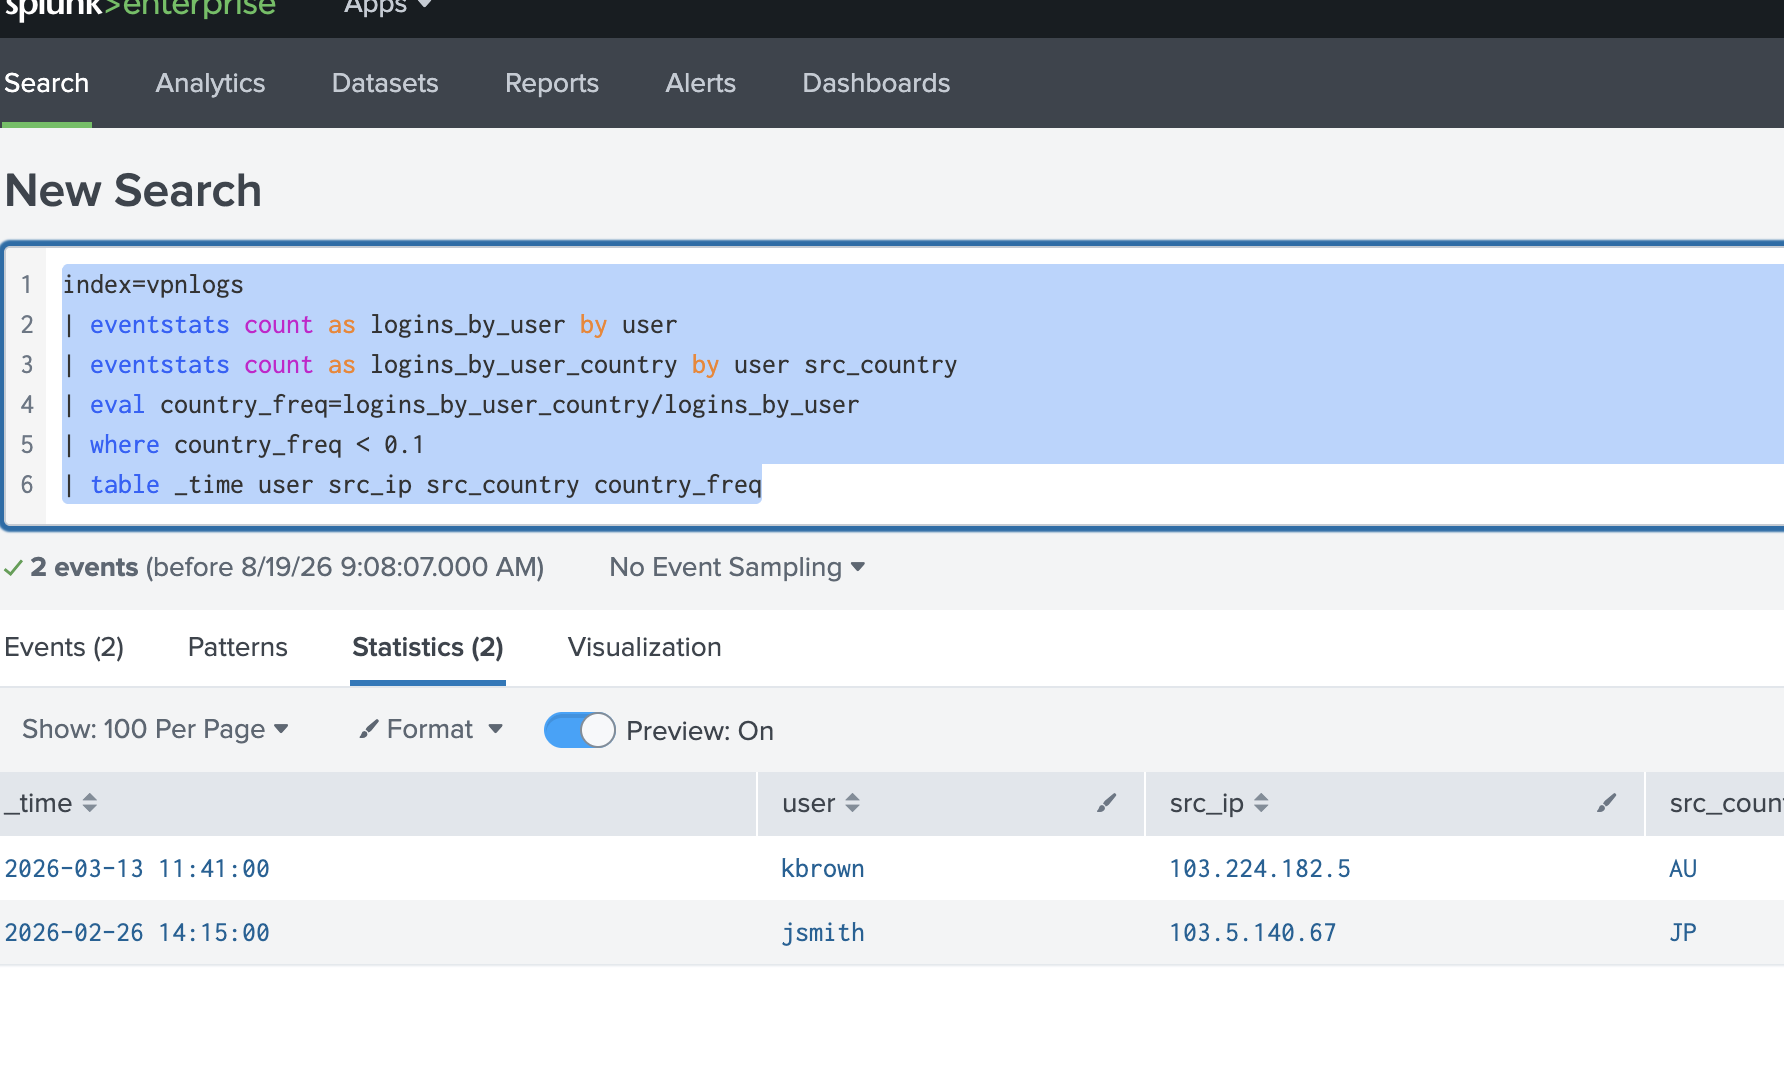
index=vpnlogs
| eventstats count as logins_by_user by user
| eventstats count as logins_by_user_country by user src_country
| eval country_freq=logins_by_user_country/logins_by_user
| where country_freq < 0.1
| table _time user src_ip src_country country_freq
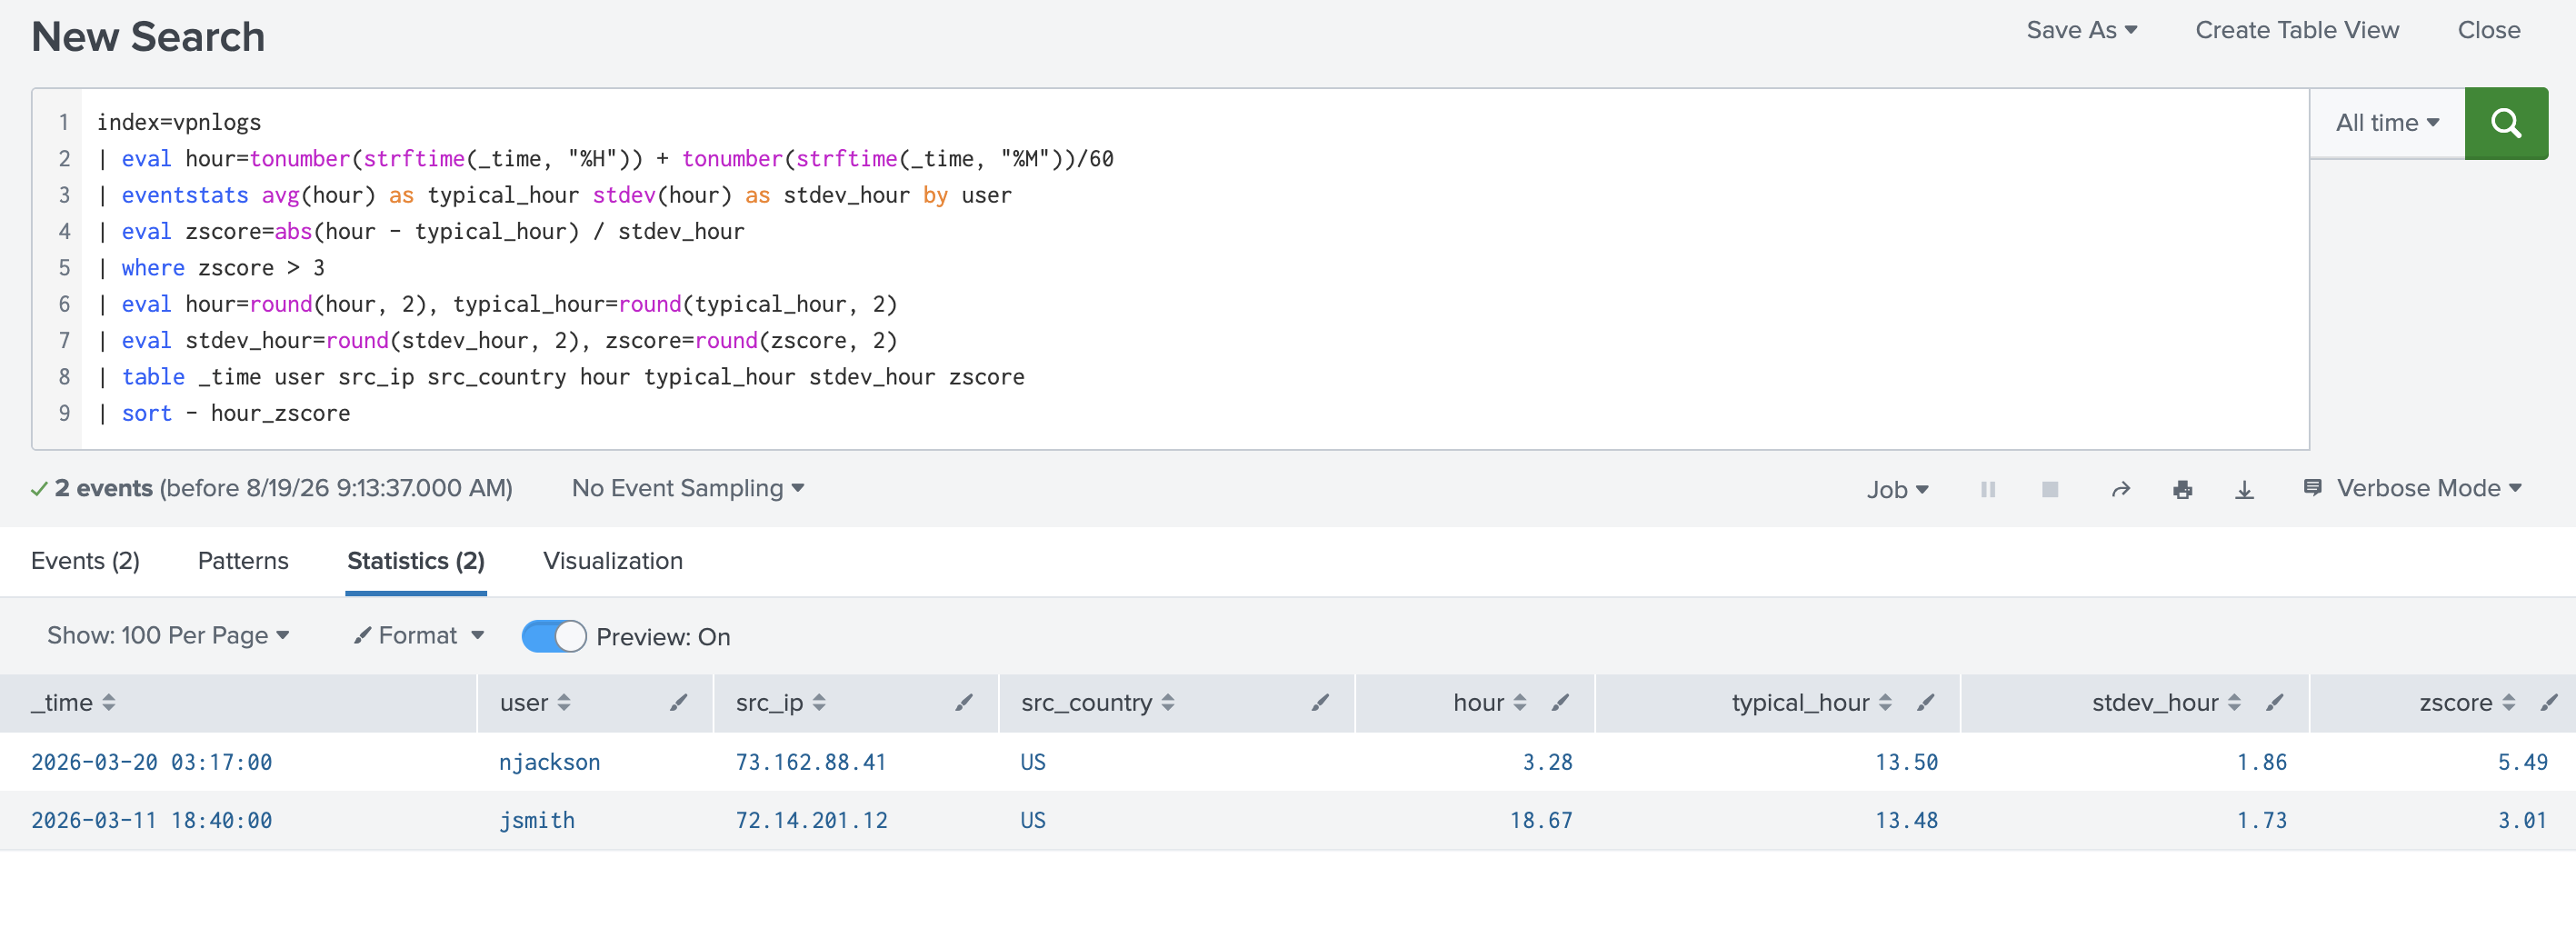
index=vpnlogs
| eval hour=tonumber(strftime(_time, "%H")) + tonumber(strftime(_time, "%M"))/60
| eventstats avg(hour) as typical_hour stdev(hour) as stdev_hour by user
| eval zscore=abs(hour - typical_hour) / stdev_hour
| where zscore > 3
| eval hour=round(hour, 2), typical_hour=round(typical_hour, 2)
| eval stdev_hour=round(stdev_hour, 2), zscore=round(zscore, 2)
| table _time user src_ip src_country hour typical_hour stdev_hour zscore
| sort - hour_zscore