Just a VPN Login: VirusTotal - IP & Hash Logs (TryHackMe)
Link to the challenge on TryHackMe: Just a VPN Login
Unusual Login
Welcome to your first shift! You are greeted by an internal alert on the SOC dashboard titled "Unusual VPN login of susan.martin@probablyfine.thm from 37.19.201.132 (Singapore)."
The SOC handover notes did indeed mention that Susan from Marketing is in Singapore, attending a security vendor conference. It is probably just fine, but the SOC procedure tells us to verify each IP in our threat intel platform TryDetectThis. Answer the first four questions to gather more information and determine the threat level.
Security Check Tool
That login IP looks suspicious, doesn't it? Your teammates reached out to Susan, and she confirmed she did not log in to the company VPN. She also mentioned that while using a public Wi-Fi hotspot at a cafe, she was suddenly prompted to install a "security check" tool, which she did. The host telemetry reveals a suspicious binary with the hash b8e02f2bc0ffb42e8cf28e37a26d8d825f639079bf6d948f8debab6440ee5630. Can you help us figure out what this binary exactly does and answer the remaining questions?
TryDetectThis
TryDetectThis is a threat intelligence database to check the reputation and other details of IP addresses, domains, and file hashes. To access this platform, please navigate to the following URL in your own browser:
Answer the questions below
What is the ASN number related to the IP?
- Open TryDetectThis and search the provided IP_Address
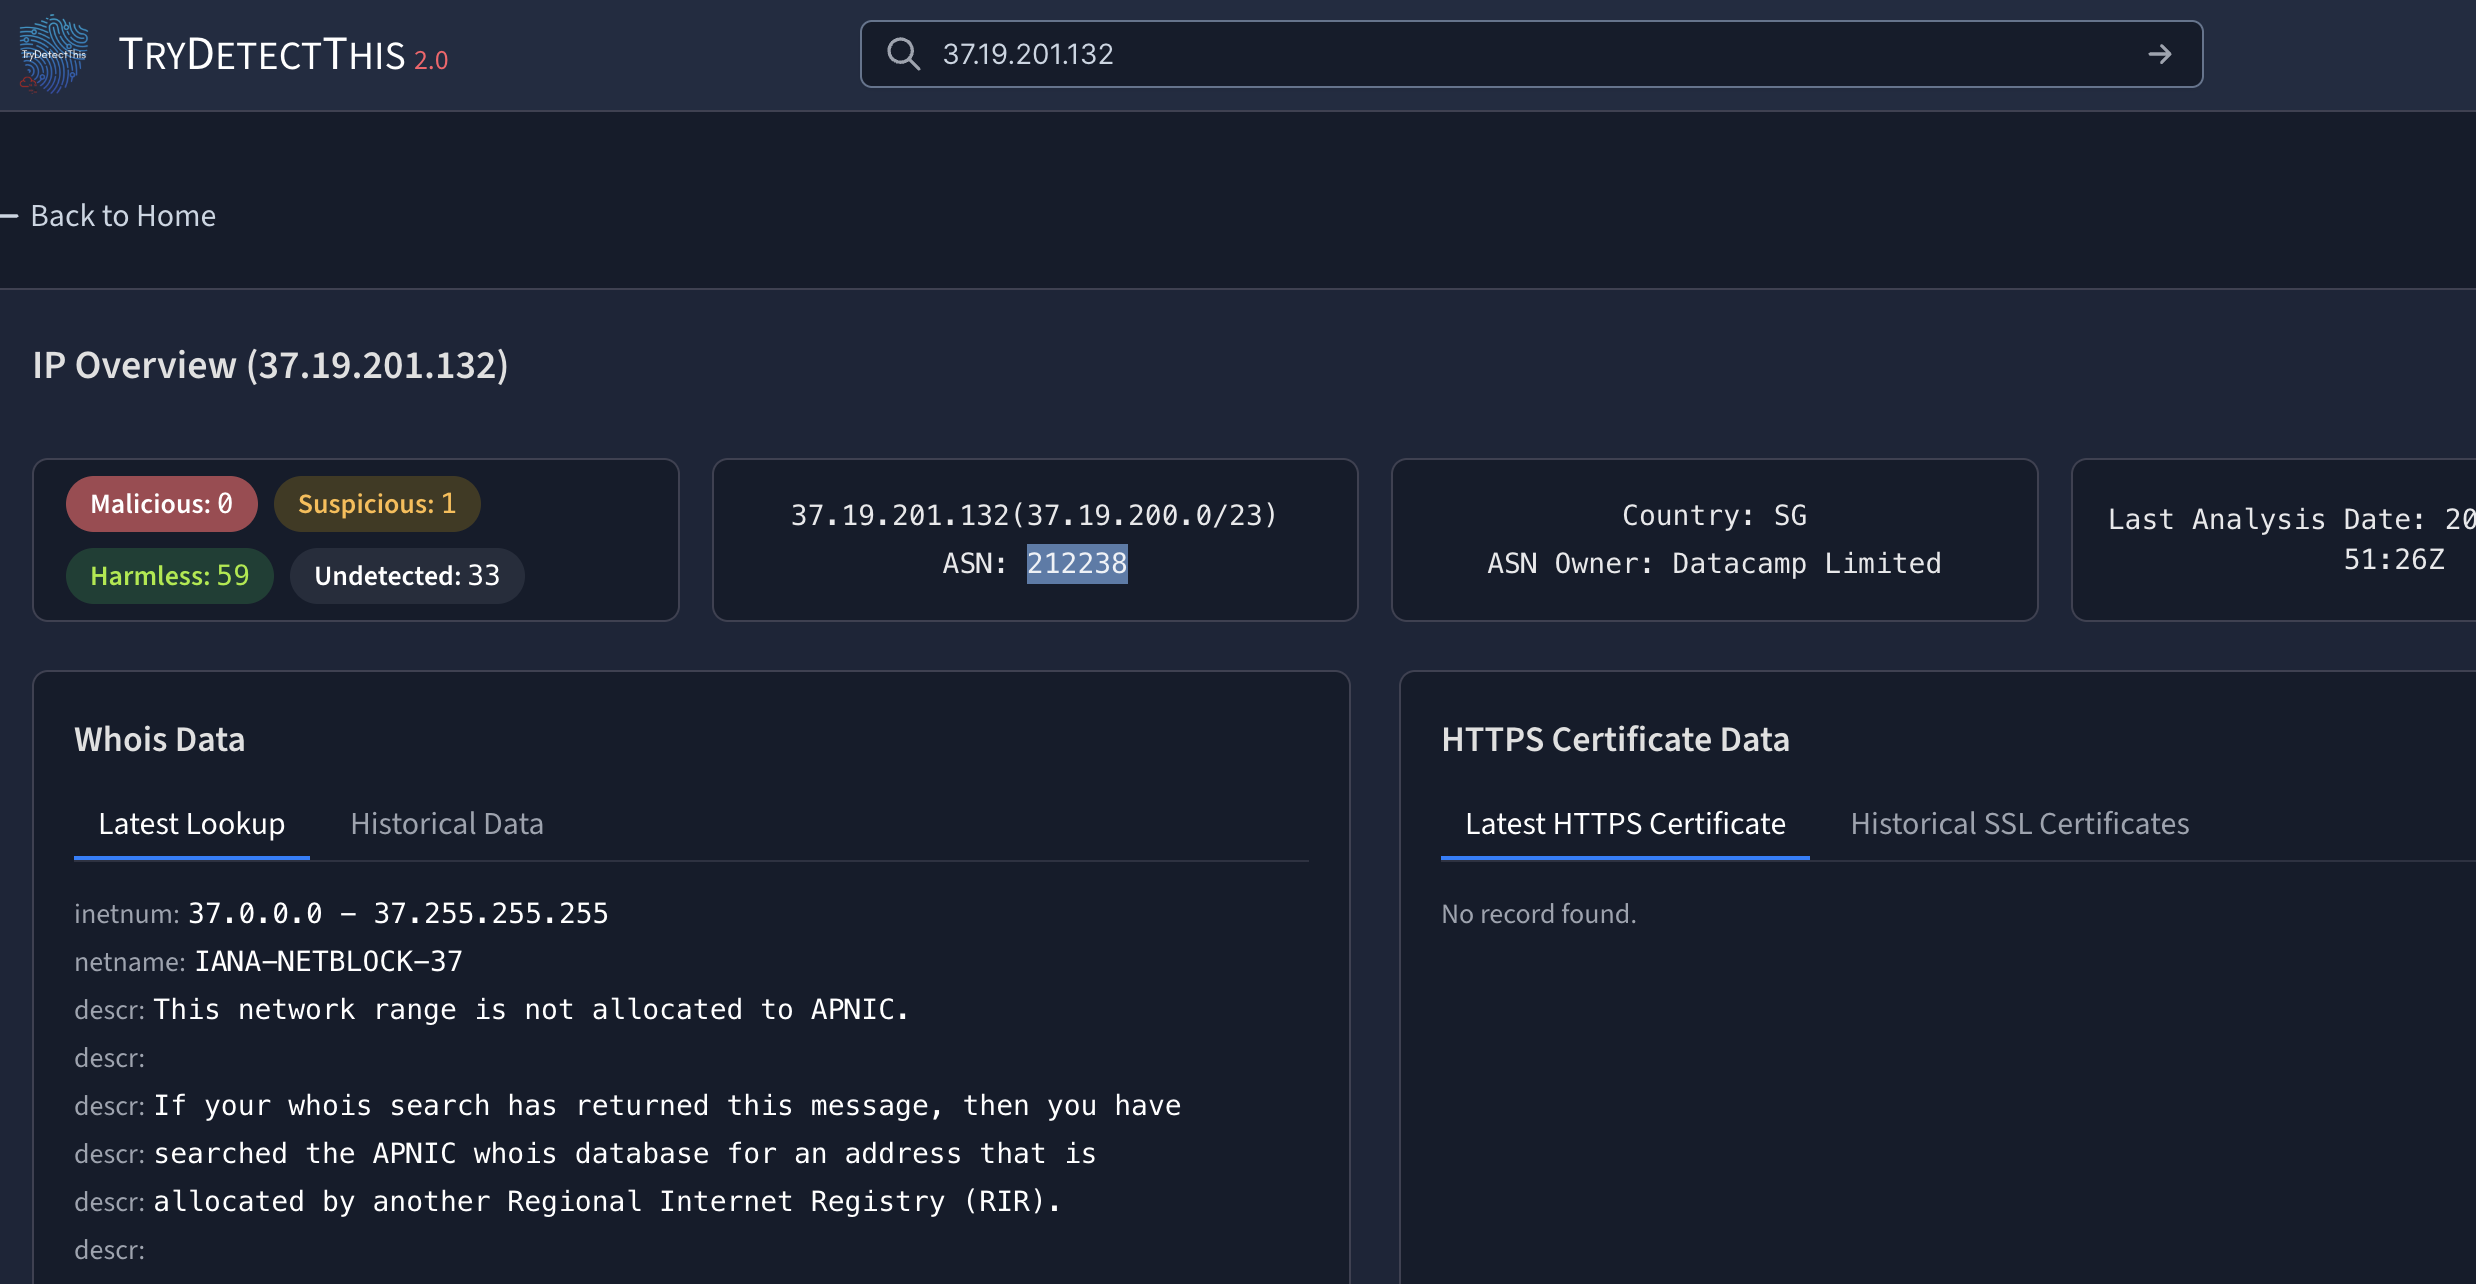
Which service is offered from this IP? vpn
What is the filename of the file related to the hash?
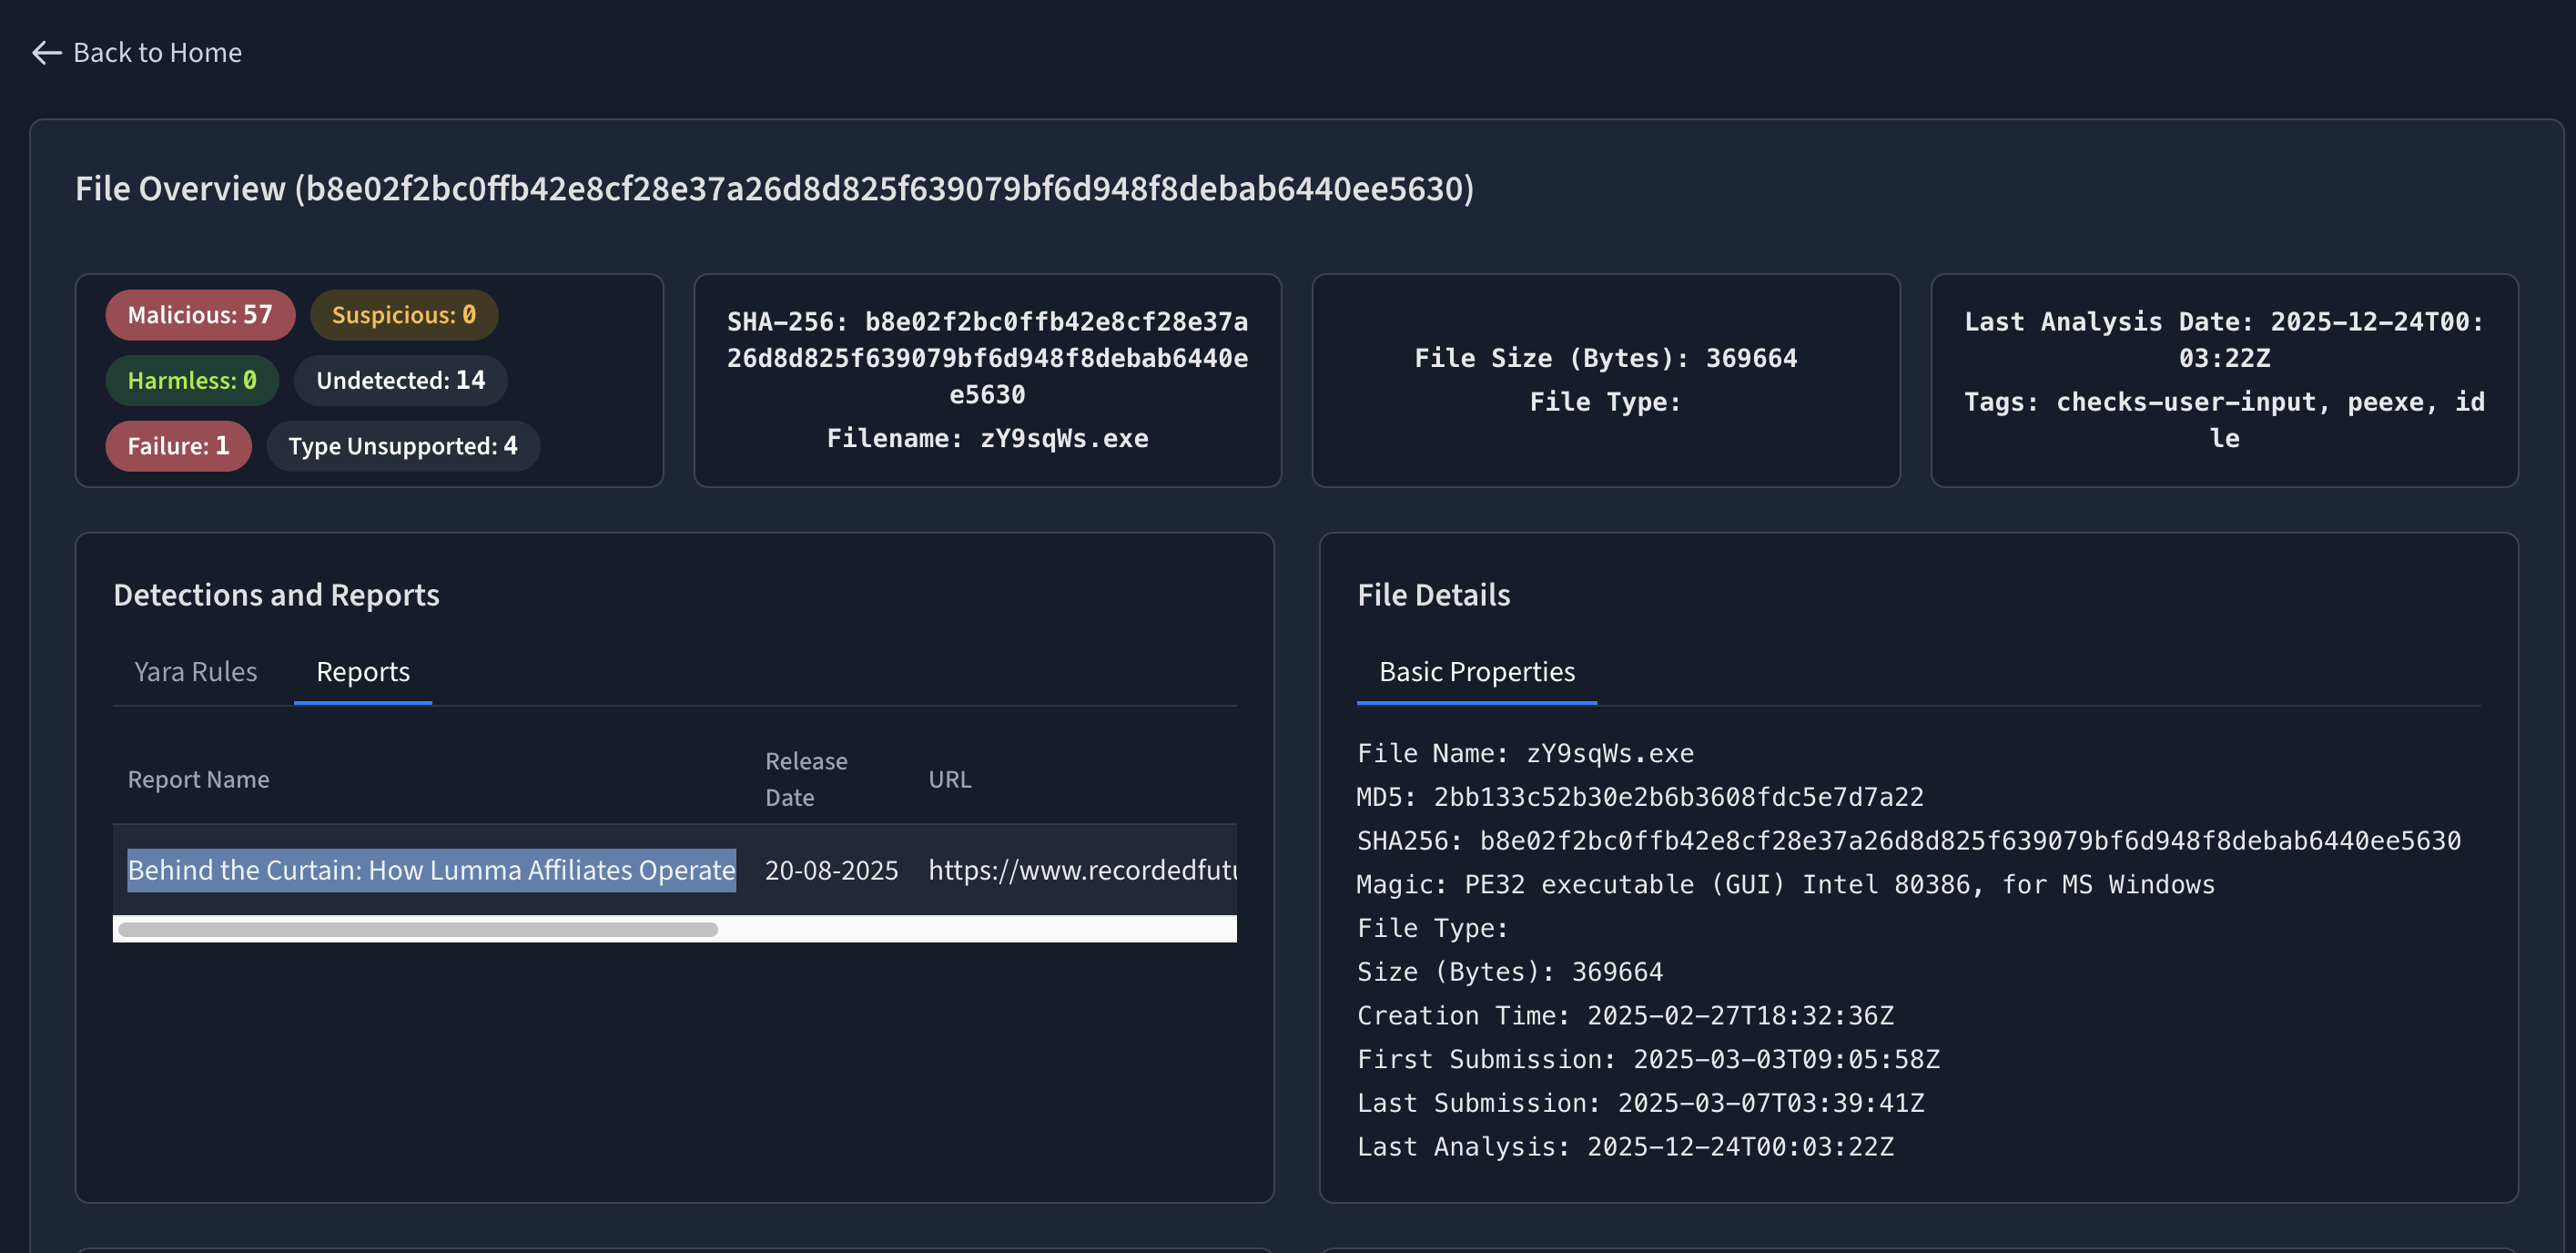
What is the threat signature that Microsoft assigned to the file? Trojan:Win32/LummaStealer.PM!MTB
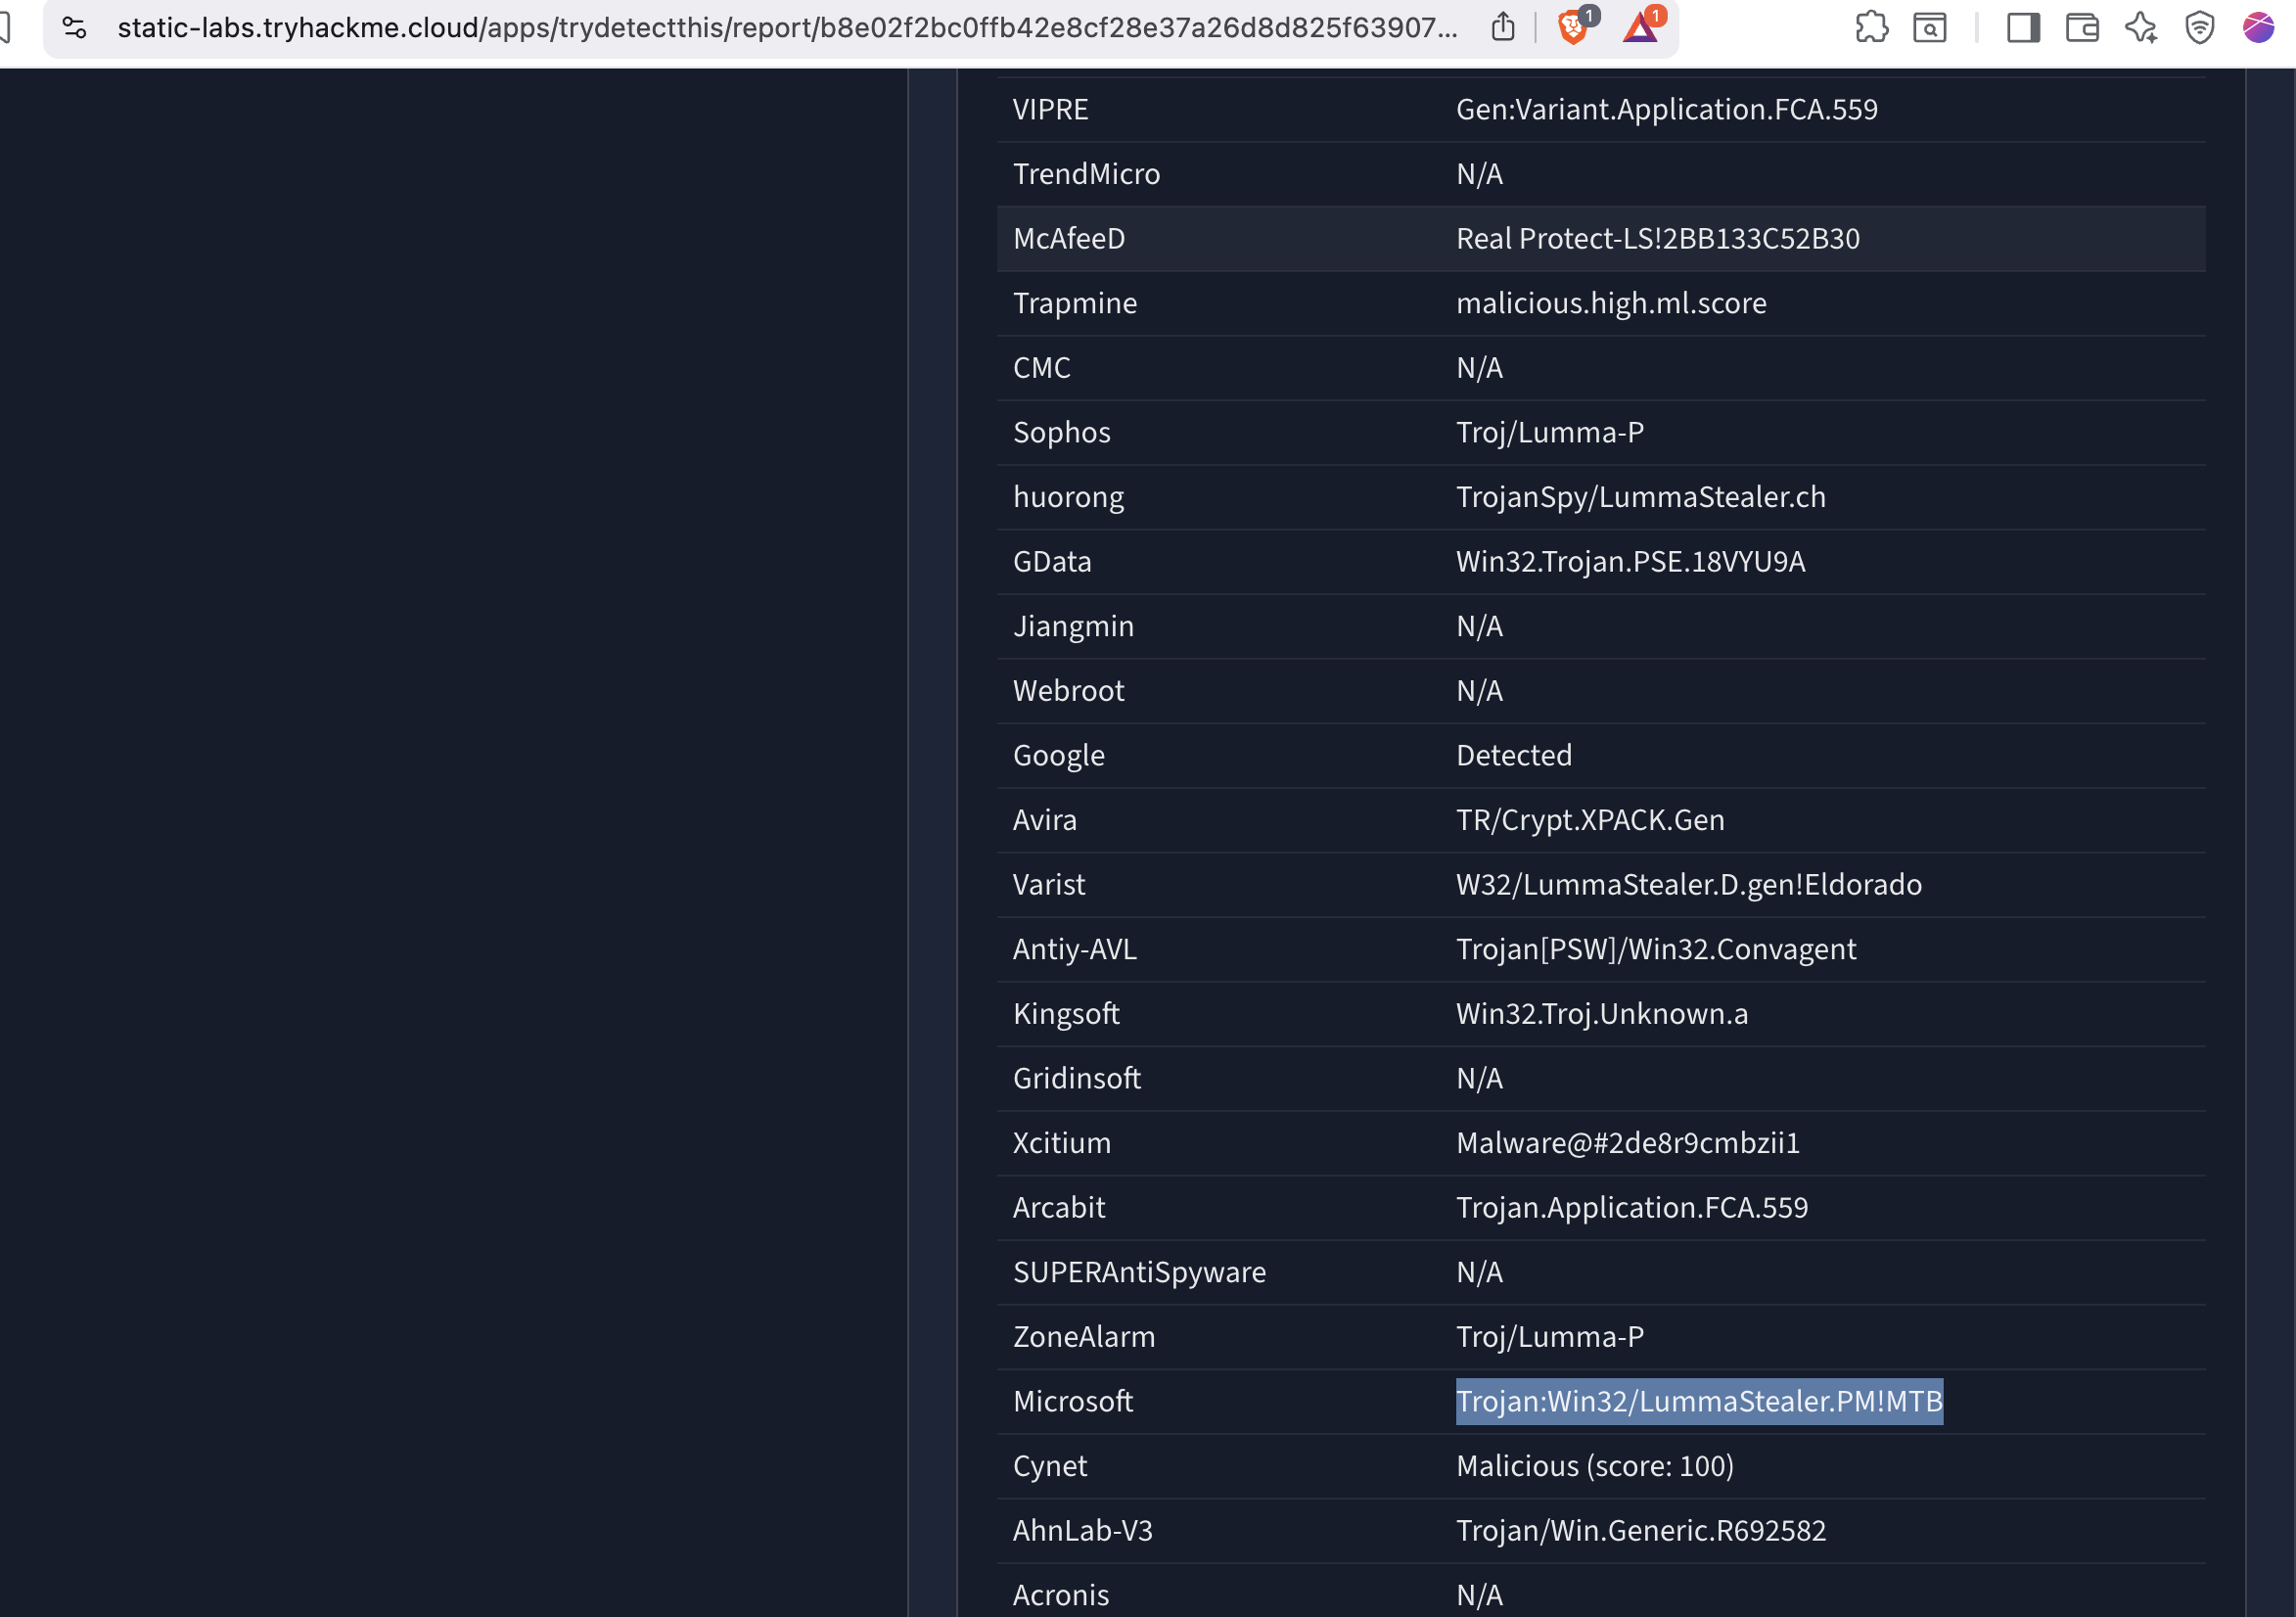
One of the contacted domains is part of a large malicious infrastructure cluster.
Based on its HTTPS certificate, how many domains are linked to the same campaign?
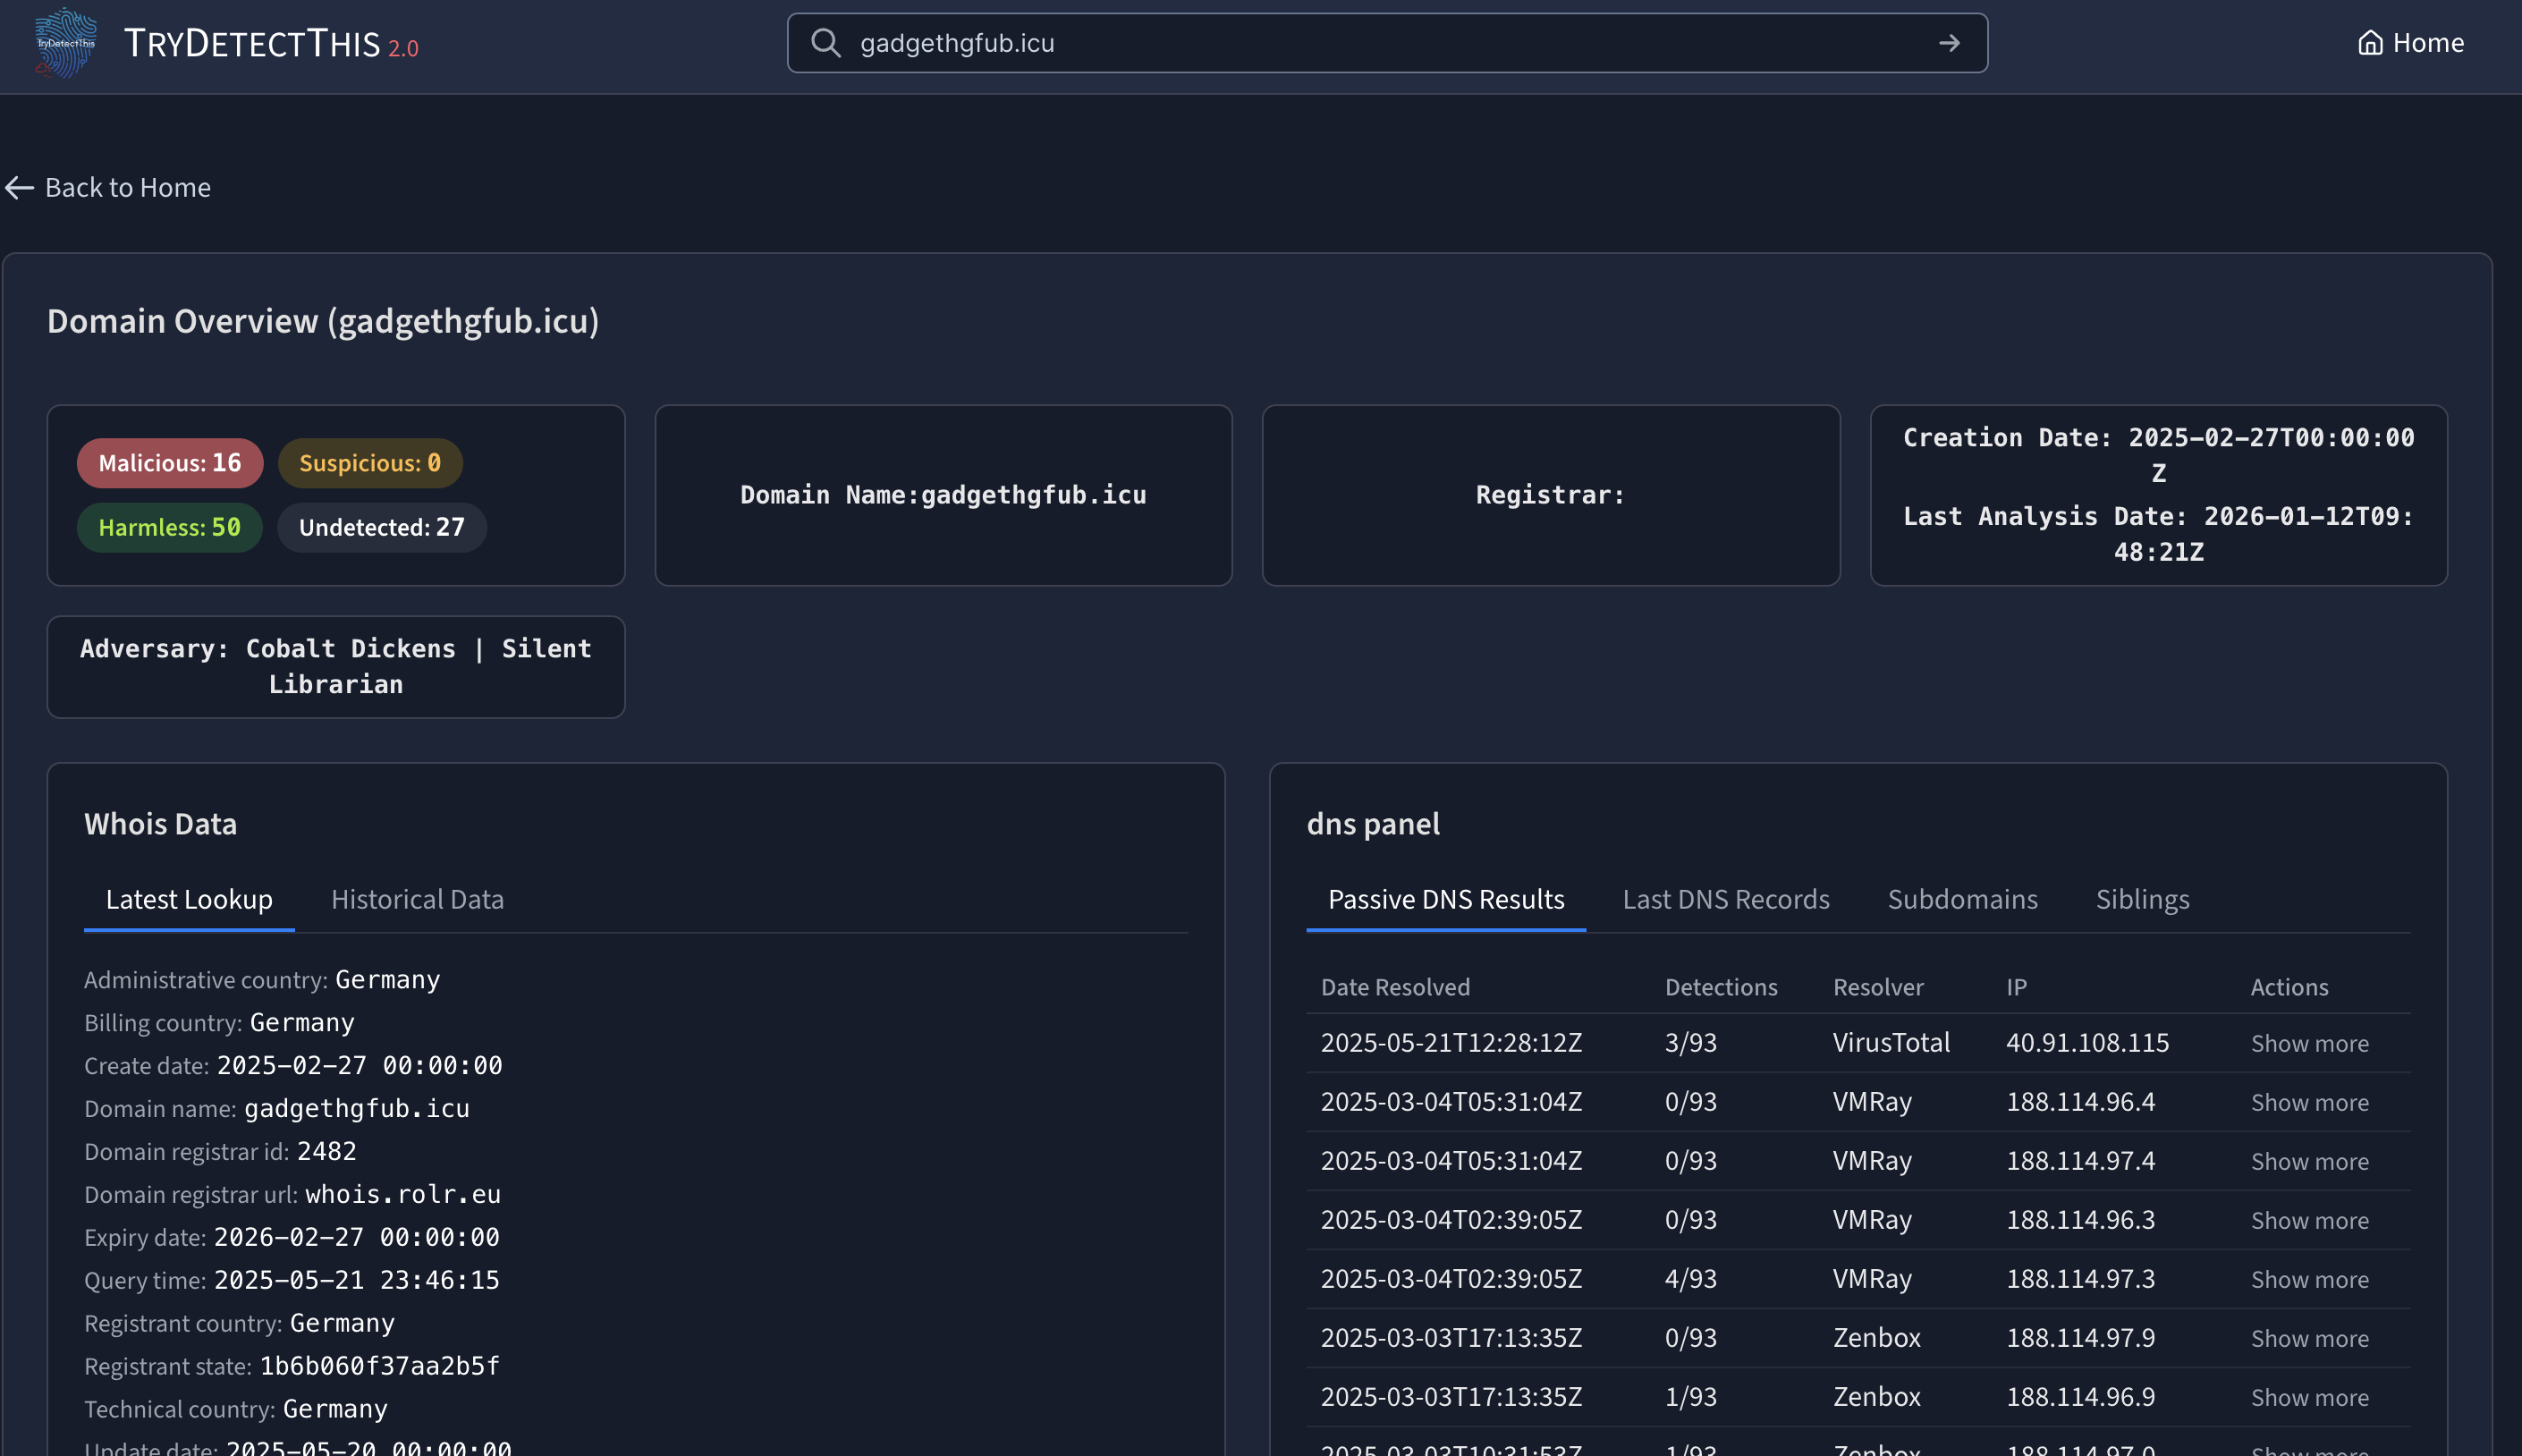
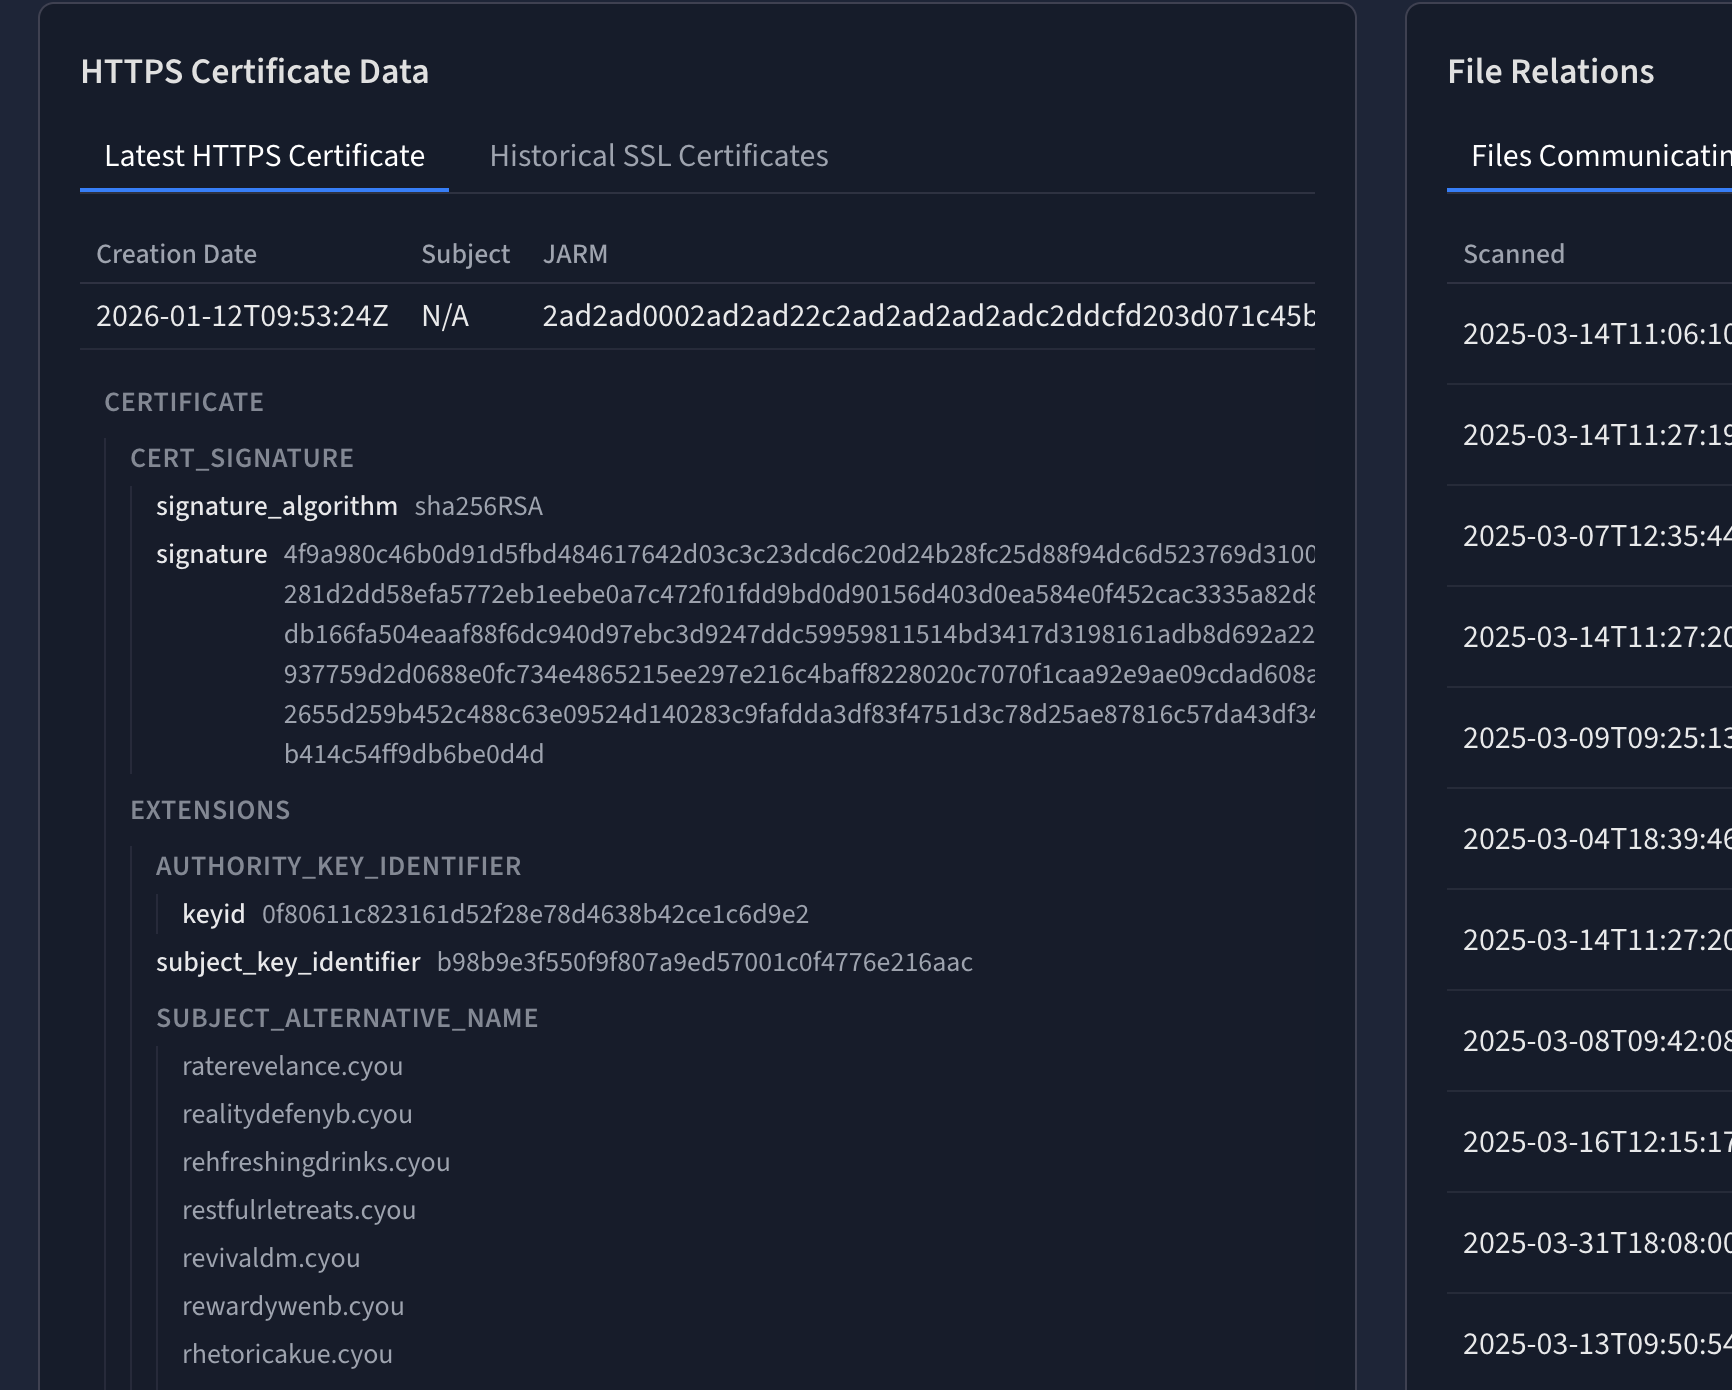
nano domains.txt

wc -l domains.txt
151 domains.txt
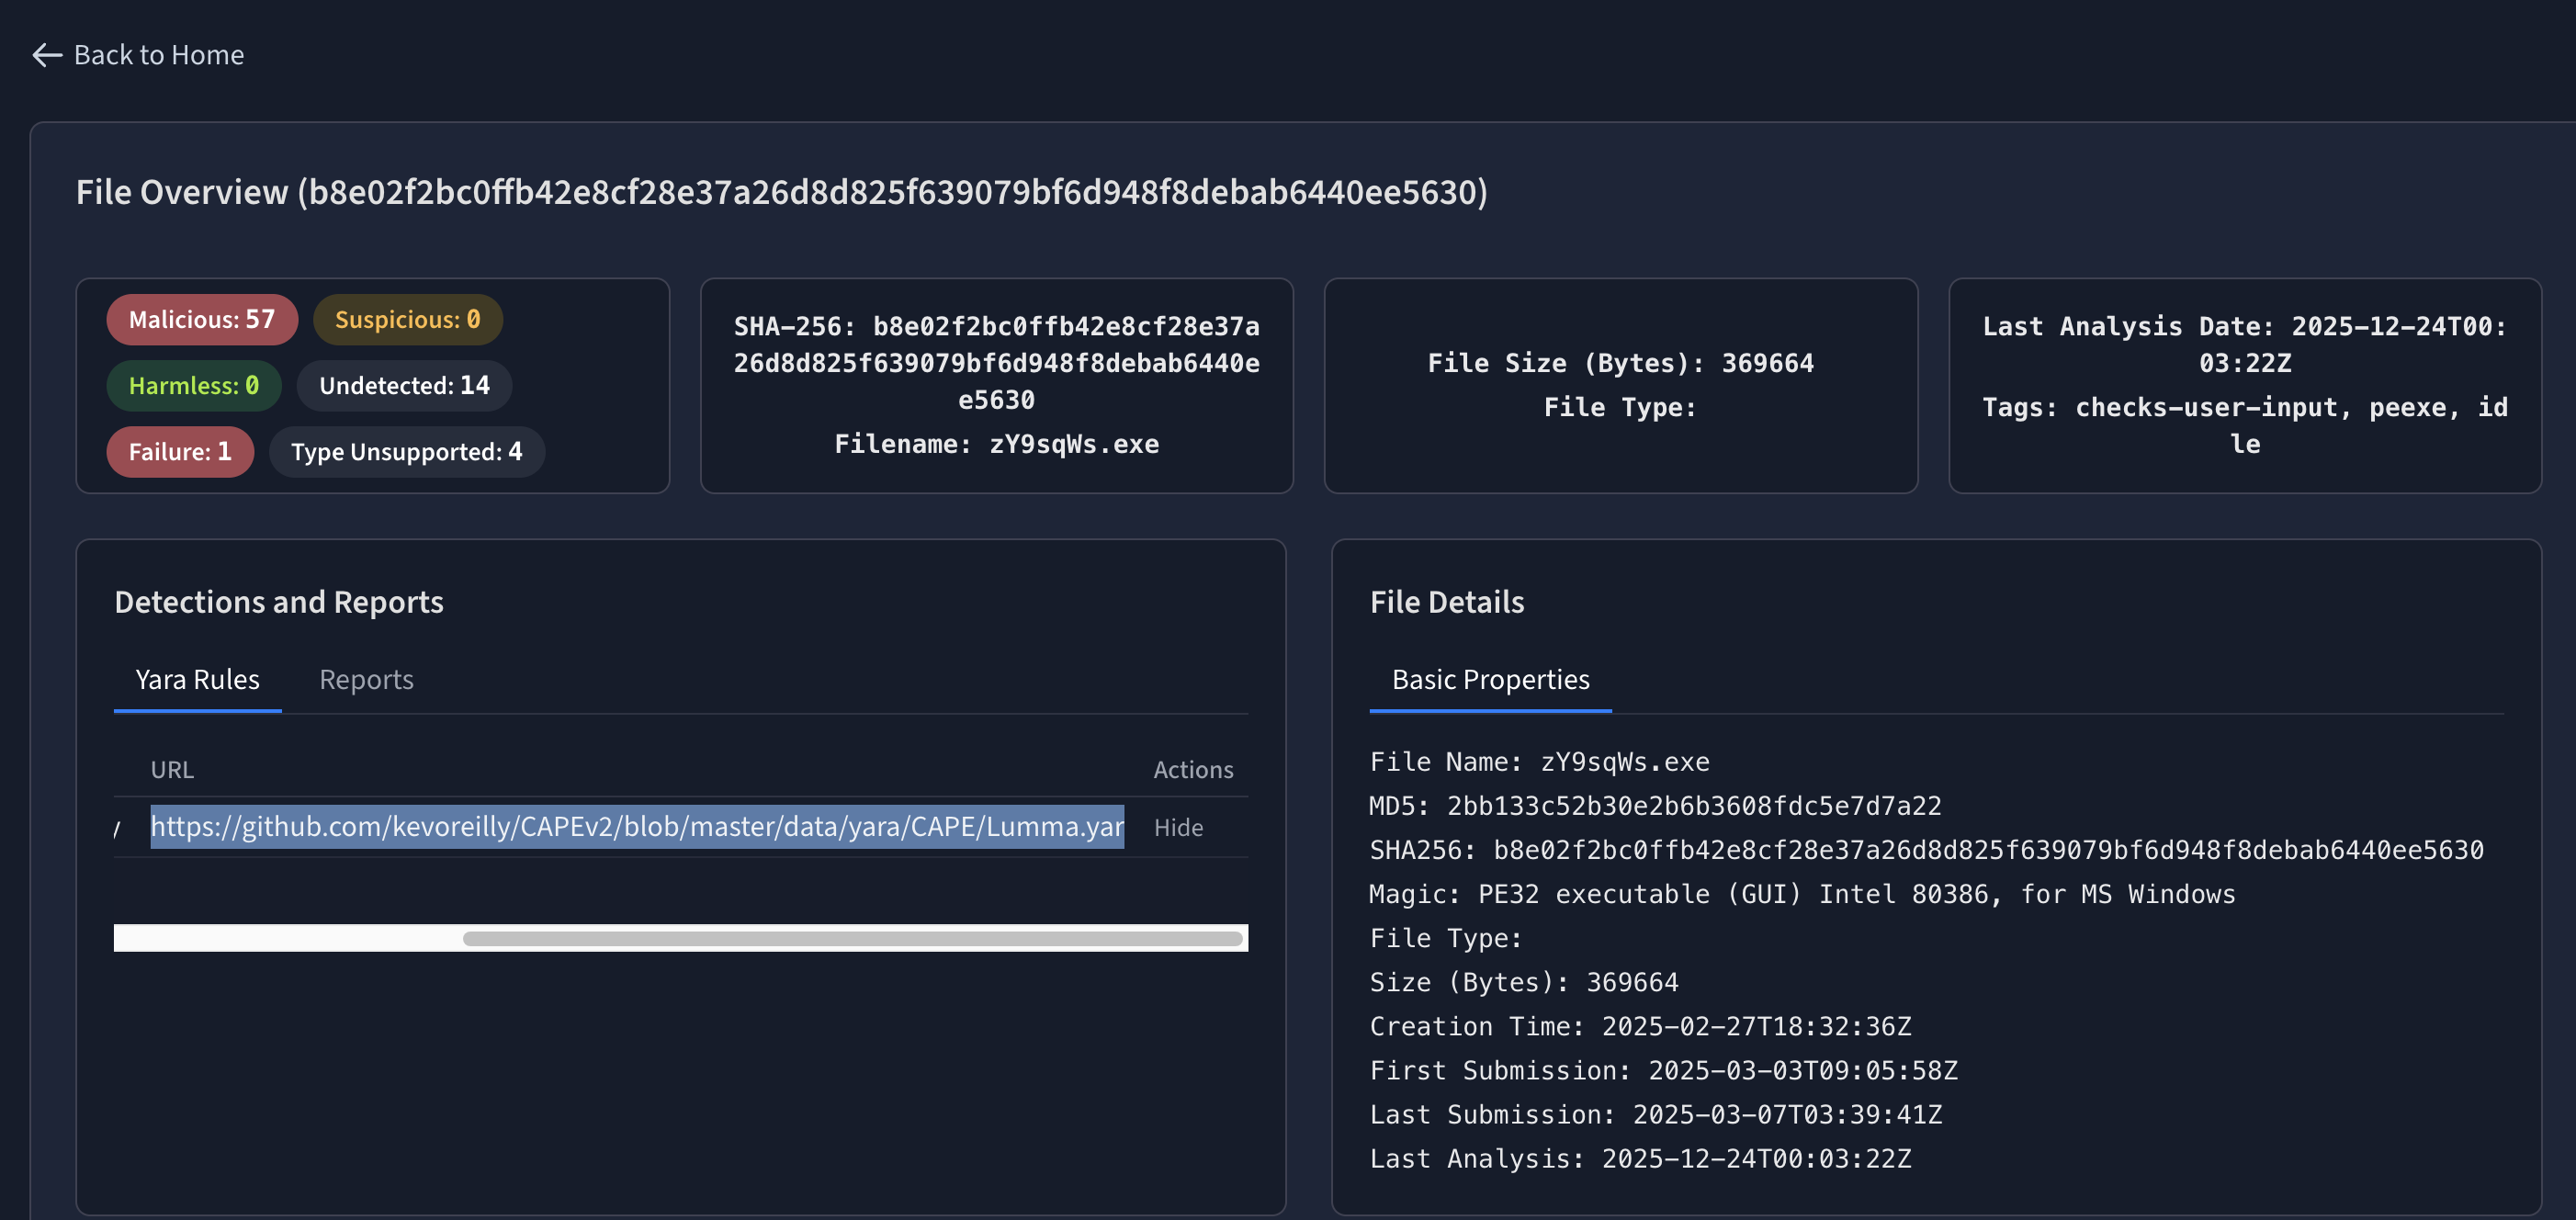
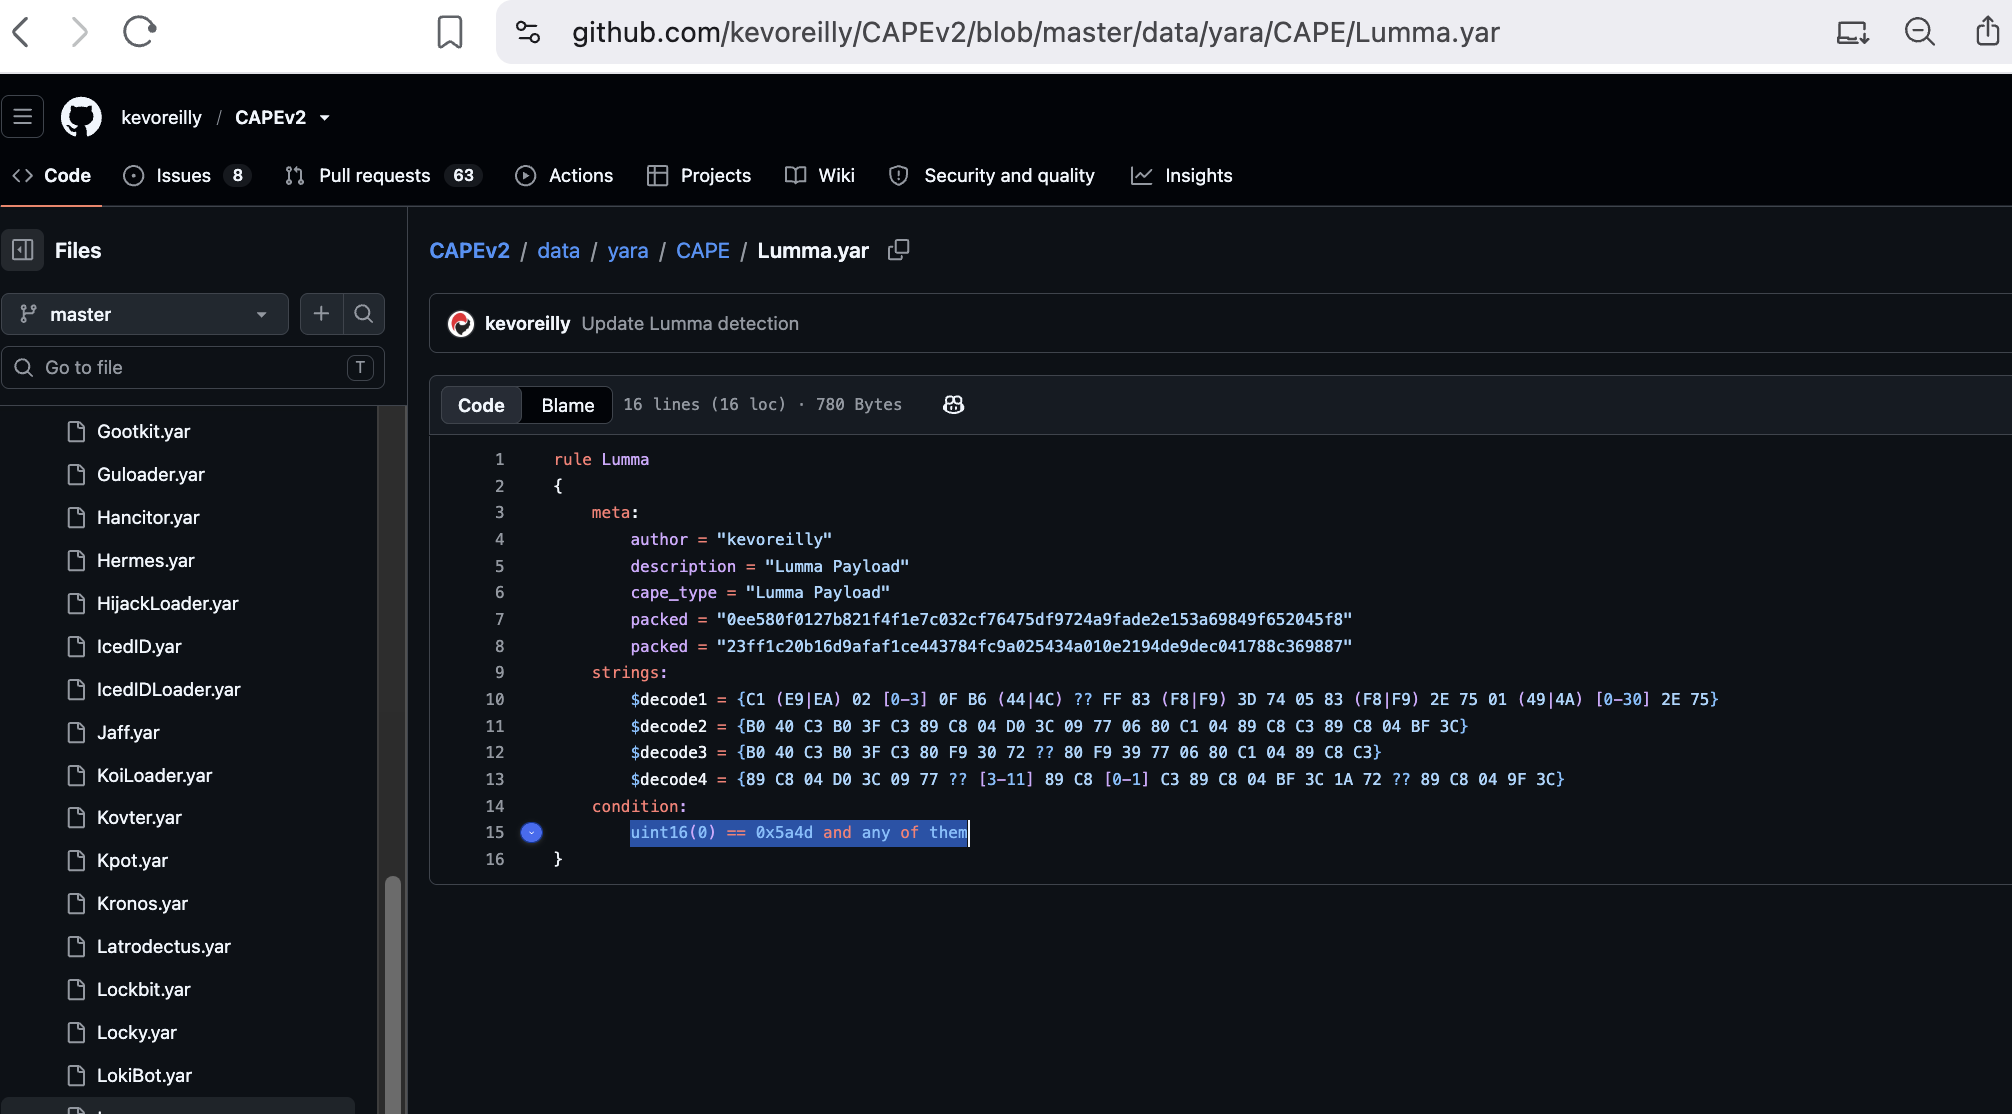
The file matches one of the YARA rules made by "kevoreilly".
What line is present in the rule's "condition" field?
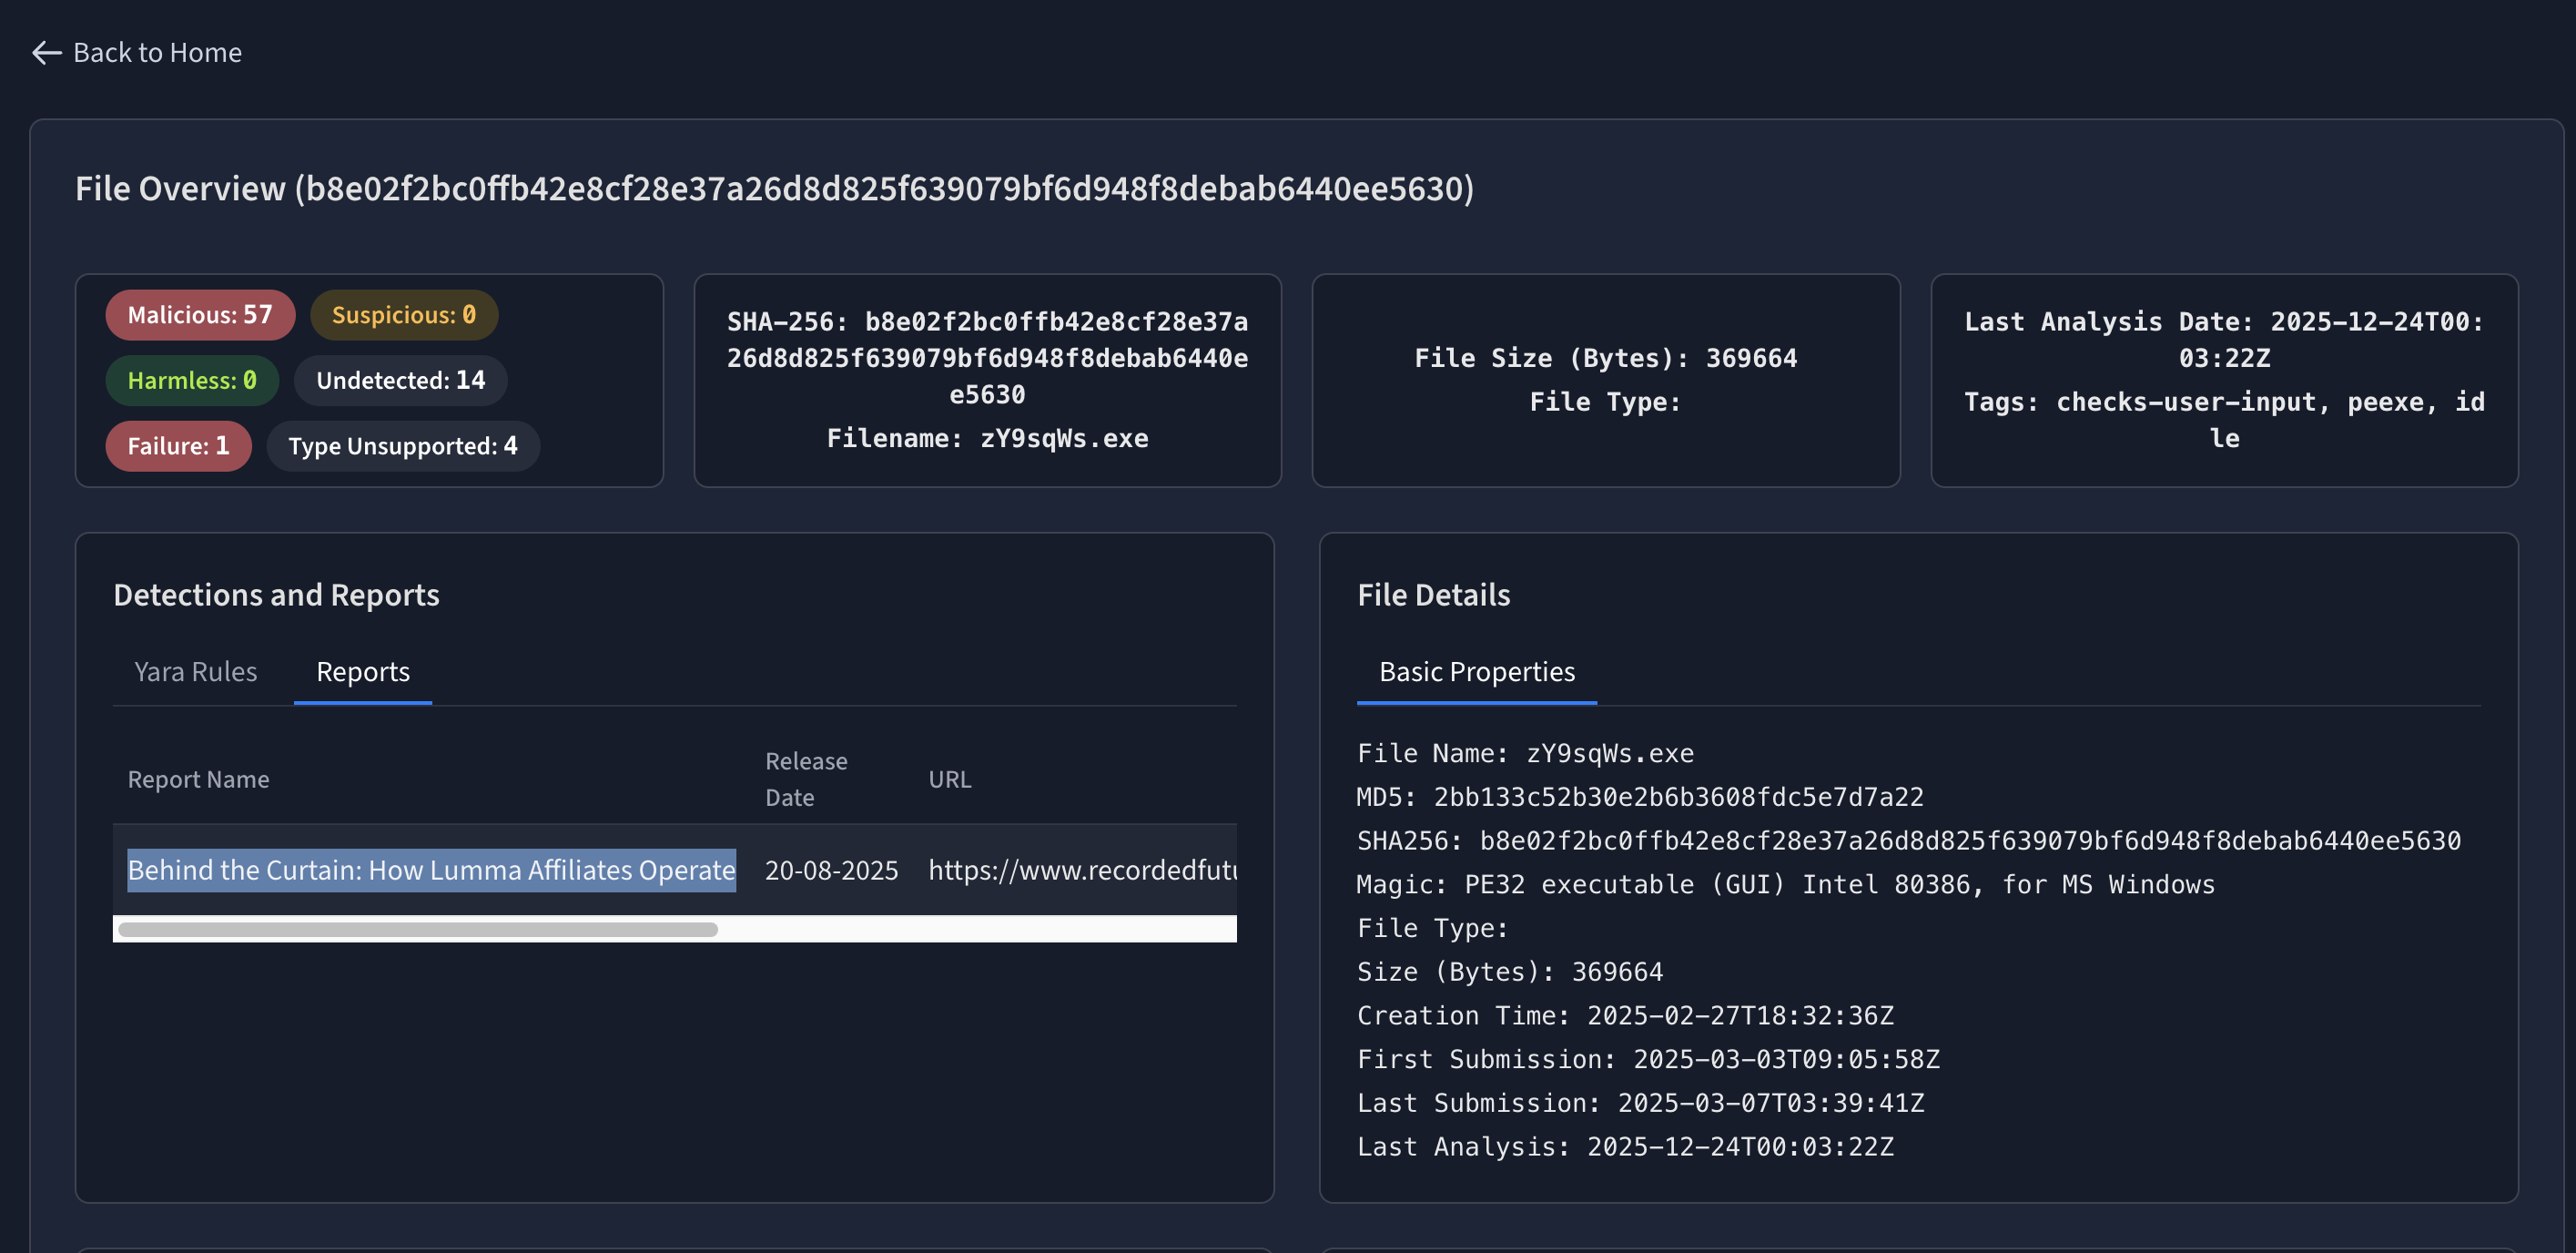
The file is also mentioned in a threat intel report.
What is the title of the report mentioning this hash?
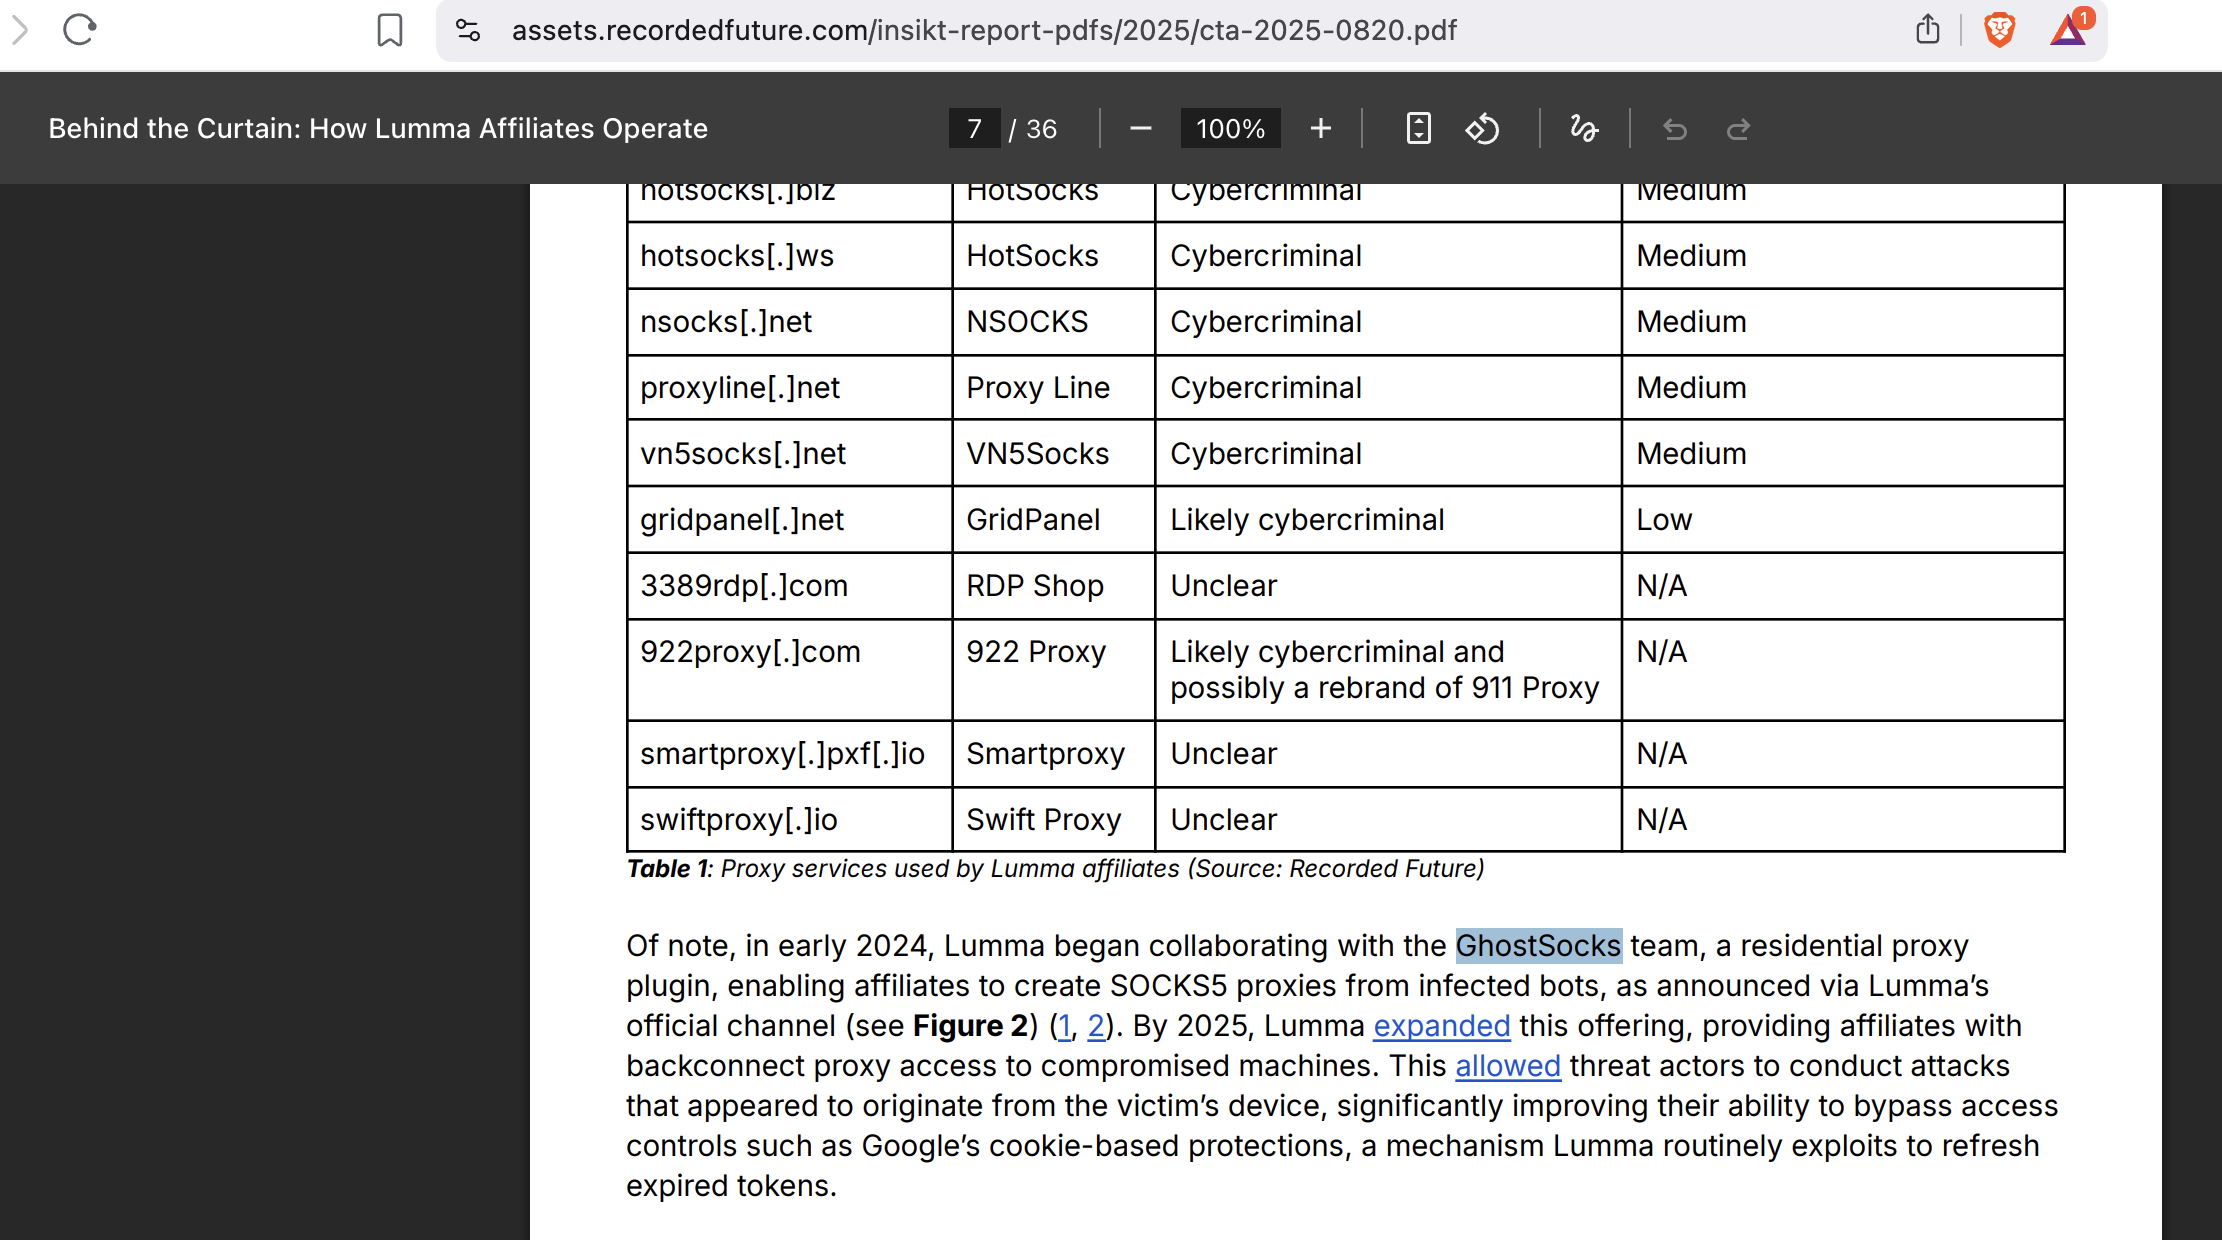
Which team did the author of the malware start collaborating with in early 2024?
A Mexican-based affiliate related to the malware family also uses other infostealers.
Which mentioned infostealer targets Android systems?
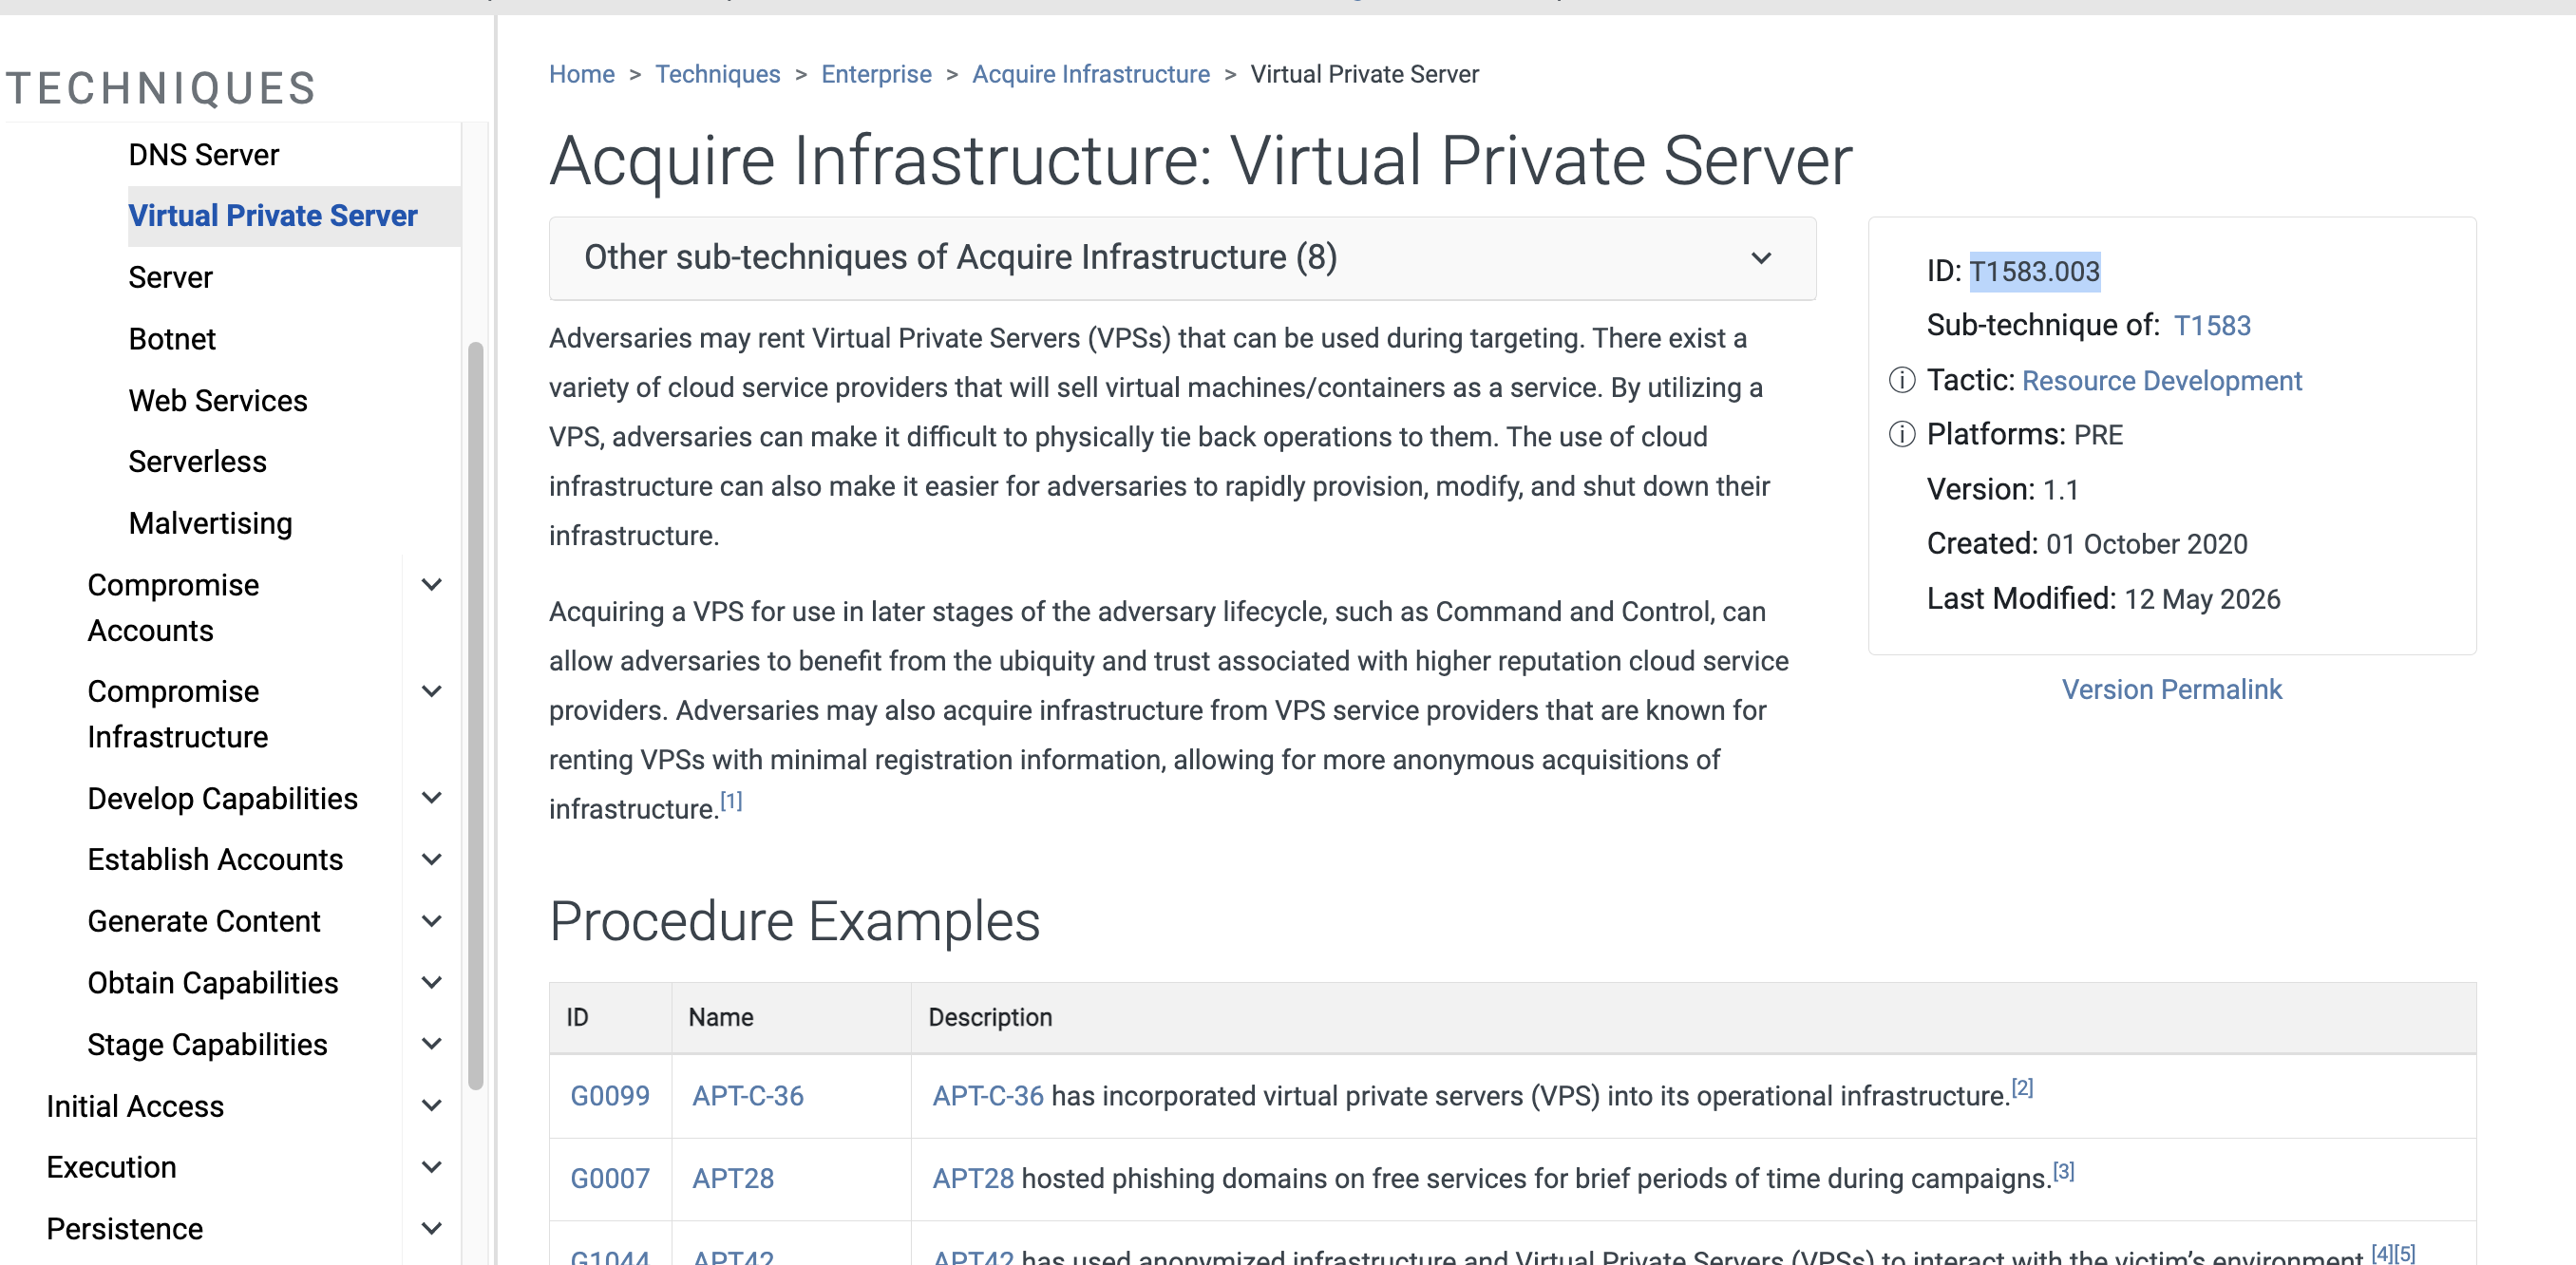
The report states that the affiliates behind the malware use the services of AnonRDP. Which Mitre ATT&CK sub-technique does this align with?