Link to the O365 Intrusion on TryHackMe
Active investigation
- High
Situation Report
Vantage Dynamics' IT team escalated a report from their Accounts Payable department on 27 August. An employee, Marcus Webb, noticed a colleague referencing a document tied to his account that he had no memory of sending. Around the same time, a second employee's account, David Chen, began showing signs of unusual activity of its own.
Vantage has not made any changes to either account and has handed over sign-in and activity logs from the day of the incident. TSS has been engaged to determine how the intrusion began, how it spread between accounts, and whether any sensitive data left the organization.
Internal Message
FROM: Mara Okafor, Lead Incident Response Analyst
TO: You
SUBJECT: RE: Vantage - The O365 Intrusion
Start with Marcus Webb's sign-in history for the day. I pulled a few details from the company beforehand, and it looks like every employee is issued a company managed MacBook as standard.
Marcus is not the only one on that team who messages colleagues and shares files constantly, so do not assume every message or share you find is part of the incident. Check whether it fits the account's usual behavior first.
Once you have the entry point, I want the persistence mechanism next, then trace whether this reached anyone else.
Mission Parameters
- 01: Establish how Marcus Webb's account was initially compromised.
- 02: Determine what the attacker did immediately after gaining access.
- 03: Identify the persistence mechanism left on the mailbox.
- 04: Trace how the attacker moved from Marcus Webb's account to a second identity.
- 05: Confirm what sensitive data was accessed and whether it left the organization.
Assigned Personnel
- Mara Okafor: Lead Incident Response Analyst
- You: Assigned Analyst
Case Briefing
Just one wrong login.
You have been brought on at THM Security Services (TSS). Click the card below to reveal your role on this case.
Your case briefing is waiting in the TSS Operations Hub. Head to the Active Case tab for everything you need before you begin. The other tabs are there if you want to explore the company, the team, or previous cases.
Prerequisites
It is recommended to go through the Microsoft 365 for SOC module before proceeding with this case.
The Investigation
Having reviewed the case details on the TSS Operations Hub, it is time to begin your investigation.
To access Splunk, follow this link: https://LAB_WEB_URL.p.thmlabs.com
Apply index=vantage with the All time filter and examine the evidence to answer the questions given below.
Answer the questions below
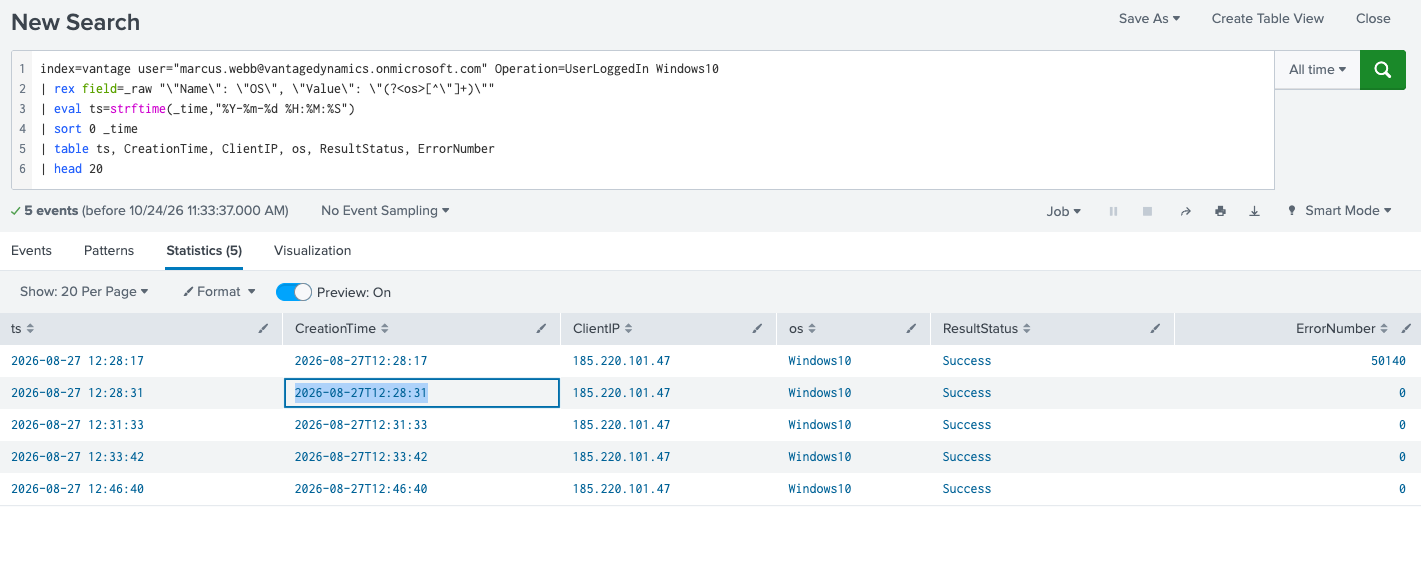
What is the first timestamp at which a non-macOS device signed into Marcus Webb's account? (Format: YYYY-MM-DD HH:MM:SS)
index=vantage user="marcus.webb@vantagedynamics.onmicrosoft.com" Operation=UserLoggedIn Windows10
| rex field=_raw "\"Name\": \"OS\", \"Value\": \"(?<os>[^\"]+)\""
| eval ts=strftime(_time,"%Y-%m-%d %H:%M:%S")
| sort 0 _time
| table ts, CreationTime, ClientIP, os, ResultStatus, ErrorNumber
| head 20
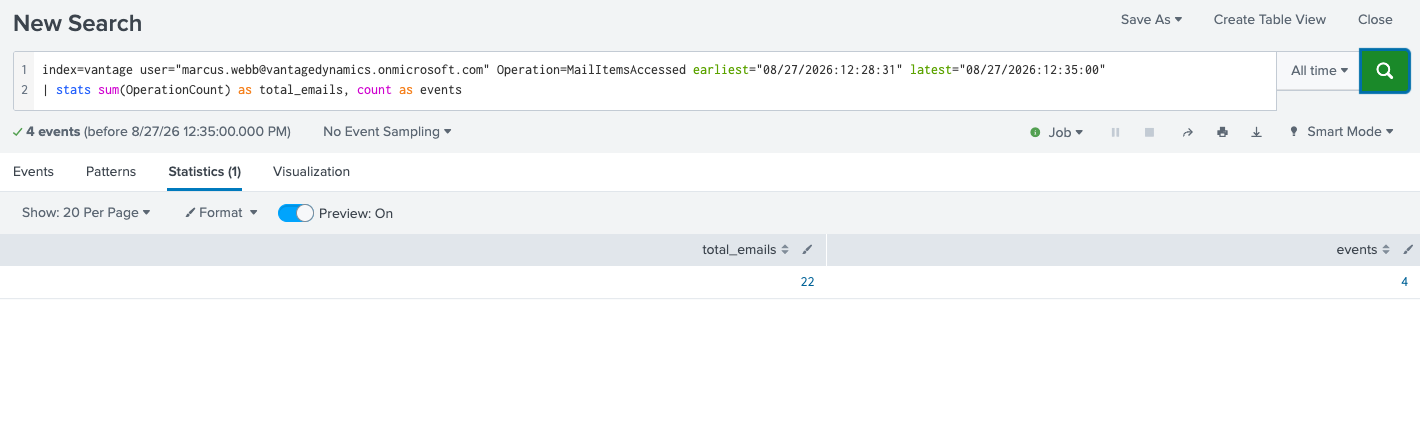
Just after logging in, the attacker accessed a large number of emails within the first few minutes of the session. How many emails were accessed during this window?
index=vantage user="marcus.webb@vantagedynamics.onmicrosoft.com" Operation=MailItemsAccessed earliest="08/27/2026:12:28:31" latest="08/27/2026:12:35:00"
| stats sum(OperationCount) as total_emails, count as events
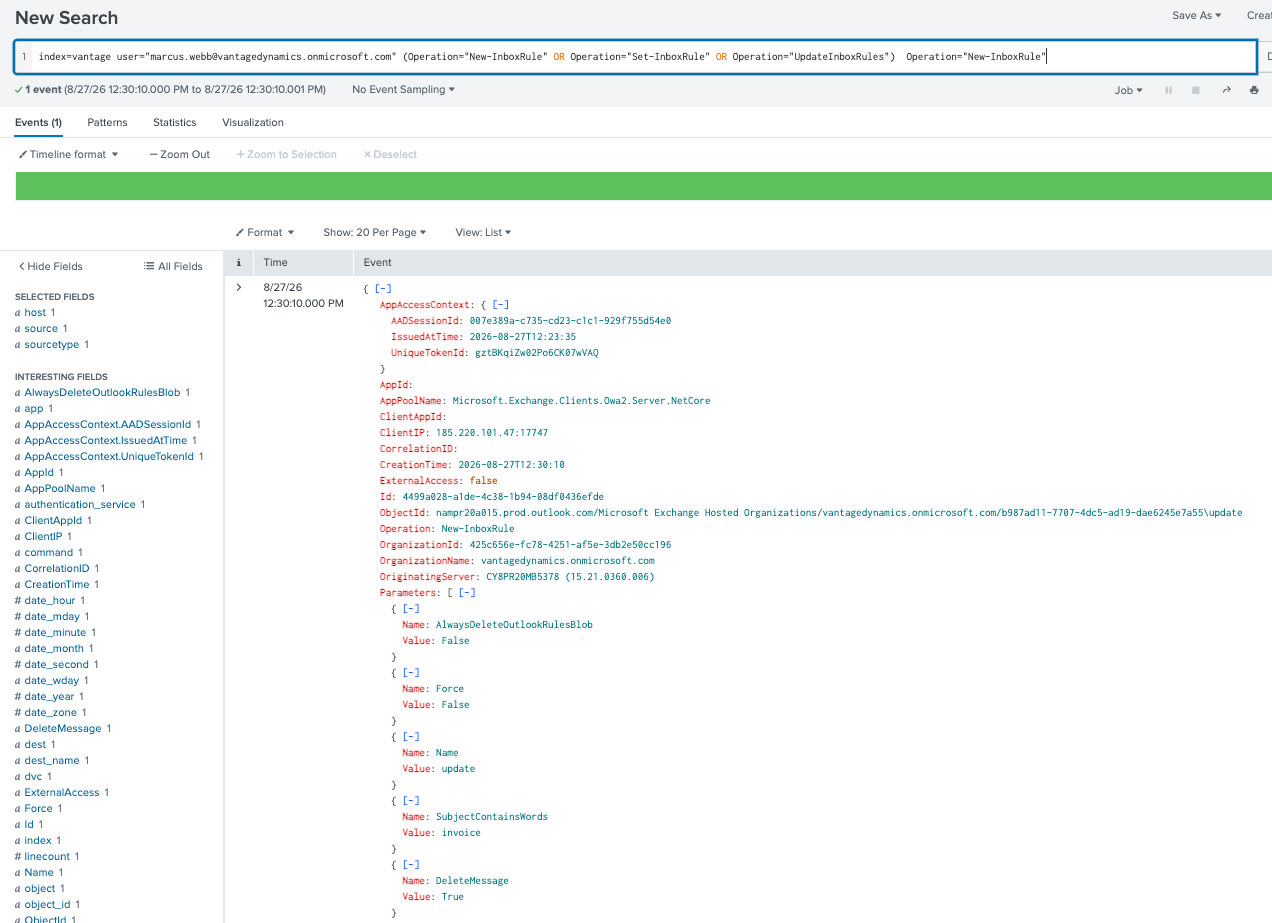
What subject line does the attacker's inbox rule match on?
index=vantage user="marcus.webb@vantagedynamics.onmicrosoft.com" (Operation="New-InboxRule" OR Operation="Set-InboxRule" OR Operation="UpdateInboxRules") Operation="New-InboxRule"
- The answer is one of the values under the parameters below -
subjectcontainswords
How much time elapsed between the malicious inbox rule being created and a matching reply email arriving in the mailbox? (e.g. 2 minutes 51 seconds)
index=vantage invoice action=delivered
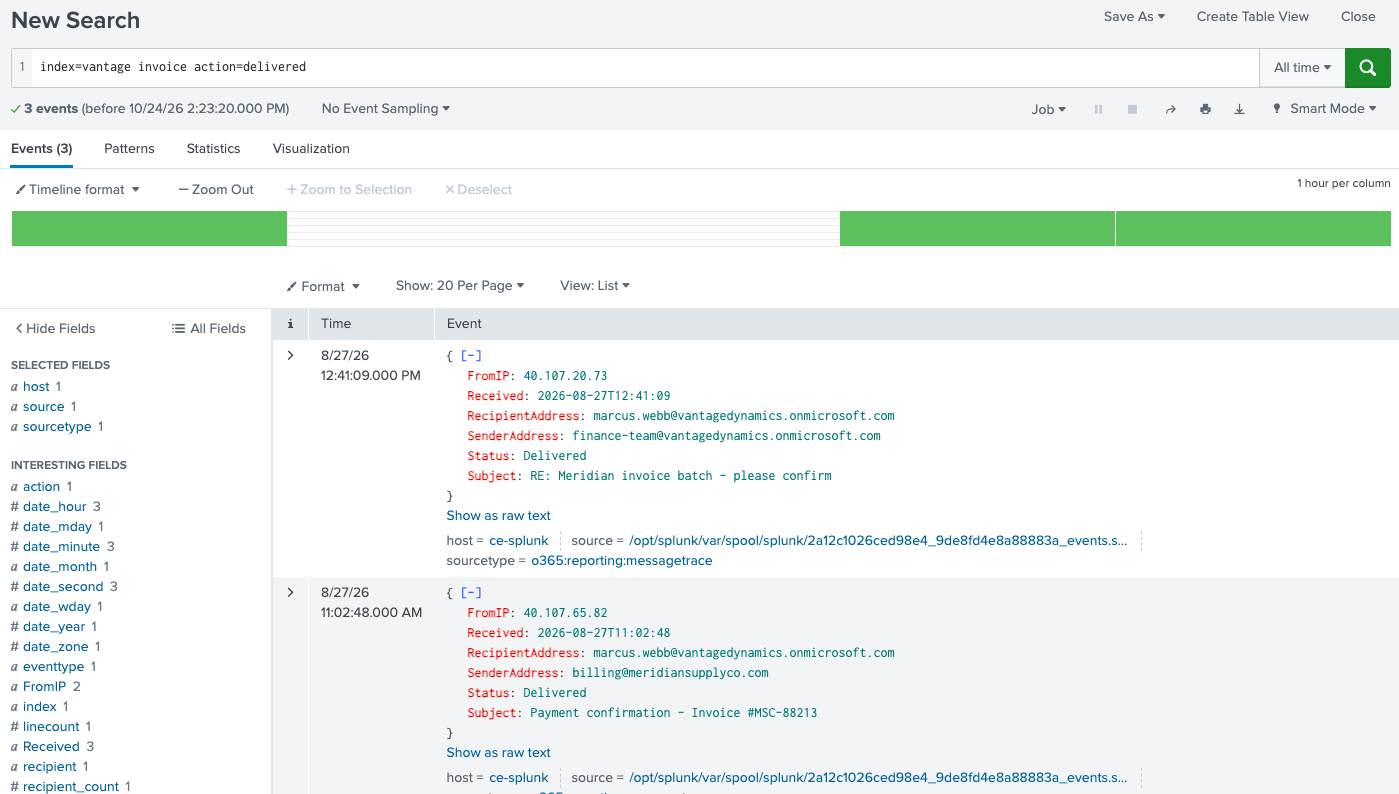
- Rule created (
New-InboxRule): 12:30:10- Matching reply delivered (message trace): 12:41:09,
RE: Meridian invoice batch - please confirm, fromfinance-team@vantagedynamics.onmicrosoft.com, statusDelivered- Difference: 12:41:09 − 12:30:10
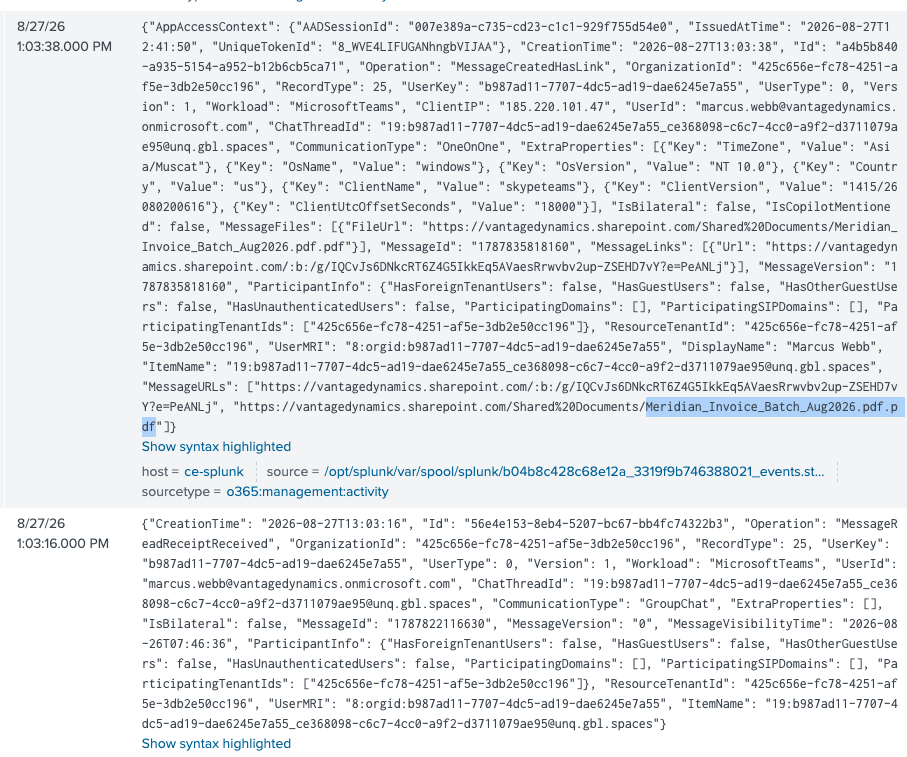
Marcus Webb's account logged a Teams message that had a link attached to it. What file did this link reference?
index=vantage user="marcus.webb@vantagedynamics.onmicrosoft.com" app=MicrosoftTeams
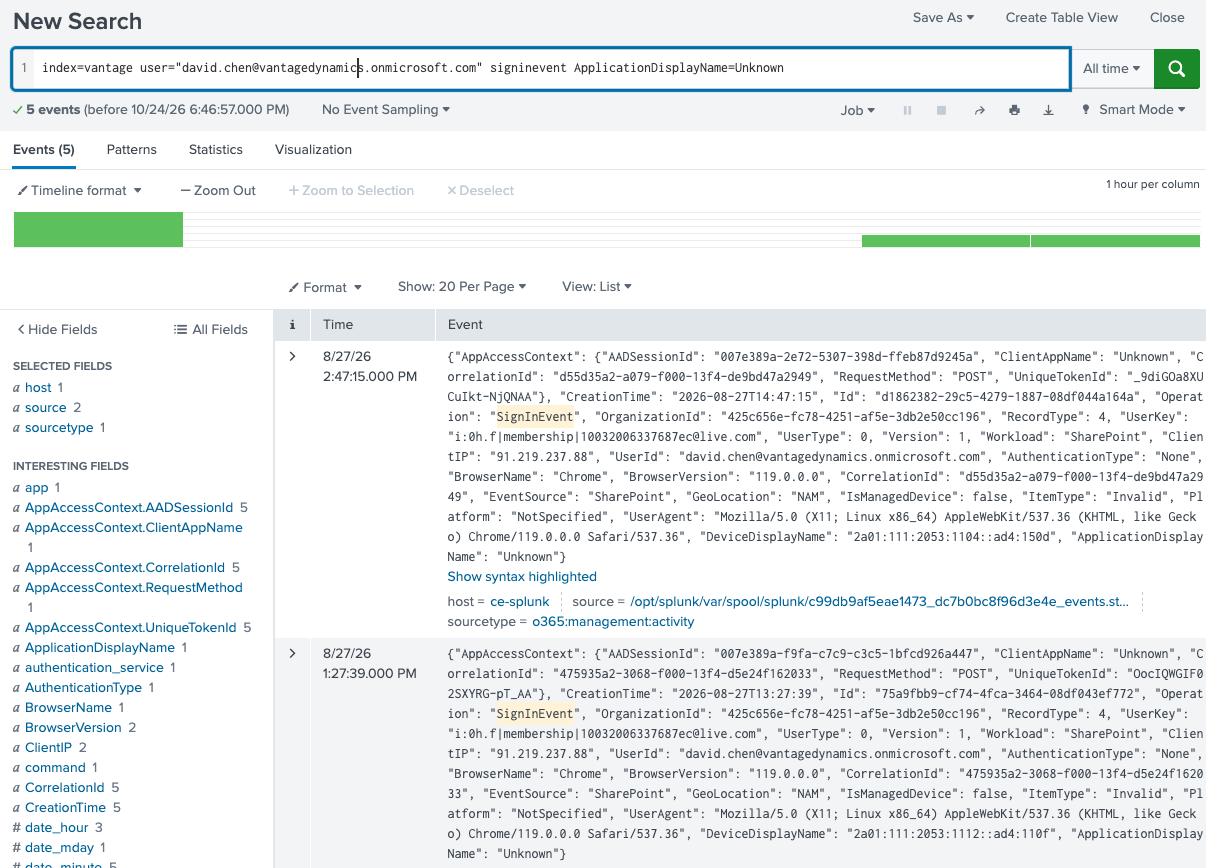
What operating system was used in the suspicious sign-in to David Chen's account?
index=vantage user="david.chen@vantagedynamics.onmicrosoft.com" signinevent ApplicationDisplayName=Unknown
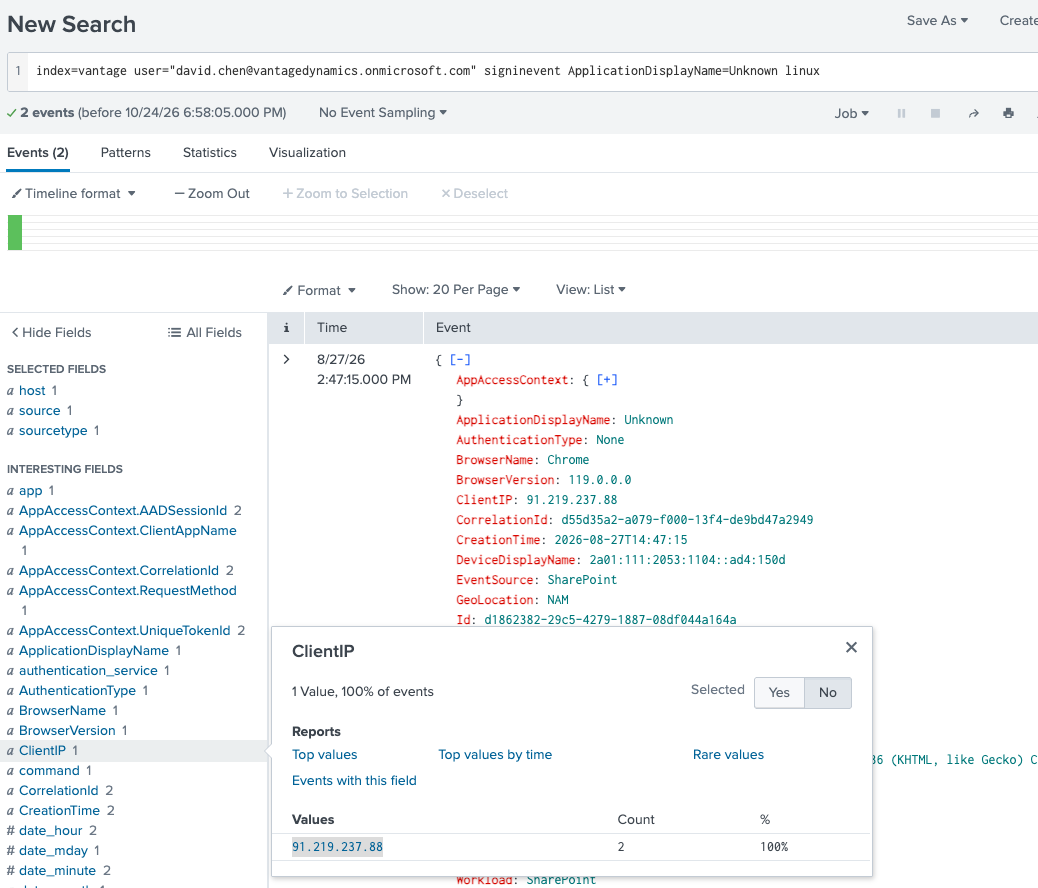
What IP address was used in this same sign-in?
index=vantage user="david.chen@vantagedynamics.onmicrosoft.com" signinevent ApplicationDisplayName=Unknown linux
How much time passed between this message being created and the suspicious sign-in to David Chen's account? (e.g. 2 minutes 51 seconds)
index=vantage user="david.chen@vantagedynamics.onmicrosoft.com" earliest="08/27/2026:13:03:38"
| eval ts=strftime(_time,"%Y-%m-%d %H:%M:%S")
| sort 0 _time
| table ts, Operation, ClientIP, UserAgent, ResultStatus
| head 15
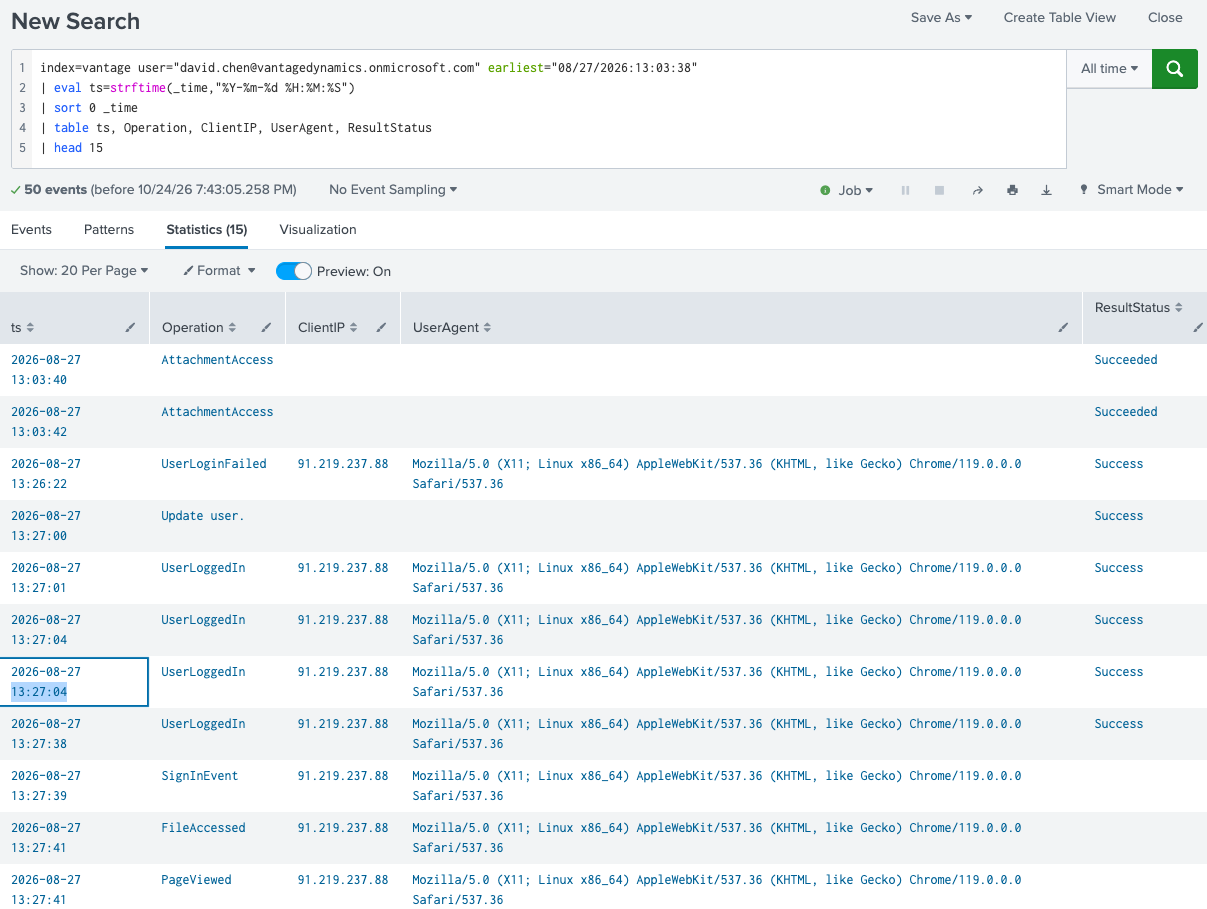
- 13:27:04
- 13:03:38
- Difference: 13:27:04 − 13:03:38
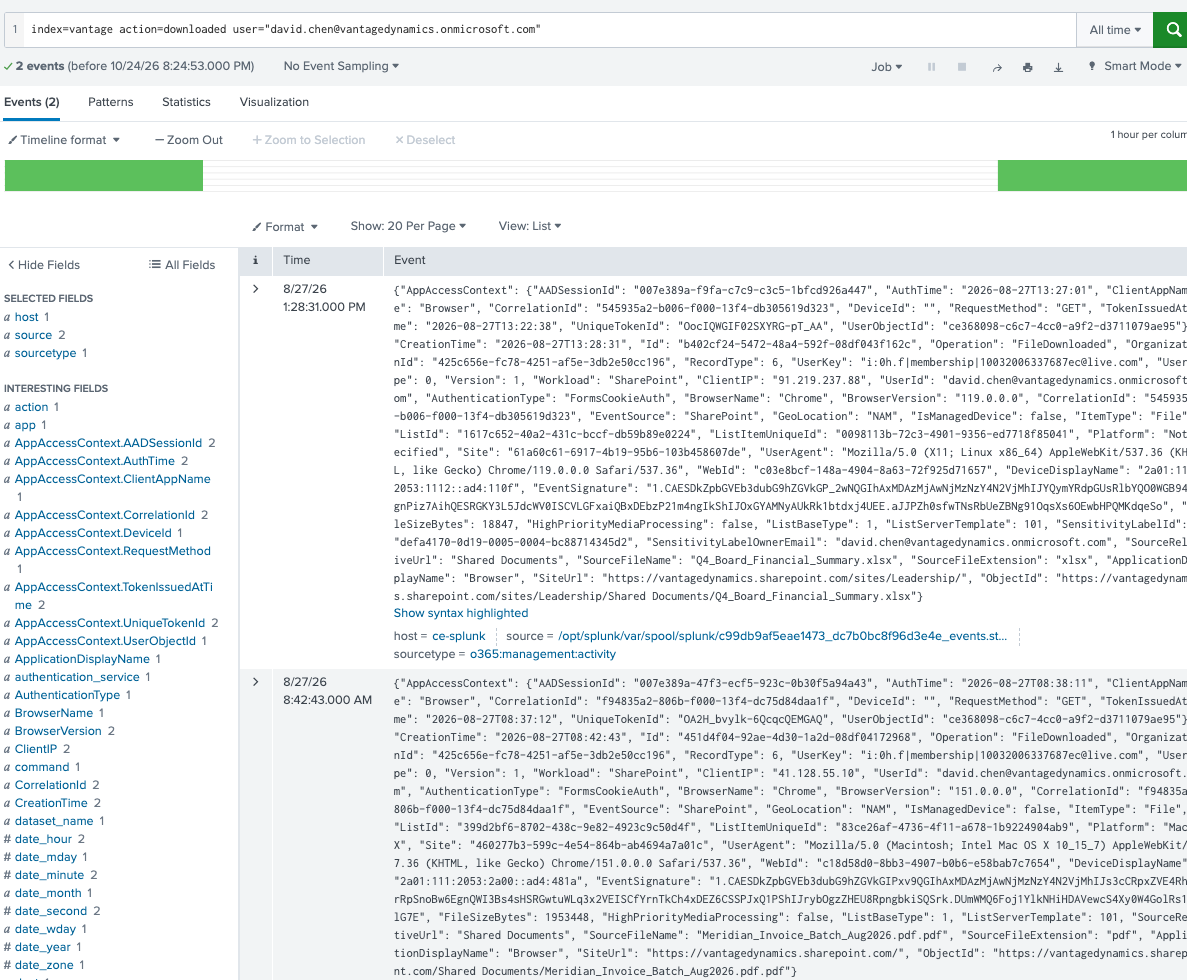
The file the attacker downloaded from David Chen's account was legitimately modified earlier that day. At what time? (Format: YYYY-MM-DD HH:MM:SS)
index=vantage action=downloaded user="david.chen@vantagedynamics.onmicrosoft.com"
index=vantage action=modified user="david.chen@vantagedynamics.onmicrosoft.com" Q4_Board_Financial_Summary.xlsx
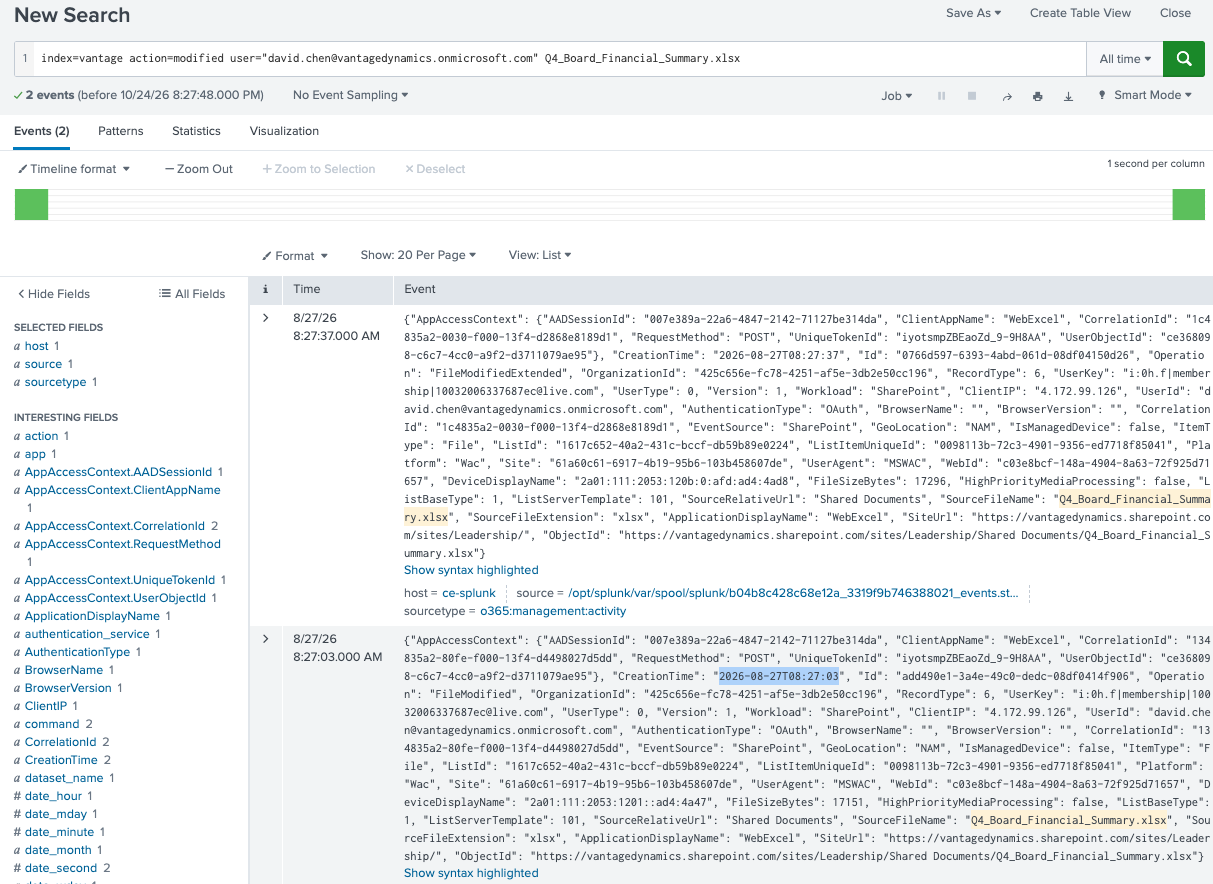
What file stored on the Leadership site had a sensitivity label applied to it by the organization's data governance, prior to the incident? The xlsx file shown in the above attachment
What file did the attacker create an external sharing link for?
index=vantage user="david.chen@vantagedynamics.onmicrosoft.com" action=shared
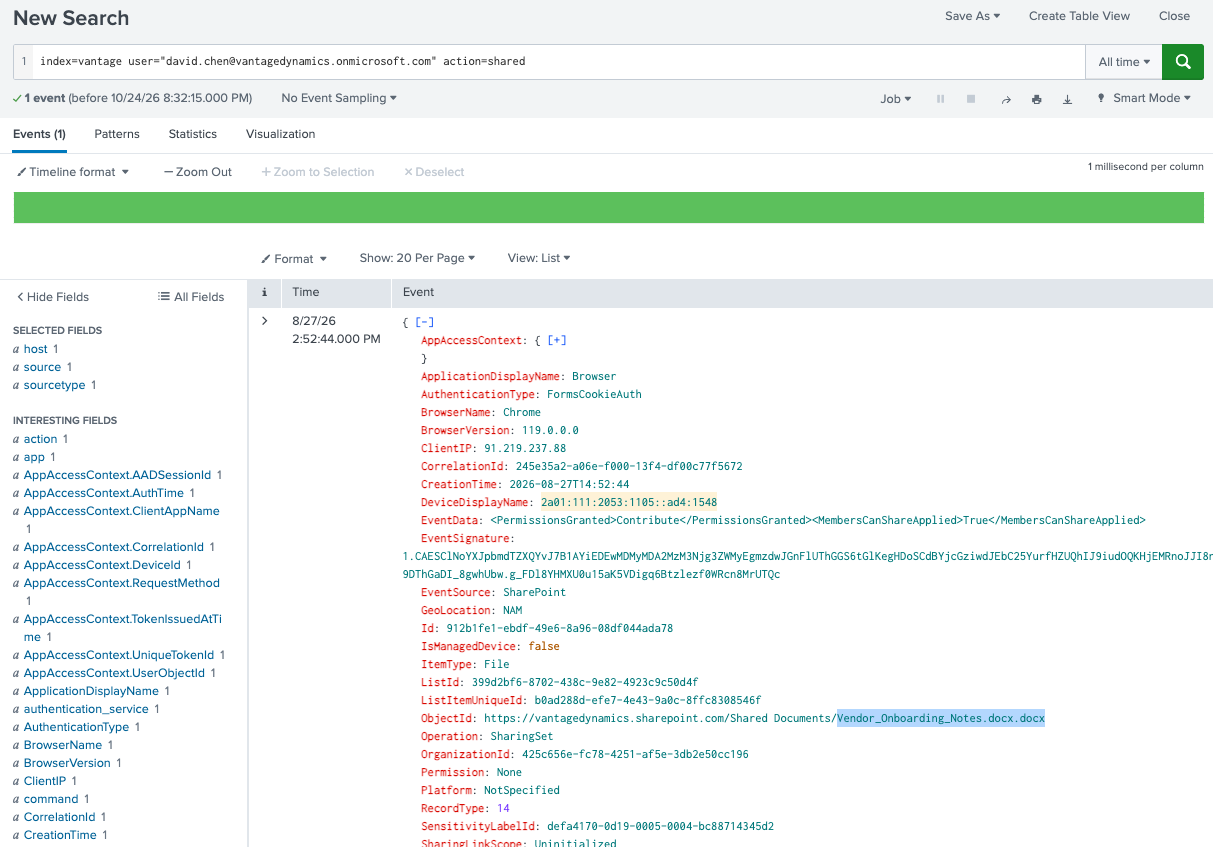
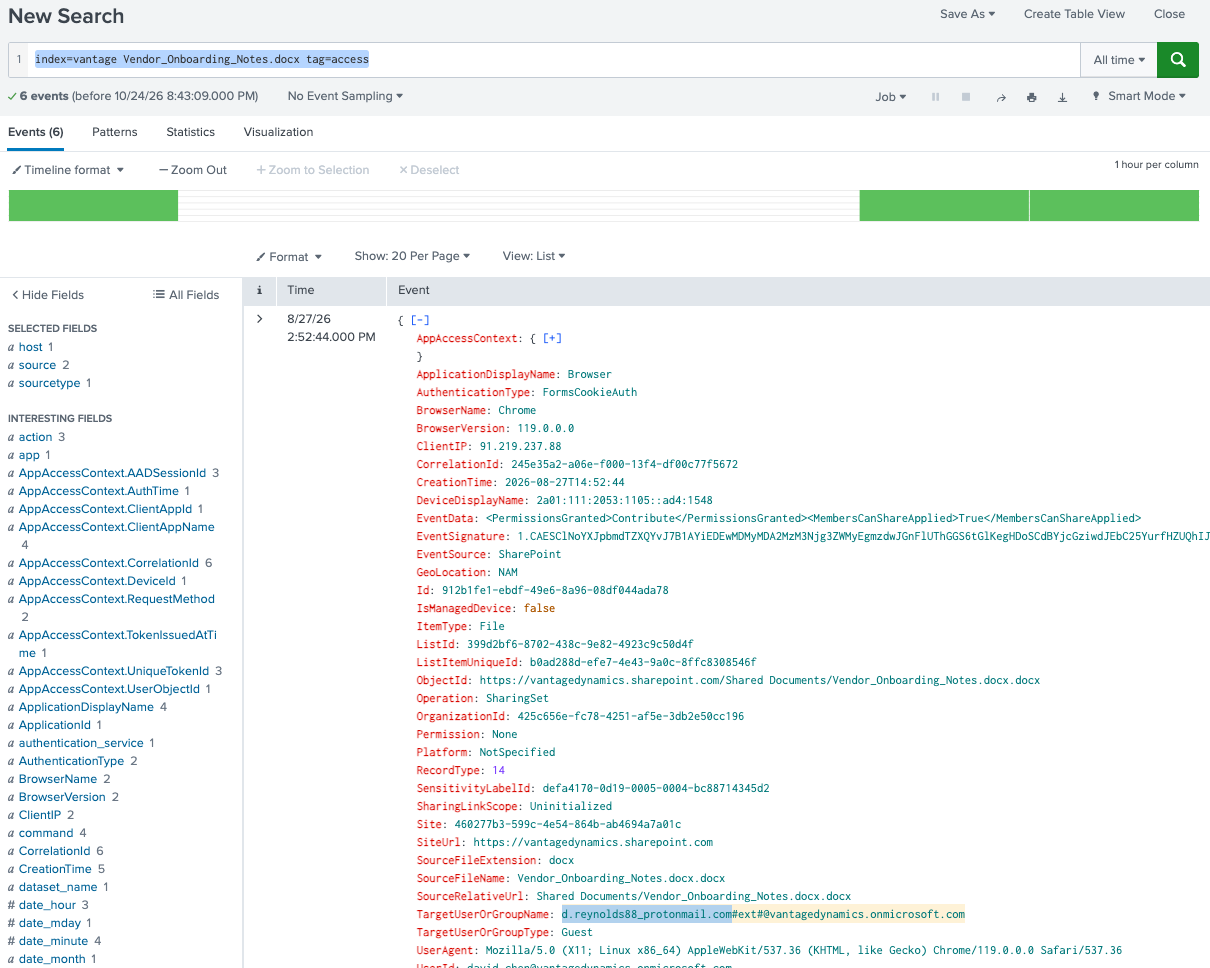
What external email address was granted access to this file?
index=vantage Vendor_Onboarding_Notes.docx tag=access
index=vantage d.reynolds*
search for
d.reynolds88_protonmail.com#ext#@vantagedynamics.onmicrosoft.com
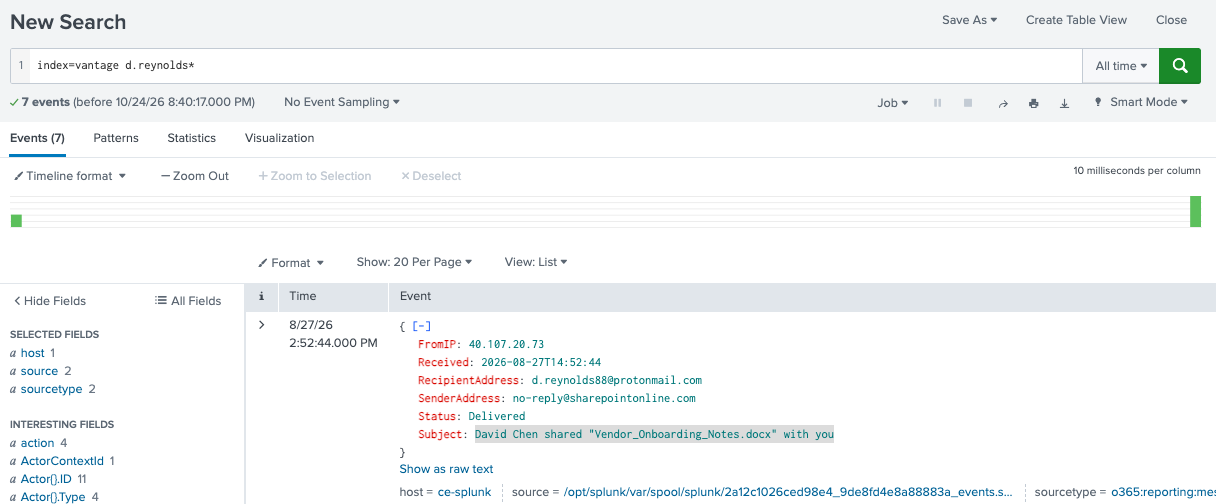
According to the emails, what is the subject line of the notification sent to this external address by the sharing application? the answer shown the attachment above
About the author
- Software Developer | Learning Cybersecurity | Open for roles * If you're in the early stages of your career in software development (student or still looking for an entry-level role) and in need of mentorship, you can reach out to me.
Comments
Join the discussionNo comments yet. Be the first to comment.